Within Case Comparison
Who Did What in the Rome Laboratory Breach?
Pryce was identified early as Datastream Cowboy, while Bevan was viewed as the more capable hacker whose routes and techniques influenced the wider intrusion
On this page
- Pryce's access and early identification
- Bevan's technical reputation and later arrest
- Why shared methods do not prove joint planning
Page outline Jump by section
Introduction
The 1994 breach of the US Air Force’s Rome Laboratory is often described as the work of two British hackers acting together, but the available evidence points to distinct rather than identical roles. Richard Pryce, using the handle Datastream Cowboy, was the first intruder identified by investigators and the person whose online activity they monitored in real time. Mathew Bevan, known as Kuji, was regarded by investigators as the more technically capable participant whose knowledge appeared to help overcome obstacles that had initially defeated Pryce. Although their activities overlapped and they communicated online, the historical record does not establish that they operated as a tightly organised conspiracy. Instead, it shows two individuals with different levels of experience, different investigative profiles and, ultimately, different legal outcomes.[Kujimedia]kujimedia.comKuji Media Corporation Ltd. » Blog Archive » Tales of Digital Crime from the Shadows of Cyberspace – Chapter SixJune 26, 2008…
Pryce’s Access and Early Identification
Richard Pryce became the most visible figure during the initial phase of the Rome Laboratory investigation because investigators were able to identify and monitor him while the intrusions were still under way.
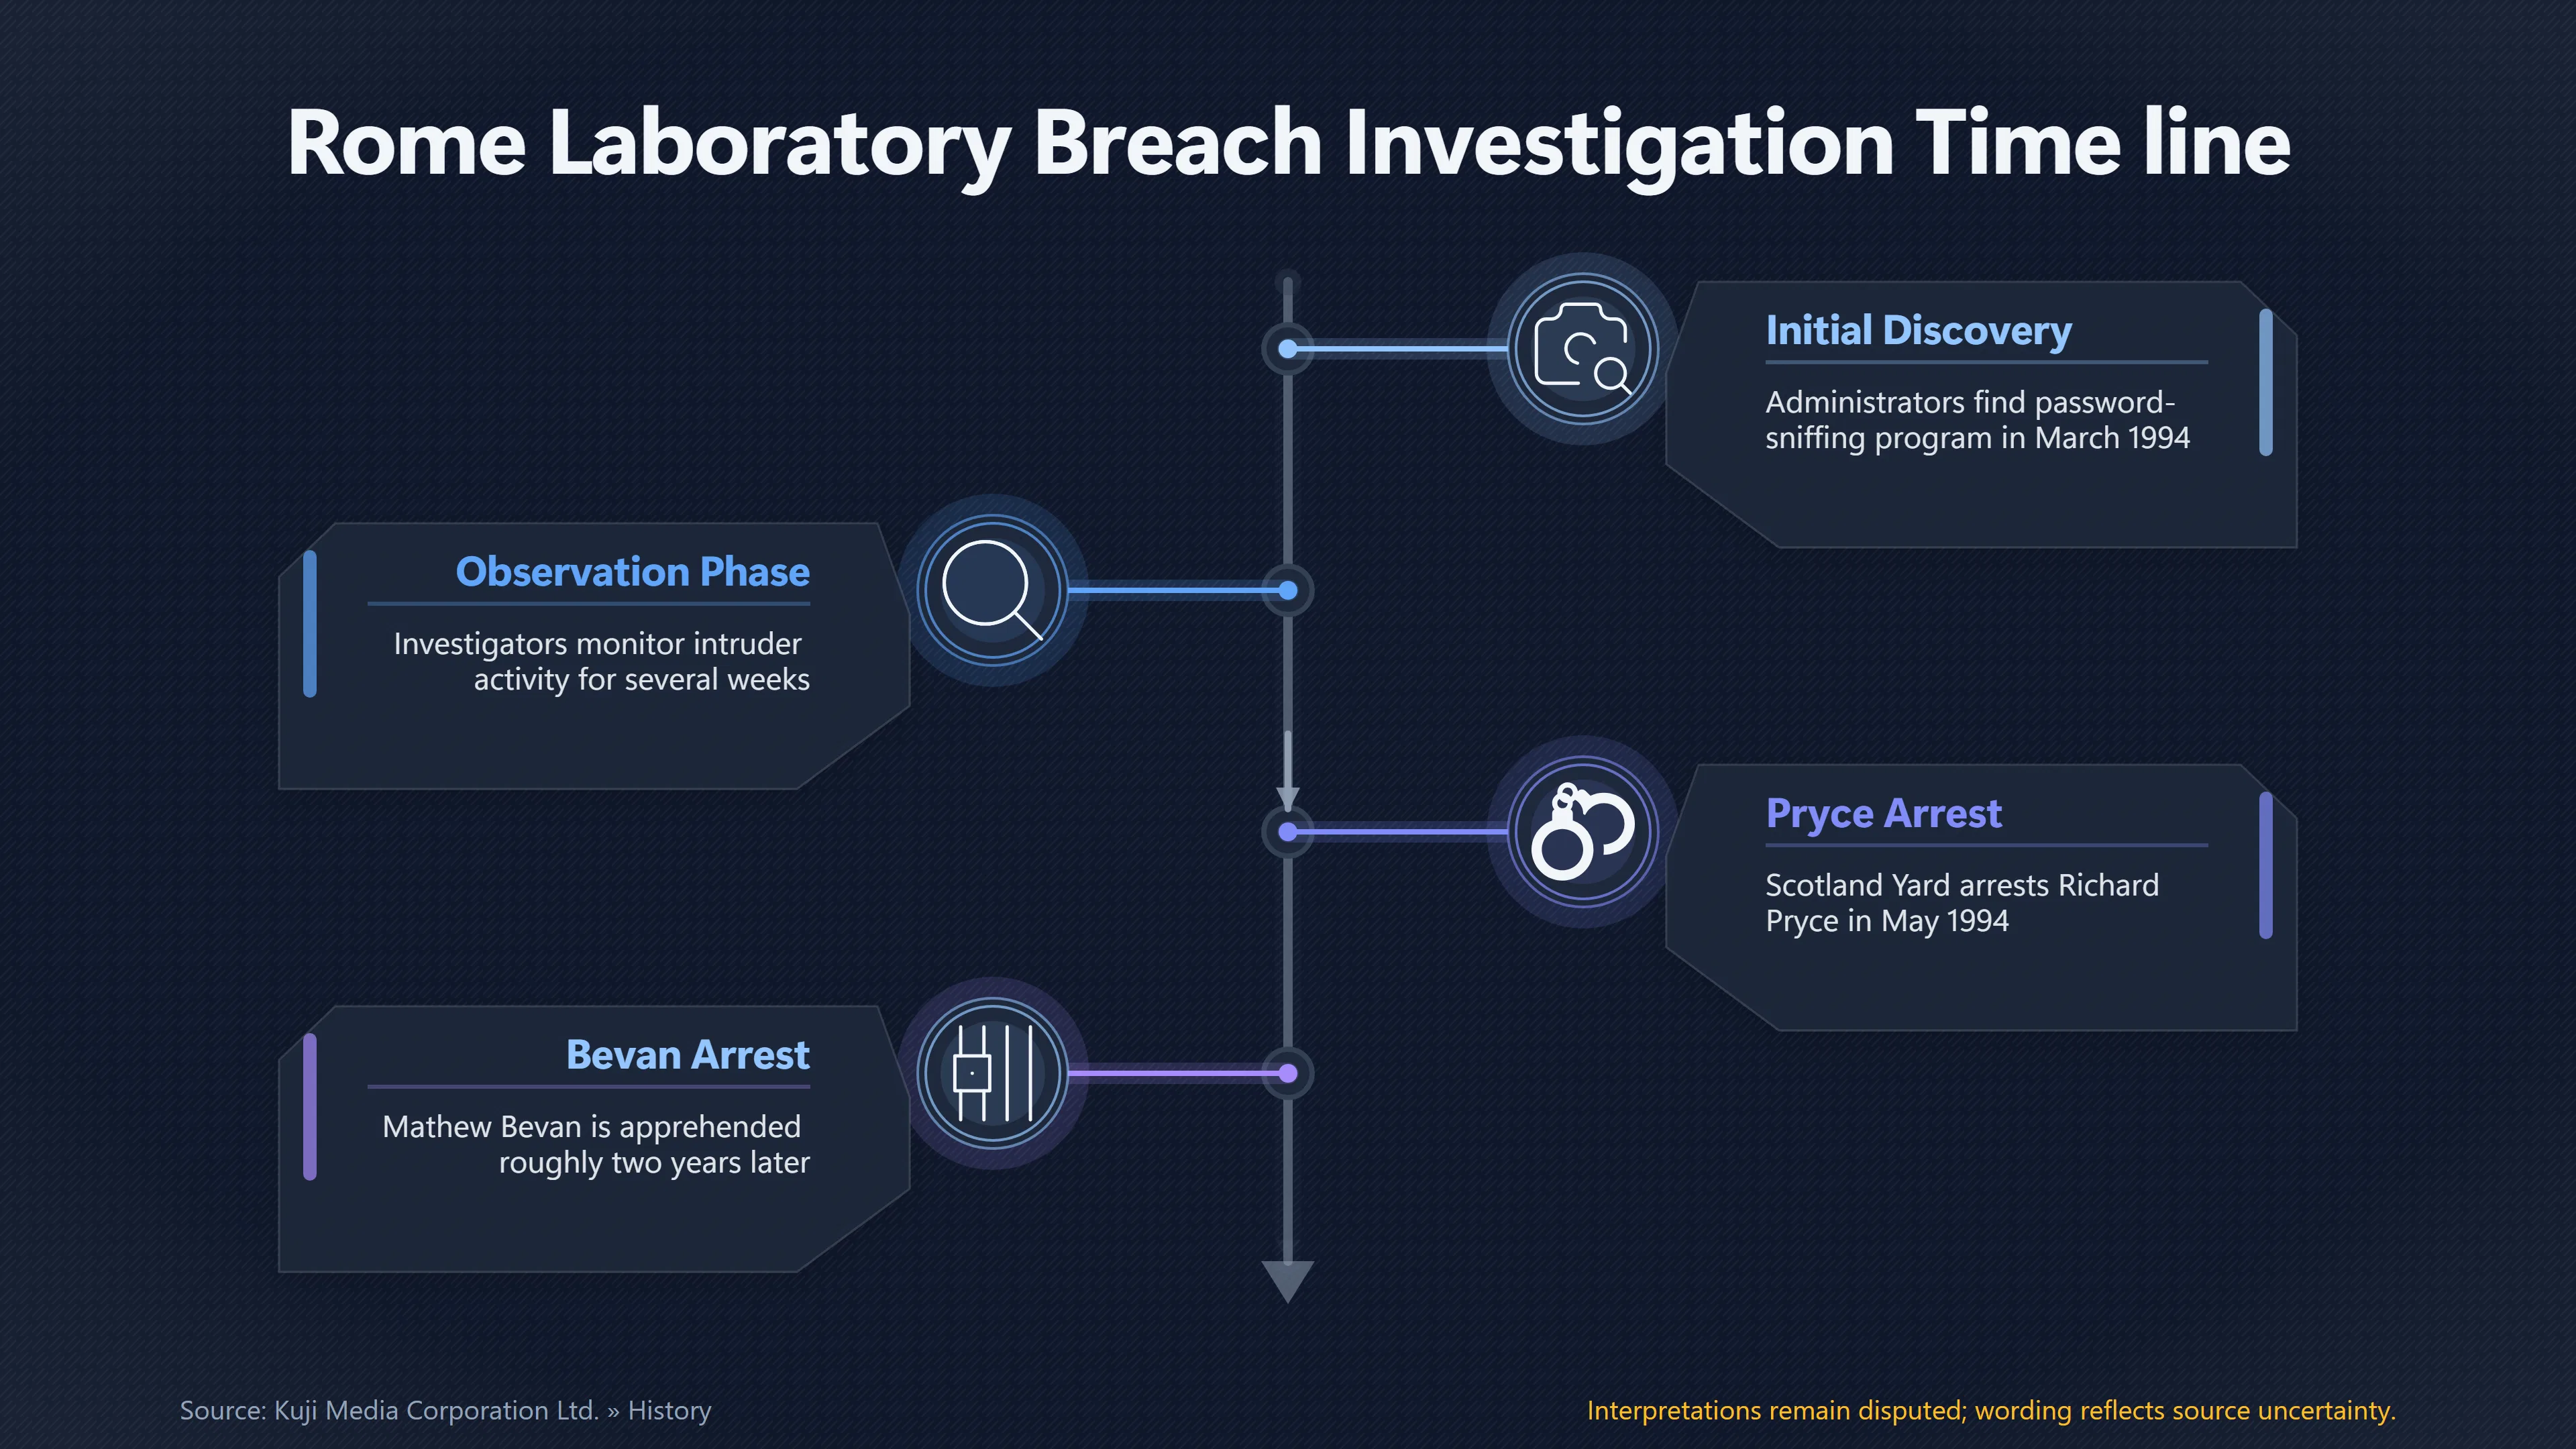
According to Air Force investigative accounts later reproduced in technical case studies, the intrusion first came to light after administrators discovered a password-sniffing program on a Rome Laboratory computer in March 1994. Rather than immediately disconnecting the attacker, investigators chose to observe the activity for several weeks, allowing them to reconstruct attack routes and identify patterns of behaviour. During this period, Datastream Cowboy carried out numerous attempts to access military and research systems through Rome Laboratory and other compromised machines.[Kujimedia]kujimedia.comKuji Media Corporation Ltd. » Blog Archive » Tales of Digital Crime from the Shadows of Cyberspace – Chapter SixJune 26, 2008…
A key reason Pryce was identified relatively quickly was not advanced cyber-forensics alone. Contemporary accounts indicate that investigators benefited from traditional police work, including information from an Internet Relay Chat (IRC) informant and telephone tracing conducted with British authorities. Those methods led Scotland Yard to Pryce, who was arrested in May 1994 while investigators were still following the wider intrusion campaign.[Kujimedia]kujimedia.comKuji Media Corporation Ltd. » Blog Archive » Confessions of a hacker by Mathew BevanJune 26, 2008…
Pryce later pleaded guilty to multiple offences under the UK’s Computer Misuse Act and received a financial penalty rather than a prison sentence. His guilty plea meant that many factual aspects of his unauthorised access were not disputed in court, although broader claims about the significance of the breach remained controversial.[Kujimedia]kujimedia.comKuji Media Corporation Ltd. » HistoryKuji Media Corporation Ltd. » History…
Bevan’s Technical Reputation and Later Arrest
Unlike Pryce, Mathew Bevan was not identified during the initial monitoring operation. Investigators knew only the online alias Kuji and believed they were dealing with a far more elusive individual.
Investigative reports and Bevan’s later recollections agree on one important point: Kuji proved considerably harder to trace. Investigators observed that he spent relatively little time connected, making technical tracing more difficult. Air Force personnel reportedly concluded that Kuji displayed greater operational discipline than Datastream Cowboy, leading some investigators to speculate—incorrectly—that he might be an experienced foreign intelligence operative rather than a young British hacker.[Kujimedia]kujimedia.comKuji Media Corporation Ltd. » Blog Archive » Confessions of a hacker by Mathew BevanJune 26, 2008…
Investigators also noticed a recurring pattern. They observed occasions where Datastream Cowboy unsuccessfully attempted to compromise a target, communicated with Kuji, and then returned to the same system successfully. This sequence became one of the main reasons investigators concluded that Kuji possessed superior technical knowledge and was providing advice or techniques that improved Pryce’s chances of success. The evidence, however, demonstrates observed behaviour rather than direct proof of formal command or organisation.[Kujimedia]kujimedia.comKuji Media Corporation Ltd. » Blog Archive » Confessions of a hacker by Mathew BevanJune 26, 2008…
Bevan was not arrested until 1996, roughly two years after Pryce. His prosecution followed a different course. After numerous hearings and challenges to the prosecution evidence, the Crown ultimately abandoned the case, concluding that continuing proceedings was not in the public interest. As a result, unlike Pryce’s case, there was never a completed criminal trial establishing the full factual allegations against Bevan.[Kujimedia]kujimedia.comKuji Media Corporation Ltd. » HistoryKuji Media Corporation Ltd. » History…
Why Shared Methods Do Not Prove Joint Planning
The Rome Laboratory case is sometimes simplified into a story of two hackers working as a coordinated team. The available evidence supports a more cautious interpretation.
Investigators documented communication between Datastream Cowboy and Kuji, including online conversations that often preceded successful intrusions. Datastream himself reportedly acknowledged that he communicated with Kuji over the Internet and by telephone. These facts support the conclusion that knowledge was exchanged between them.[Kujimedia]kujimedia.comKuji Media Corporation Ltd. » Blog Archive » Tales of Digital Crime from the Shadows of Cyberspace – Chapter SixJune 26, 2008…
However, several important distinctions remain:
- There is no public evidence that they had met in person during the attacks.
- The investigative record does not demonstrate a formal hierarchy or long-term operational plan.
- Much of the inference that Kuji was “directing” events came from investigators’ interpretation of observed patterns rather than direct records of the conversations themselves.
- Bevan later denied acting as Pryce’s tutor in the way described by US investigators, arguing that official accounts exaggerated the relationship and the threat posed by both hackers.[Kujimedia]kujimedia.comKuji Media Corporation Ltd. » Datastream CowboyKuji Media Corporation Ltd. » Datastream Cowboy…
This distinction matters because later retellings often transform a collaborative exchange of techniques into an organised conspiracy. The surviving documentary record supports communication and overlapping activity but falls short of proving detailed joint planning for every intrusion.
What Their Different Roles Reveal About the Rome Laboratory Breach
Comparing Bevan and Pryce illustrates how investigators viewed different forms of participation within the same intrusion campaign.
Pryce became the operational focus because his activities generated the observable trail that investigators could follow. His attacks, routing methods and eventual identification enabled authorities to uncover the wider compromise of Rome Laboratory and connected systems.[Kujimedia]kujimedia.comKuji Media Corporation Ltd. » Blog Archive » Tales of Digital Crime from the Shadows of Cyberspace – Chapter SixJune 26, 2008…
Bevan, by contrast, acquired a reputation as the technically stronger figure. Investigators attributed improved intrusion techniques and successful follow-up attacks to his influence, while simultaneously struggling to establish his real identity. That reputation shaped contemporary concerns about the breach, even though the legal case against him never reached a judicial determination.[Kujimedia]kujimedia.comKuji Media Corporation Ltd. » Blog Archive » Confessions of a hacker by Mathew BevanJune 26, 2008…
Taken together, the evidence suggests complementary rather than identical roles: Pryce was the readily traceable intruder whose actions exposed the scale of the compromise, while Bevan was perceived as the more sophisticated participant whose expertise may have influenced how some attacks were carried out. The documented exchange of methods helps explain why their names are linked in the history of the Rome Laboratory breach, but it should not be treated as conclusive proof that every intrusion resulted from a centrally planned or tightly directed partnership.[Kujimedia]kujimedia.comKuji Media Corporation Ltd. » Blog Archive » Tales of Digital Crime from the Shadows of Cyberspace – Chapter SixJune 26, 2008…
Amazon book picks
Further Reading
Books and field guides related to Who Did What in the Rome Laboratory Breach?. Use these as the next step if you want deeper reading beyond the article.

Cyberpunk: Outlaws and Hackers on the Computer Frontier
Using the exploits of three international hackers, "Cyberpunk" provides a fascinating tour of a bizarre subculture populated by outlaws w...
Underground: Tales of Hacking, Madness and Obsession on the E...
Suelette Dreyfus and her co-author, WikiLeaks founder Julian Assange, tell the extraordinary true story of the computer underground, and...
The Hacker Crackdown: Law and Disorder on the Electronic Fron...
The bestselling cyberpunk author "has produced by far the most stylish report from the computer outlaw culture since Steven Levy's Hacker...
eBay marketplace picks
Marketplace Samples
Live-tested eBay searches with available results related to this page.
Selected fromretro computer model oneBay.co.uk.
Endnotes
1.
Source: kujimedia.com
Link:https://www.kujimedia.com/tales-of-digital-crime-from-the-shadows-of-cyberspace-chapter-six/
Source snippet
Kuji Media Corporation Ltd. » Blog Archive » Tales of Digital Crime from the Shadows of Cyberspace – Chapter SixJune 26, 2008...
Published: June 26, 2008
2.
Source: kujimedia.com
Link:https://www.kujimedia.com/confessions-of-a-hacker-by-mathew-bevan/
Source snippet
Kuji Media Corporation Ltd. » Blog Archive » Confessions of a hacker by Mathew BevanJune 26, 2008...
Published: June 26, 2008
3.
Source: kujimedia.com
Title: Kuji Media Corporation Ltd. » History
Link:https://www.kujimedia.com/articles/
Source snippet
Kuji Media Corporation Ltd. » History...
4.
Source: kujimedia.com
Title: Kuji Media Corporation Ltd. » Datastream Cowboy
Link:https://www.kujimedia.com/tag/datastream-cowboy/
Source snippet
Kuji Media Corporation Ltd. » Datastream Cowboy...
5.
Source: kujimedia.com
Title: Kuji Media Corporation Ltd. » Datastream Cowboy
Link:https://www.kujimedia.com/tag/datastream-cowboy/page/2/
Source snippet
Kuji Media Corporation Ltd. » Datastream Cowboy...
6.
Source: kujimedia.com
Title: Kuji Media Corporation Ltd. » Blog Archive » THE SCHOOLBOY SPY. Sunday Times
Link:https://www.kujimedia.com/the-schoolboy-spy-sunday-times/
7.
Source: kujimedia.com
Title: Kuji Media Corporation Ltd. » Richard Pryce
Link:https://www.kujimedia.com/tag/richard-pryce/page/2/
Additional References
8.
Source: sciencedirect.com
Link:https://www.sciencedirect.com/science/article/pii/S0379073826001544
Source snippet
Decommissioning and relocation of a Forensic Science laboratory A Phased Approach to Closure, Continuity, and Sustainability - ScienceDir...
9.
Source: korben.info
Title: Deux ados cherchant des OVNIS ont failli lancer la WW3
Link:https://korben.info/kuji-datastream-cowboy-pentagone-hack-1996-histoire-complete.html
Source snippet
July 25, 2025 — Image X-Files - La série qui a inspiré toute une génération de hackers conspirationnistes Et là, c'est le moment "e...
Published: July 25, 2025
10.
Source: onr.org.uk
Link:https://www.onr.org.uk/publications/regulatory-reports/site-specific-reports/inspection-records/2026/06/sellafield-inspection-id-53287
Source snippet
Inspection ID: 53287 | Office for Nuclear RegulationJune 2, 2026 — The purpose of LC7 is to ensure that the licensee implements adequate...
Published: June 2, 2026
11.
Source: youtube.com
Title: A Tale of Two UFO Hackers: Matthew Bevan & Gary Mc Kinnon
Link:https://www.youtube.com/watch?v=rksYZZgSPcY
Source snippet
Who Is The Most Dangerous Hacker Ever? (Tier List)...
12.
Source: onr.org.uk
Link:https://www.onr.org.uk/publications/regulatory-reports/site-specific-reports/inspection-records/2020/01/compliance-inspection-of-licence-conditions-7-incidents-on-the-site-and-36-organisational-capability
13.
Source: trulyadventure.us
Link:https://www.trulyadventure.us/the-hacker
14.
Source: afrl.af.mil
Link:https://www.afrl.af.mil/News/Article-Display/Article/3203251/afrl-celebrates-unified-science-and-technology-enterprise/
15.
Source: af.mil
Link:https://www.af.mil/News/Article-Display/Article/3205018/afrl-celebrates-unified-science-and-technology-enterprise/
16.
Source: youtube.com
Title: Who Is The Most Dangerous Hacker Ever? (Tier List)
Link:https://www.youtube.com/watch?v=z7OjzYT_-Zo
Source snippet
Gary Mckinnon: The Hacker Who Found UFOs...
17.
Source: airandspaceforces.com
Link:https://www.airandspaceforces.com/article/0397sweepers/