Within Access Methods
Lateral Movement Rou
One of the most important features of the Gary McKinnon case was that he did not need to connect directly to every military or NASA computer from his home internet connection.
Page outline Jump by section
Introduction
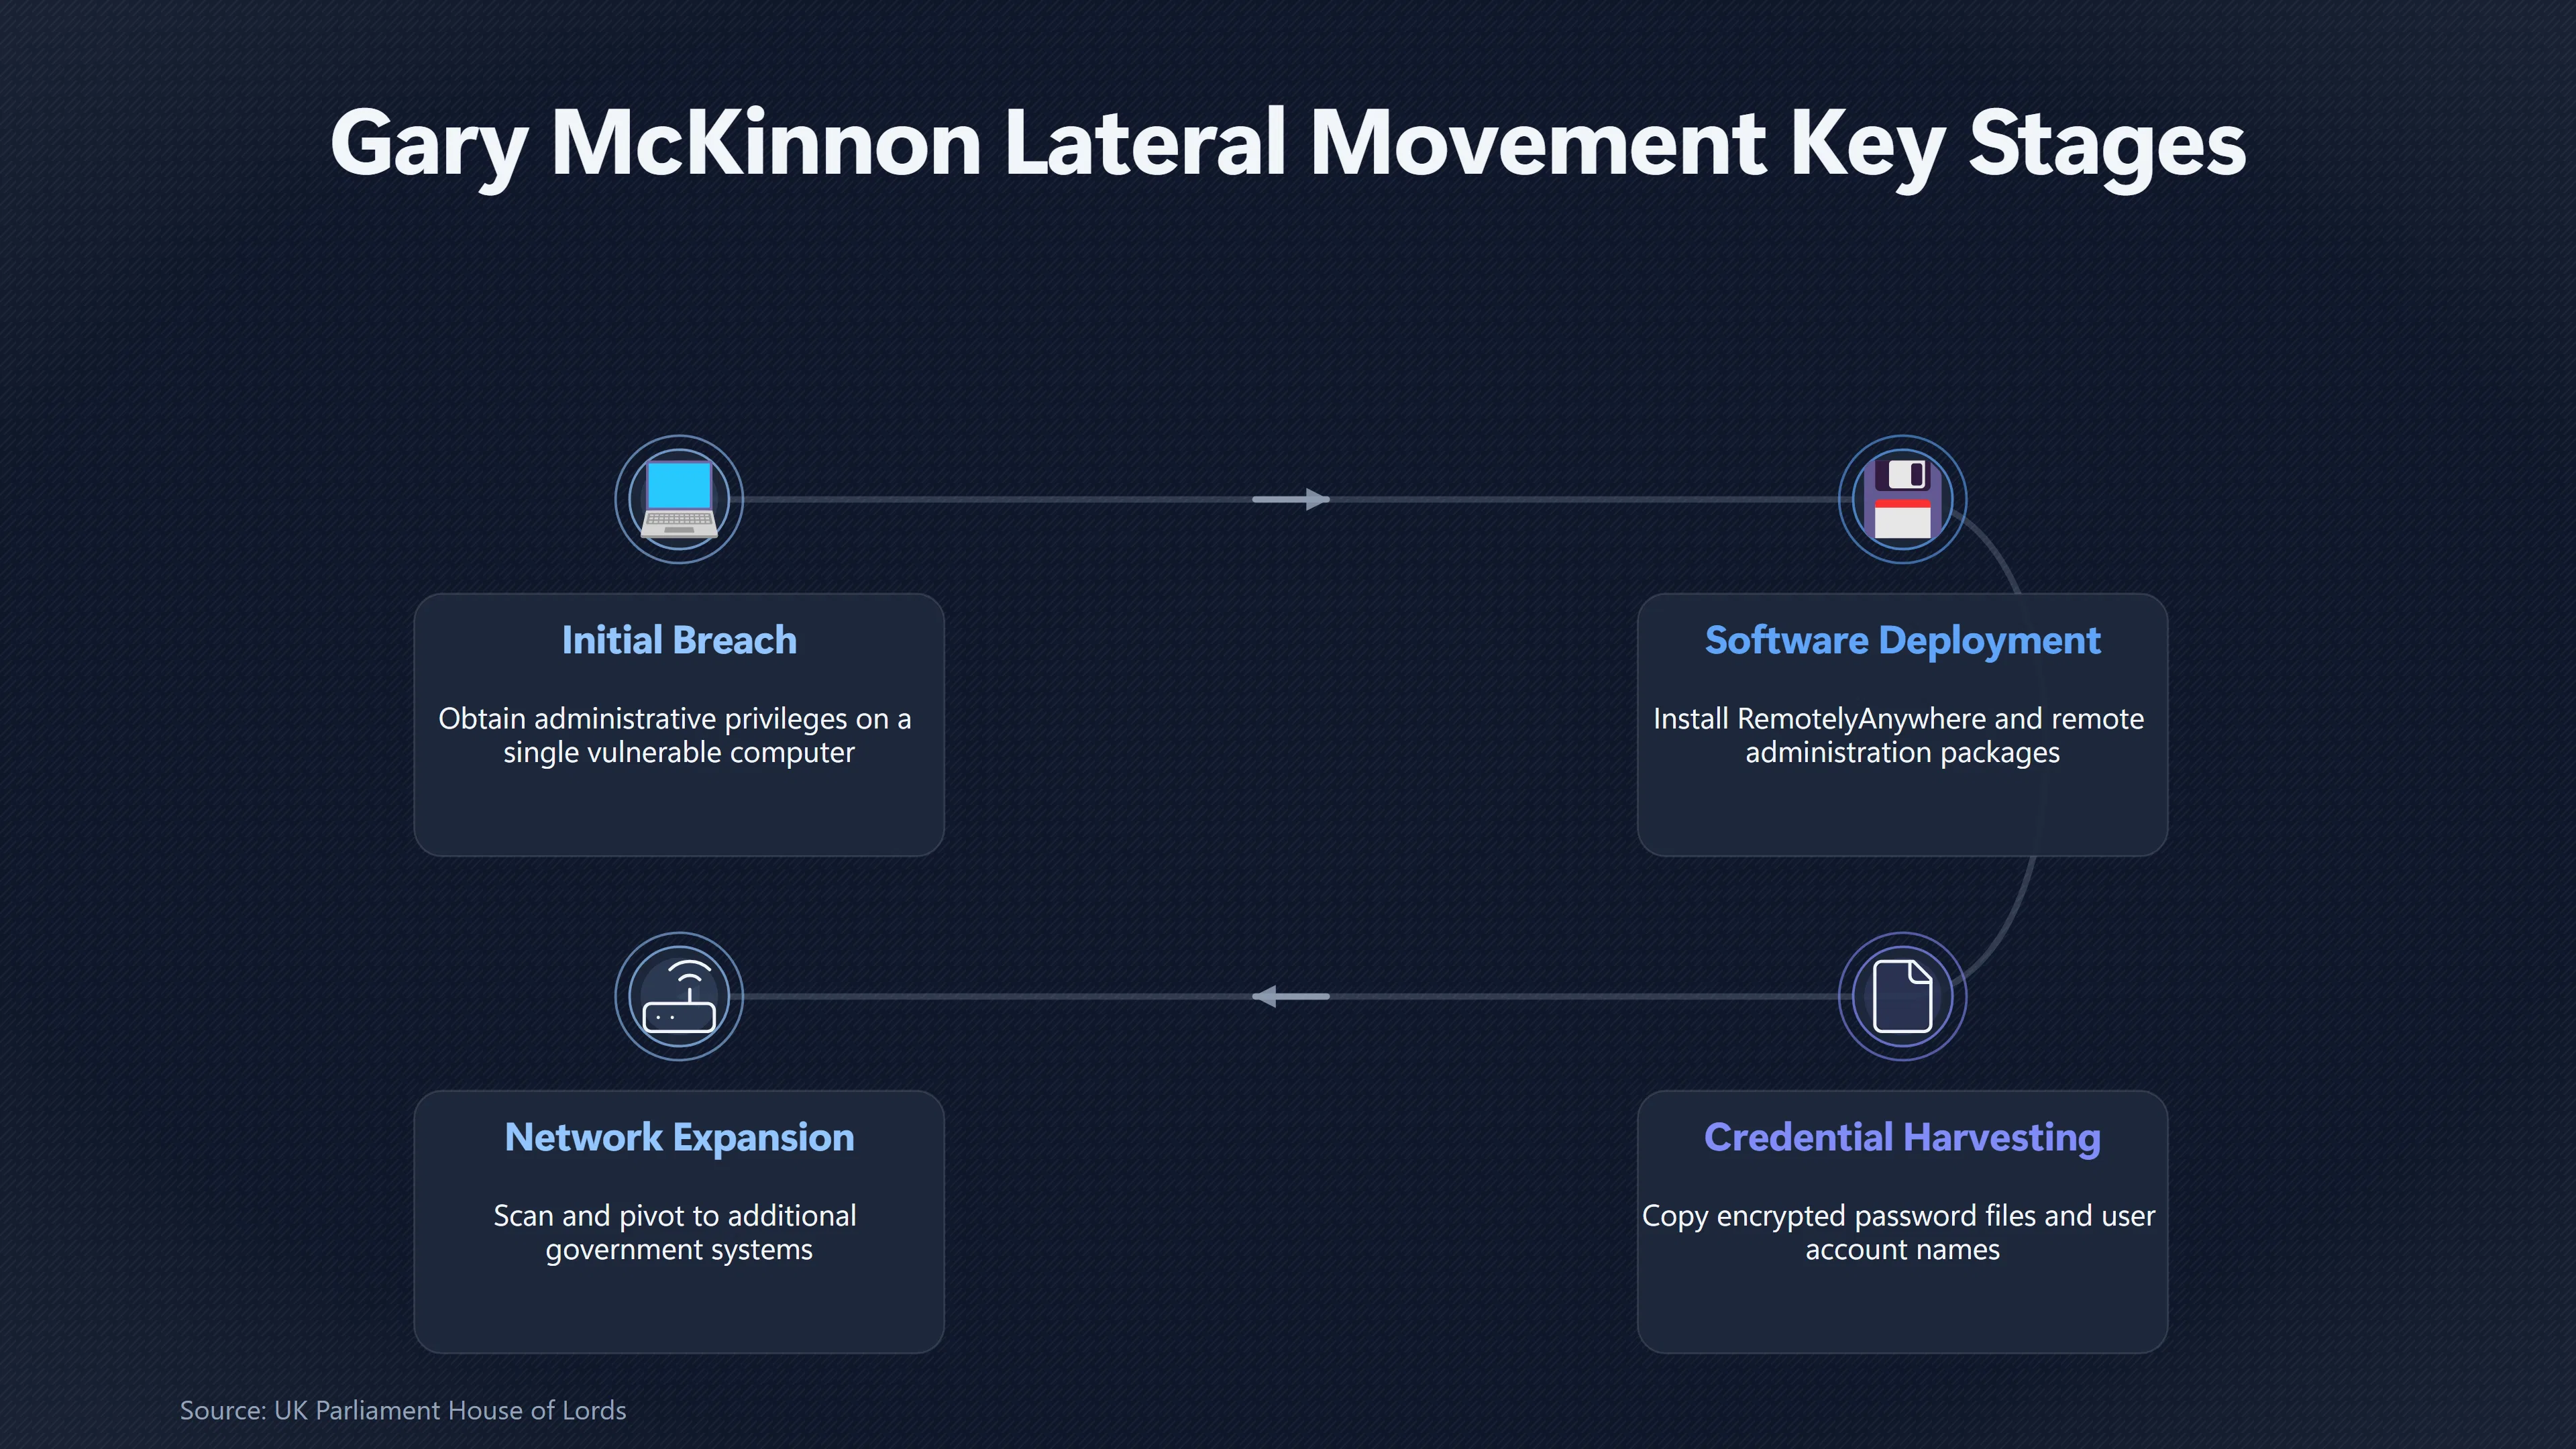
One of the most important features of the Gary McKinnon case was that he did not need to connect directly to every military or NASA computer from his home internet connection. According to US indictments and the House of Lords judgment summarising the allegations, once he had administrative access to a vulnerable computer he could use that trusted machine as a new starting point for finding additional systems, installing remote-access software, copying account information and moving deeper into connected government networks.[UK Parliament]publications.parliament.ukUK Parliament House of LordsUK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008…
This mechanism—known today as lateral movement—helps explain why a single poorly protected computer could become the gateway to many others. Rather than repeatedly attacking isolated internet-facing systems, a compromised host effectively became an internal platform from which other military and NASA computers were easier to discover and reach.
Using a Compromised Host as a New Launch Point
The allegations against McKinnon describe a progression rather than a series of unrelated break-ins. After obtaining administrative privileges on one computer, he allegedly installed the commercial remote administration package RemotelyAnywhere together with other software that enabled continued access and concealed his activities. From that position he could search for additional computers that shared the same weaknesses.[UK Parliament]publications.parliament.ukUK Parliament House of LordsUK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008…
The House of Lords judgment states that the installed software allowed him to scan more than 73,000 US government computers for other susceptible systems. It further explains that he was able to “lever himself from network to network”, illustrating that each successful compromise increased his ability to identify and reach further machines.[UK Parliament]publications.parliament.ukUK Parliament House of LordsUK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008…
This mattered because an internal computer occupies a different position from an external attacker. Once a machine is trusted by its surrounding network, communications originating from it may reach servers, administrative tools or shared resources that are not directly exposed to the public internet. Even where individual systems remained separately protected, an attacker operating from inside the environment often has better visibility of addresses, services and network relationships than someone scanning from outside.
The Role of Copied Usernames and Password Files
Administrative access also enabled the alleged theft of authentication data. According to the US indictments, McKinnon copied files containing usernames and encrypted passwords from compromised systems, including approximately 950 passwords from servers connected to the Naval Weapons Station Earle network. The House of Lords judgment similarly records allegations that account names and encrypted password files were copied from multiple Army, Navy and NASA computers.[Department of Justice]justice.govDepartment of JusticeBritish National Charged with Hacking Into N.J. Naval Weapons Station Computers, Disabling Network After Sept. 11 (N…
These password files did not necessarily reveal every password immediately. However, they provided valuable information in several ways:
- They identified legitimate user and administrator accounts.
- They could potentially be subjected to password-cracking techniques offline.
- They revealed which credentials existed across different systems.
- They reduced the need to rely solely on discovering new vulnerable internet-facing machines.
The Virginia indictment also alleges that after copying password files from an Army computer, McKinnon installed tools intended to obtain unauthorised access to additional computers. This illustrates that credential collection was treated as part of expanding access rather than an isolated act of data theft.[Wikisource]en.wikisource.orgUS v Gary Mc Kinnon IndictmentUS v Gary McKinnon Indictment - Wikisource, the free online library…
Why Broad Internal Connectivity Increased the Damage
Government organisations rarely operate as collections of completely isolated computers. Military bases, administrative offices and research facilities depend on networks that allow systems to exchange information, authenticate users and manage shared services.
The McKinnon allegations suggest that weaknesses in this internal connectivity amplified the consequences of the initial compromise. Once one machine became available, it could serve as:
- a platform for discovering additional hosts;
- a trusted location from which to launch further scans;
- a repository of account information useful elsewhere;
- a persistent access point through installed remote-control software.
This helps explain how prosecutors alleged that McKinnon ultimately accessed 97 computers across the US Army, Navy, Air Force, Department of Defense and NASA despite beginning with far fewer entry points. The significance lay less in sophisticated exploitation than in repeatedly extending access from one compromised system to the next.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 2002)…
Why Internal Trust Was Such a Critical Weakness
Modern cybersecurity guidance often assumes that internal network traffic should not automatically be trusted. During the period covered by the McKinnon allegations, many enterprise networks relied much more heavily on the assumption that machines already inside the organisation were comparatively trustworthy.
As a result, compromising a single administrative workstation or server could expose:
- network shares;
- directory information;
- administrative utilities;
- password databases;
- additional remote management services.
The McKinnon case became a well-known example because prosecutors argued that exactly this sequence occurred: an initial compromise led to administrative control, administrative control enabled credential collection and remote administration, and those capabilities made further compromises progressively easier.[UK Parliament]publications.parliament.ukUK Parliament House of LordsUK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008…
What the Mechanism Revealed
The importance of this aspect of the case extends beyond the specific allegations against McKinnon. It demonstrated that the greatest risk did not necessarily come from breaching dozens of independent systems individually. Instead, one inadequately protected computer could become a stepping stone into many others.
For that reason, the case is frequently discussed as an illustration of lateral movement: the process by which an attacker converts one successful intrusion into wider access by exploiting trusted network relationships and harvested credentials. The allegations that McKinnon scanned from compromised hosts, copied password files and used installed remote-access software all fit this mechanism, helping explain how relatively ordinary security weaknesses could produce access across multiple military and NASA networks.[parliament.uk]publications.parliament.ukUK Parliament House of LordsUK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008…
Amazon book picks
Further Reading
Books and field guides related to Lateral Movement Rou. Use these as the next step if you want deeper reading beyond the article.
The Cuckoo's Egg
This is the true story of how a systems manager at Lawrence Berkeley Lab singlehandedly tracked down and helped capture a computer hacker...
Windows Internals
The definitive guide–fully updated for Windows 10 and Windows Server 2016 Delve inside Windows architecture and internals, and see how co...
Network Security Assessment
Covers offensive technologies by grouping and analyzing them at a higher level--from both an offensive and defensive standpoint--helping...
Hacking: The Art of Exploitation, 2nd Edition
Hacking is the art of creative problem solving, whether that means finding an unconventional solution to a difficult problem or exploitin...
eBay marketplace picks
Marketplace Samples
Live-tested eBay searches with available results related to this page.
Selected fromhacker t shirt oneBay.co.uk.
Endnotes
1.
Source: publications.parliament.uk
Title: UK Parliament House of Lords
Link:https://publications.parliament.uk/pa/ld200708/ldjudgmt/jd080730/mckinn-1.htm
Source snippet
UK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008...
Published: July 30, 2008
2.
Source: justice.gov
Link:https://www.justice.gov/archive/criminal/cybercrime/press-releases/2002/mckinnonIndict.htm
Source snippet
Department of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 2002)...
Published: November 12, 2002
3.
Source: justice.gov
Link:https://www.justice.gov/archive/criminal/cybercrime/press-releases/2002/mckinnonIndict2.htm
Source snippet
Department of JusticeBritish National Charged with Hacking Into N.J. Naval Weapons Station Computers, Disabling Network After Sept. 11 (N...
4.
Source: en.wikisource.org
Title: US v Gary Mc Kinnon Indictment
Link:https://en.wikisource.org/wiki/US_v_Gary_McKinnon_Indictment
Source snippet
US v Gary McKinnon Indictment - Wikisource, the free online library...
5.
Source: parliament.uk
Title: Update following cyber security incident
Link:https://www.parliament.uk/mps-lords-and-offices/offices/commons/media-relations-group/news/update-following-cyber-attack/
Source snippet
UK ParliamentJuly 20, 2017 — UPDATE FOLLOWING CYBER SECURITY INCIDENT 20 July 2017 Jul 20 2017 Image: PC-Westminster-palace-standard.png...
Published: July 20, 2017
6.
Source: hansard.parliament.uk
Title: uk Commons Chamber
Link:https://hansard.parliament.uk/html/Commons/2009-12-01/CommonsChamber
Source snippet
David Burrowes (Enfield, Southgate) (Con) (Urgent Question): To ask the Secretary of State for the Home Department if he will make a stat...
7.
Source: GOV.UK
Title: latest on gary mckinnon case
Link:https://www.gov.uk/government/news/latest-on-gary-mckinnon-case
Source snippet
on Gary McKinnon case - GOV.UKNovember 4, 2010 — LATEST ON GARY MCKINNON CASE Find out the latest position on the Glasgow-born systems ad...
Published: November 4, 2010
Additional References
8.
Source: sooperkanoon.com
Link:https://sooperkanoon.com/case/amp/945113/mckinnon-appellant-vs-government-respondents
Source snippet
GOVERNMENT OF THE UNITED STATES OF AMERICA (RESPONDENTS) AND ANOTHER - COURT JUDGMENT SooperKanoon Citation | sooperkanoon.com/945113 Cou...
9.
Source: vlex.co.uk
Title: Mc Kinnon v United States of America
Link:https://vlex.co.uk/vid/mckinnon-v-usa-818719549
Source snippet
McKinnon v United States of America - vLex United KingdomJuly 30, 2008 — MCKINNON V UNITED STATES OF AMERICA [Jurisdiction]({{ 'jurisdiction/' | relative_url }}) | England & Wal...
Published: July 30, 2008
10.
Source: youtube.com
Title: Detecting Lateral Movement with Splunk
Link:https://www.youtube.com/watch?v=a47KDhIOUJw
Source snippet
This list provides directly relevant documentaries and technical breakdowns explaining how attackers use initial access to pivot and move...
11.
Source: youtube.com
Title: Hacking for UFOs and fighting for his life. Who is Gary Mc Kinnon?
Link:https://www.youtube.com/watch?v=OImdnvQx7sQ
Source snippet
Lateral Movement Explained | How Hackers Quietly Take Over Networks...
12.
Source: youtube.com
Title: Lateral Movement Explained | How Hackers Quietly Take Over Networks
Link:https://www.youtube.com/watch?v=fDy3G5BBkVI
Source snippet
How Hackers Pivot with SSH (Dynamic Port Forwarding Explained)...
13.
Source: casemine.com
Link:https://www.casemine.com/judgement/uk/5a8ff75e60d03e7f57eabd29
14.
Source: casemine.com
Link:https://www.casemine.com/judgement/uk/5a8ff75e60d03e7f57eabd29/amp
15.
Source: theguardian.com
Link:https://www.theguardian.com/technology/2002/nov/13/hacking.internetcrime
16.
Source: youtube.com
Title: The Man Who Hacked the U.S. Government
Link:https://www.youtube.com/watch?v=ND0zQX1rGdg
Source snippet
Hacking for UFOs and fighting for his life. Who is Gary McKinnon?...
17.
Source: theguardian.com
Link:https://www.theguardian.com/technology/2008/jun/16/hacking.internationalcrime