Within Access Methods
How Mass Scanning Found the Weakest Machines
McKinnon searched tens of thousands of government internet addresses to find the small fraction of Windows systems that exposed usable entry points.
On this page
- How address range scanning narrowed the search
- Why most systems resisted while a few failed
- What the scanning scale does and does not prove
Page outline Jump by section
Introduction
Gary McKinnon’s method for finding vulnerable United States government computers relied far more on systematic searching than on defeating sophisticated security controls. According to court records, indictments and contemporary reporting, he used automated tools to examine very large ranges of internet-connected government addresses, looking for the relatively small number of Windows systems that exposed administrative access through weak or missing authentication. The key lesson from the case is that mass scanning does not imply that every machine was vulnerable. Instead, it demonstrates how a determined attacker could search at scale until ordinary security failures appeared, then use those isolated weaknesses as entry points into larger networks.[parliament.uk]publications.parliament.ukUK Parliament House of LordsUK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008…
How address-range scanning narrowed the search
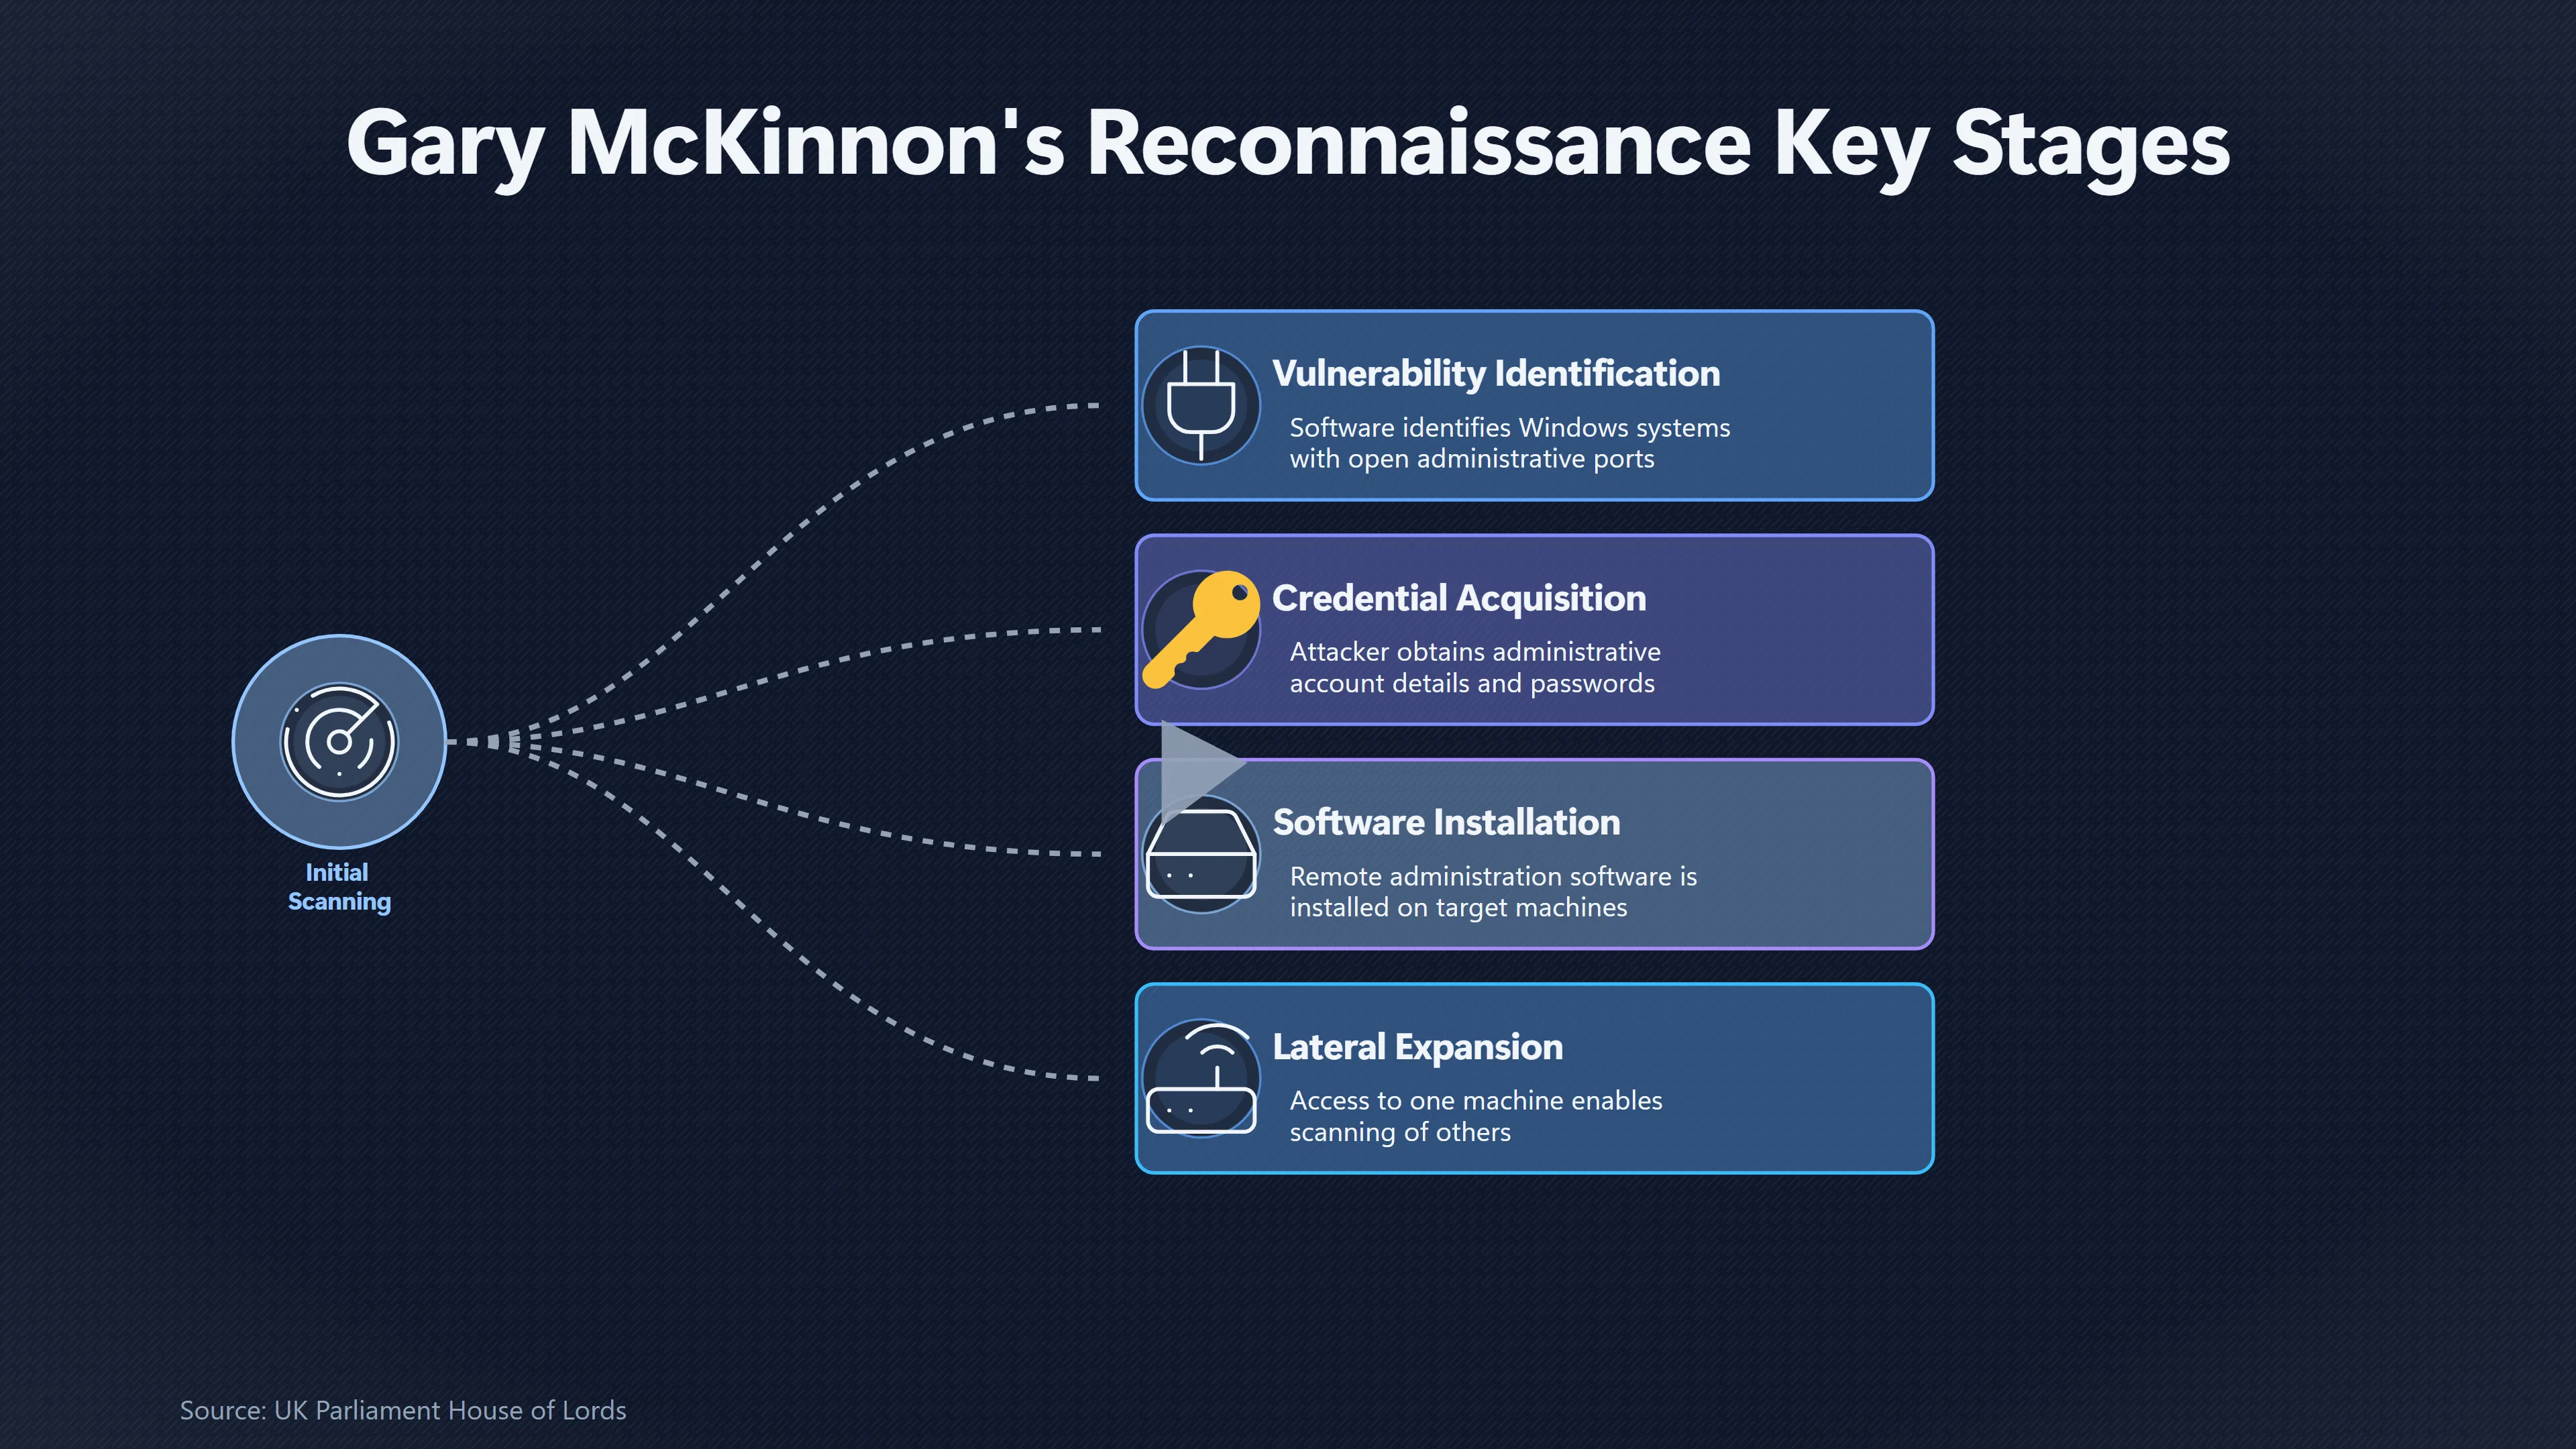
McKinnon’s alleged campaign began with reconnaissance rather than immediate intrusion. Instead of targeting individual computers one by one, prosecutors said he scanned large numbers of hosts within United States military and NASA address ranges to identify machines exposing Microsoft Windows services to the public internet. Automated scanning dramatically reduced the effort required to locate systems that might accept remote administrative connections.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 2002)…
This approach reflected an important feature of internet-connected networks at the time. Large organisations often owned extensive blocks of public IP addresses. An automated scanner could rapidly test whether each address responded on particular Windows networking ports or remote administration services. Most systems either did not respond or rejected unauthorised access, but the software recorded the comparatively small number that appeared reachable for closer examination. Contemporary investigators stated that McKinnon used publicly available automated software rather than a previously unknown technical breakthrough.[WIRED]wired.comBrit Fights Hacking Extradition | WIREDBrit Fights Hacking Extradition | WIRED…
The House of Lords’ summary of the extradition case describes this progression in practical terms. It states that McKinnon identified government computers with open Microsoft Windows connections, obtained administrative account details and passwords, installed remote administration software after gaining access, and subsequently scanned more than 73,000 government computers to locate further systems susceptible to the same weaknesses. The scanning therefore functioned as a repeating discovery process rather than a single event.[UK Parliament]publications.parliament.ukUK Parliament House of LordsUK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008…
Why most systems resisted while a few failed
One of the most frequently misunderstood aspects of the case is the relationship between the number of computers scanned and the number ultimately compromised.
Contemporary Justice Department allegations and media reporting indicate that McKinnon examined tens of thousands of systems but was accused of accessing fewer than one hundred government computers. That difference is significant because it illustrates that the overwhelming majority of scanned machines did not become successful intrusions. Automated scanning was a filtering mechanism designed to locate exceptions rather than evidence that an entire government network lacked security.[justice.gov]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 2002)…
Officials quoted during the investigation made this point explicitly. They noted that only around one hundred military systems appeared vulnerable out of the many thousands examined, arguing that the scan results showed many systems successfully resisted unauthorised access. Security researchers, however, observed that even a small fraction of vulnerable machines could present a serious organisational risk if those systems held administrative privileges or provided pathways into wider networks.[WIRED]wired.comBrit Fights Hacking Extradition | WIREDBrit Fights Hacking Extradition | WIRED…
Accounts of exactly why individual computers failed differ slightly across sources. Court documents refer to administrative accounts and associated passwords, while McKinnon later stated in interviews that he repeatedly found administrator accounts with blank passwords. Investigators also reported simple, easily guessed passwords on some systems. These explanations are not necessarily contradictory because different computers could have exhibited different configuration errors. The common factor was that the automated scan identified machines worth investigating more closely rather than proving every host was identically vulnerable.[parliament.uk]publications.parliament.ukUK Parliament House of LordsUK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008…
What the scanning scale does—and does not—prove
The scale of McKinnon’s scanning has sometimes been presented as evidence that United States government networks were broadly insecure. The available evidence supports a more nuanced conclusion.
The documented scanning activity demonstrates that automated reconnaissance can efficiently search enormous address spaces for isolated security weaknesses. Once automation is involved, examining tens of thousands of internet addresses becomes technically straightforward. What requires effort is finding the comparatively small subset where authentication, configuration or remote administration has been implemented poorly enough to permit further access.[UK Parliament]publications.parliament.ukUK Parliament House of LordsUK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008…
Equally important, the number of scanned systems should not be confused with the number of compromised systems. Public reporting and court records consistently distinguish between those figures. Prosecutors alleged scans of tens of thousands of government computers but unauthorised access to approximately ninety-seven systems. Those figures indicate a search process with a low success rate rather than widespread automatic compromise.[parliament.uk]publications.parliament.ukUK Parliament House of LordsUK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008…
The case also illustrates an enduring principle of network defence. Large organisations may successfully protect the vast majority of their infrastructure, yet a handful of poorly configured internet-facing machines can still create disproportionate risk if they provide administrative access or serve as stepping stones into additional systems. According to the indictment, once McKinnon gained access to one machine, he allegedly used it to locate and compromise further military and NASA computers, showing how reconnaissance and lateral movement could reinforce one another.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 2002)…
Why this mechanism became an enduring security lesson
Although the McKinnon case is often remembered because of his stated interest in UFO-related information, security professionals frequently cite it for a different reason: it demonstrated how ordinary automation could expose weak operational security across large organisations.
Nothing in the public record indicates that the initial discovery process depended on exotic malware or advanced exploitation. Instead, investigators described the use of readily available scanning software to identify internet-exposed Windows systems, followed by attempts to authenticate where administrative protections had been inadequately configured. The significance lay in combining large-scale automated reconnaissance with patience and persistence until vulnerable machines were found.[wired.com]wired.comBrit Fights Hacking Extradition | WIREDBrit Fights Hacking Extradition | WIRED…
For defenders, the episode reinforced the importance of reducing publicly exposed services, enforcing strong authentication, monitoring internet-facing systems continuously and assuming that automated scanning by external parties is constant rather than exceptional. The underlying mechanism remains relevant because modern attackers still use automated discovery tools to locate the small proportion of systems that have been misconfigured, even when the overwhelming majority of machines are properly secured.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 2002)…
Amazon book picks
Further Reading
Books and field guides related to How Mass Scanning Found the Weakest Machines. Use these as the next step if you want deeper reading beyond the article.
Nmap Network Scanning
The official guide to the Nmap Security Scanner, a free and open source utility used by millions of people, suits all levels of security...
Network Security Assessment
Covers offensive technologies by grouping and analyzing them at a higher level--from both an offensive and defensive standpoint--helping...
Hacking: The Art of Exploitation
Hacking is the art of creative problem solving, whether that means finding an unconventional solution to a difficult problem or exploitin...
The Practice of Network Security Monitoring
Network security is not simply about building impenetrable walls—determined attackers will eventually overcome traditional defenses. The...
eBay marketplace picks
Marketplace Samples
Live-tested eBay searches with available results related to this page.
Selected fromhacker t shirt oneBay.co.uk.
Endnotes
1.
Source: publications.parliament.uk
Title: UK Parliament House of Lords
Link:https://publications.parliament.uk/pa/ld200708/ldjudgmt/jd080730/mckinn-1.htm
Source snippet
UK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008...
Published: July 30, 2008
2.
Source: justice.gov
Link:https://www.justice.gov/archive/criminal/cybercrime/press-releases/2002/mckinnonIndict.htm
Source snippet
Department of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 2002)...
Published: November 12, 2002
3.
Source: wired.com
Title: Brit Fights Hacking Extradition | WIRED
Link:https://www.wired.com/2002/11/brit-fights-hacking-extradition/
Source snippet
Brit Fights Hacking Extradition | WIRED...
4.
Source: justice.gov
Link:https://www.justice.gov/archive/criminal/cybercrime/press-releases/2002/mckinnonIndict2.htm
Source snippet
Department of JusticeBritish National Charged with Hacking Into N.J. Naval Weapons Station Computers, Disabling Network After Sept. 11 (N...
5.
Source: wired.com
Title: accused pentagon hacker in court
Link:https://www.wired.com/2005/06/accused-pentagon-hacker-in-court/
6.
Source: wired.com
Title: brit accused of hacking pentagon
Link:https://www.wired.com/2002/11/brit-accused-of-hacking-pentagon/
7.
Source: theguardian.com
Title: The Guardian Game over | Gary Mc Kinnon | The Guardian
Link:https://www.theguardian.com/theguardian/2005/jul/09/weekend7.weekend2
8.
Source: theguardian.com
Link:https://www.theguardian.com/technology/2008/jul/30/gary.mckinnon
Source snippet
Gary McKinnon – 'world's most dangerous hacker' – to be extradited | Hacking | The GuardianJuly 30, 2008 — Image: 'Super hacker' Gary McK...
Published: July 30, 2008
9.
Source: theguardian.com
Link:https://www.theguardian.com/technology/2008/jun/16/hacking.internationalcrime
Source snippet
June 16, 2008 — This article is more than 18 years old BRITISH HACKER SHOULD NOT BE EXTRADITED TO US, LORDS TOLD This article is more tha...
Published: June 16, 2008
10.
Source: theguardian.com
Title: I spent
Link:https://www.theguardian.com/theobserver/2007/apr/22/features.magazine7
Source snippet
Gary McKinnon | Life and style | The GuardianApril 21, 2007 — This article is more than 19 years old GARY MCKINNON This article is more t...
Published: April 21, 2007
11.
Source: theguardian.com
Title: British hacker faces extradition to US | US news | The Guardian
Link:https://www.theguardian.com/technology/2006/may/10/news.usnews
12.
Source: theguardian.com
Title: Hacker ‘left note on US army computer’ | Hacking | The Guardian
Link:https://www.theguardian.com/technology/2005/jul/27/hacking.internetcrime
Additional References
13.
Source: youtube.com
Title: The Man Who Hacked the U.S. Government
Link:https://www.youtube.com/watch?v=ND0zQX1rGdg
Source snippet
Hacking for UFOs and fighting for his life. Who is Gary McKinnon?...
14.
Source: youtube.com
Title: Hacking for UFOs and fighting for his life. Who is Gary Mc Kinnon?
Link:https://www.youtube.com/watch?v=OImdnvQx7sQ
Source snippet
UK hacker's extradition to US blocked...
15.
Source: youtube.com
Title: Gary Mc Kinnon wins extradition battle
Link:https://www.youtube.com/watch?v=y4lecD44F5E
Source snippet
The Man Who Hacked the U.S. Government...
16.
Source: youtube.com
Title: UK hacker’s extradition to US blocked
Link:https://www.youtube.com/watch?v=v4Js8DF80HY
Source snippet
Ancient Aliens: Hacking NASA Secrets...
17.
Source: youtube.com
Title: Ancient Aliens: Hacking NASA Secrets
Link:https://www.youtube.com/watch?v=20rWFDfh68Y
Source snippet
Gary McKinnon wins extradition battle...