Within Access Methods
Remotelyanywhere Per
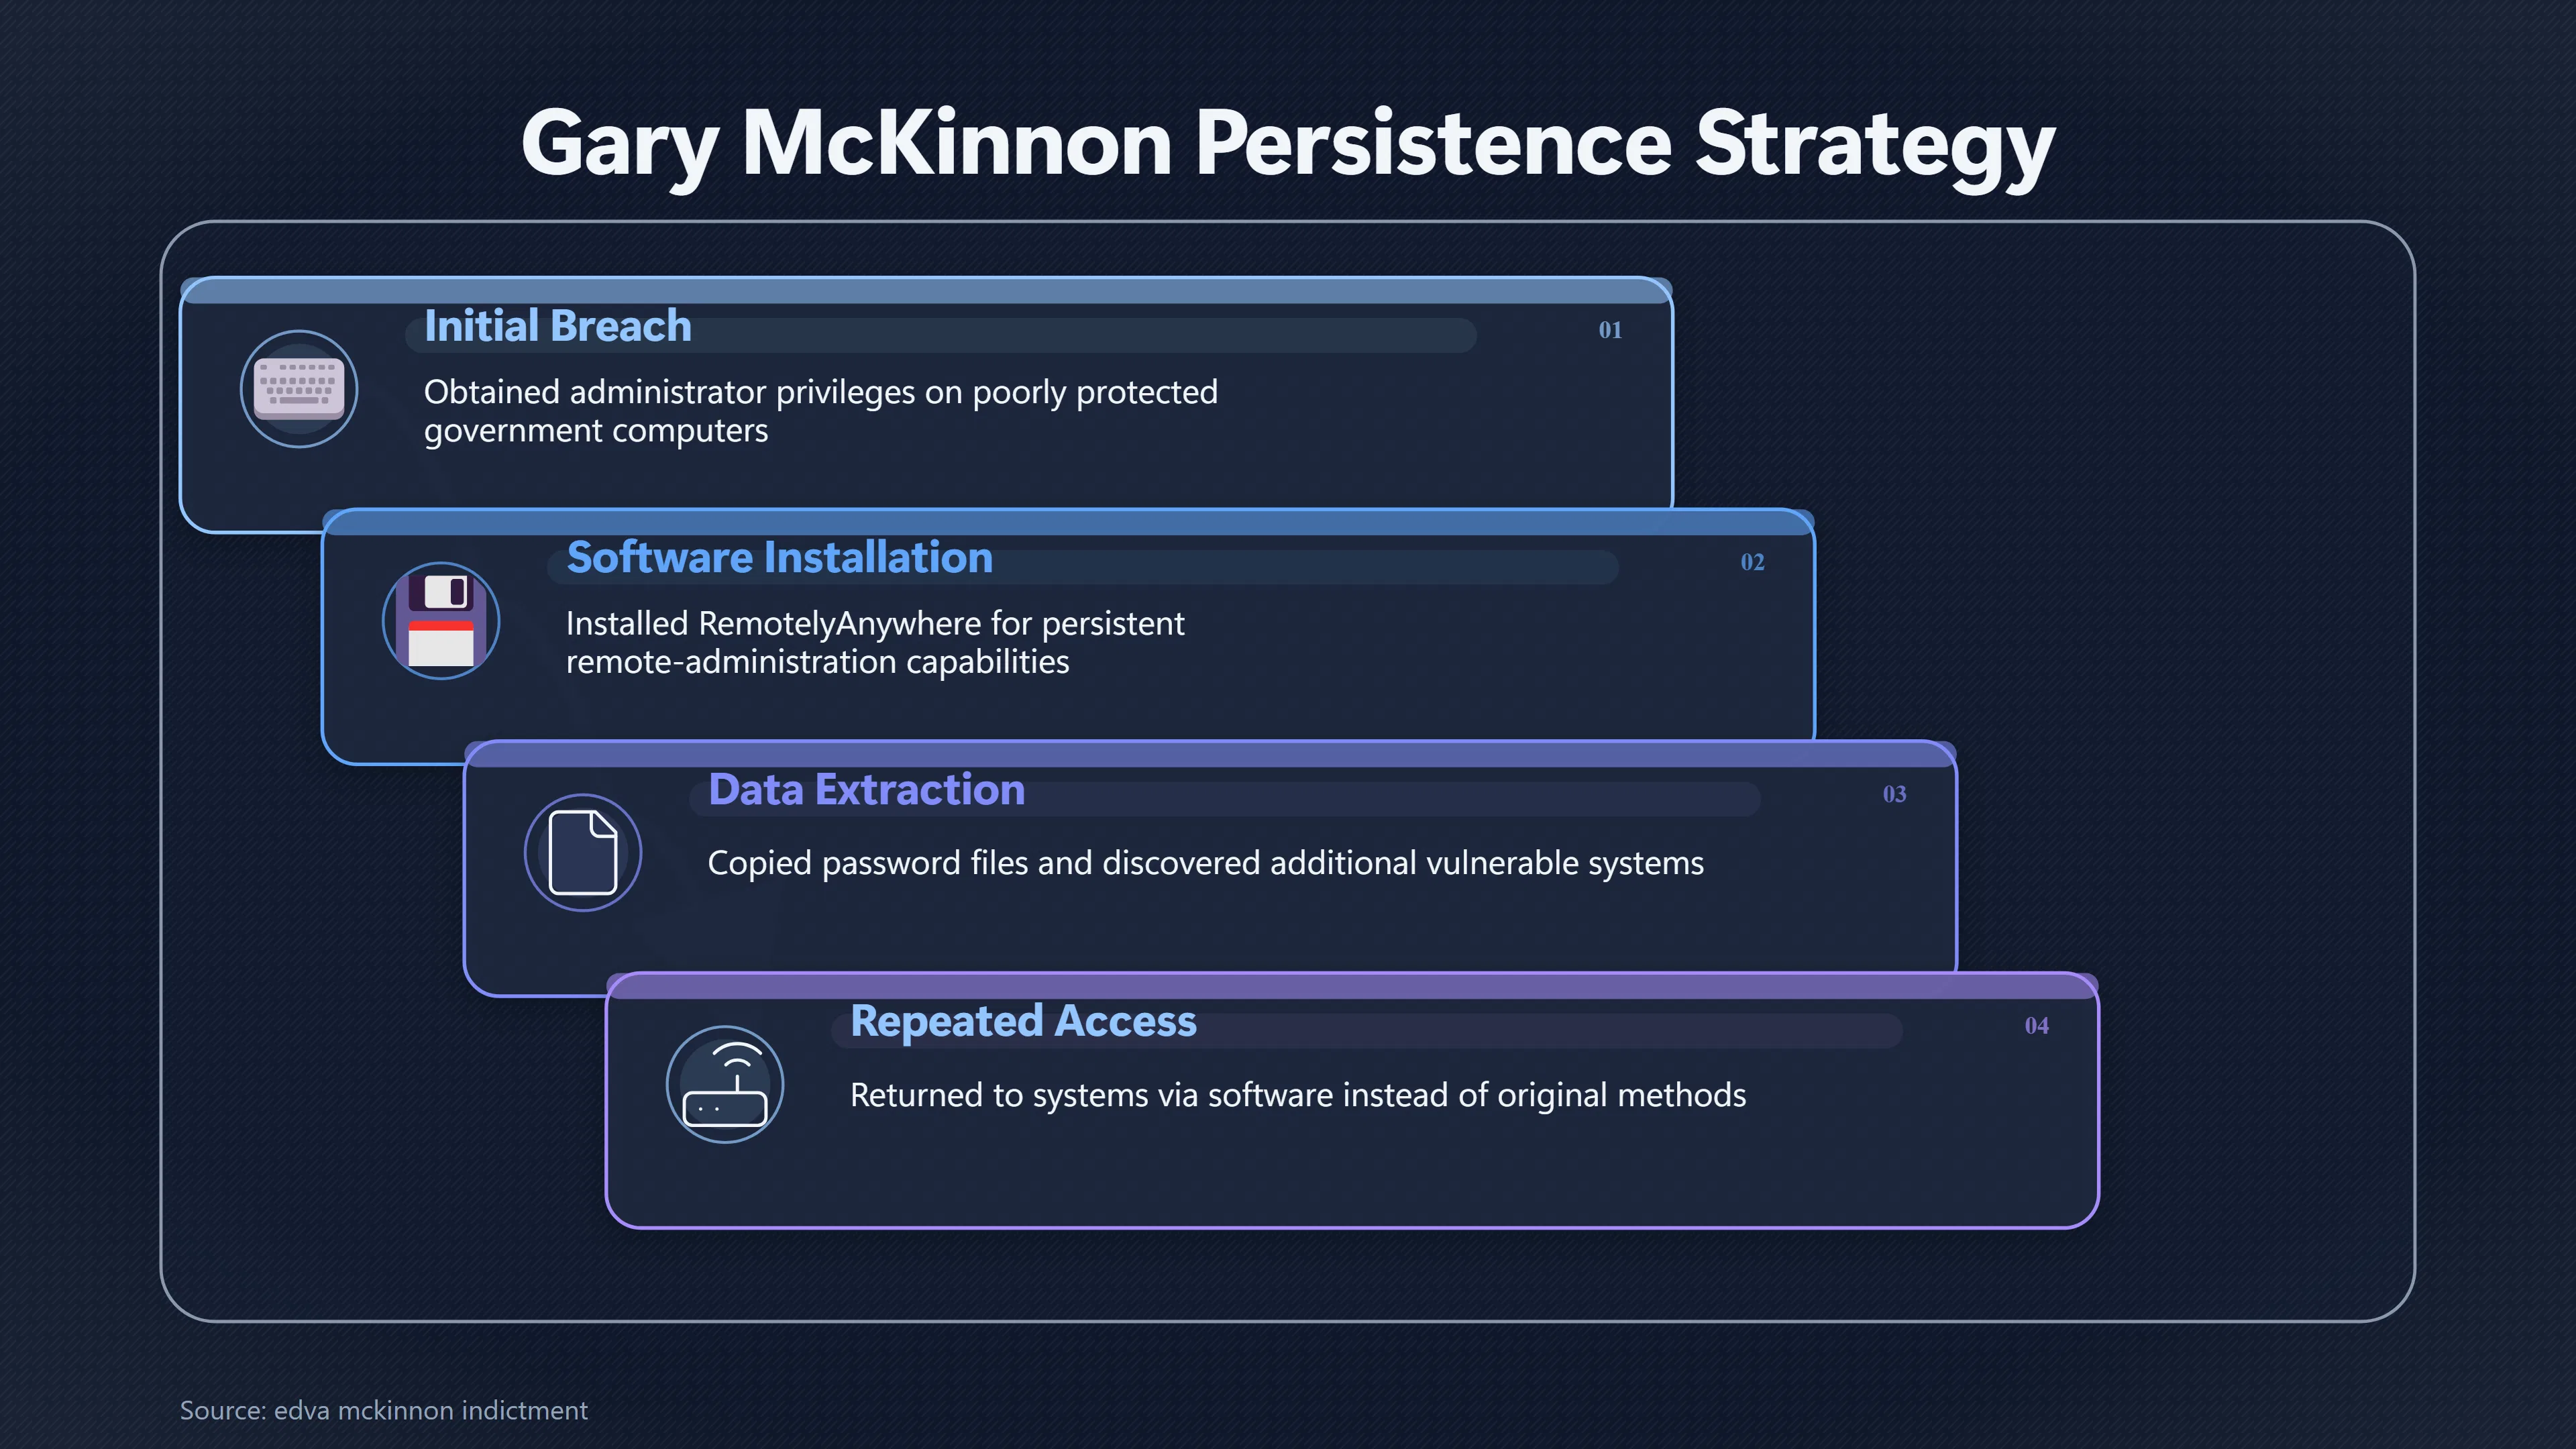
After Gary McKinnon had obtained administrator privileges on poorly protected US government computers, his next objective was not to repeat the same login process every time he wanted to reconnect.
Page outline Jump by section
Introduction
The significance of RemotelyAnywhere lies in how it transformed a one-time compromise into persistent access. Instead of repeatedly searching for vulnerable machines or reusing the original authentication method, McKinnon could reconnect directly through software already running on the target computer. The choice of a legitimate administration product also illustrates how ordinary IT tools can become security liabilities when installed without authorisation.
The Legitimate Tool That Became a Back Door
RemotelyAnywhere was not malicious software. Developed as a commercial remote-management product, it enabled authorised administrators to control Windows computers from another internet-connected machine through a web browser. Once installed, it provided capabilities comparable to sitting in front of the physical computer, including desktop access, file management and system administration.[Department of Justice]justice.govedva mckinnon indictmentDepartment of JusticeIN THE UNITED STATES DISTRICT COURT FOR THEMarch 26, 2026…
According to the federal indictment, once installed on a host computer the software allowed a user to:
- remotely control the computer over the internet;
- transfer, copy and delete files;
- perform nearly every administrative function available to someone physically using the machine;
- return to the same system repeatedly without relying on the original method of entry.[Department of Justice]justice.govedva mckinnon indictmentDepartment of JusticeIN THE UNITED STATES DISTRICT COURT FOR THEMarch 26, 2026…
Those features made the software valuable for legitimate IT departments but equally valuable to anyone who had already obtained administrator rights without authorisation.
Why Commercial Software Could Attract Less Suspicion
The allegations against McKinnon consistently distinguish between gaining access and maintaining it. After administrative privileges had been obtained, investigators alleged that he installed commercially available remote-administration software rather than relying solely on hacking utilities.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20…
This distinction mattered because commercial administration tools differed from many traditional “backdoor” programs of the period:
- they were widely used by legitimate organisations;
- they offered stable, feature-rich remote administration;
- they often resembled ordinary system-management software rather than malware;
- security products of the early 2000s were generally less likely to treat authorised administration utilities as inherently suspicious.[WIRED]wired.comdot mil hackers download mistakeDot-Mil Hacker's Download Mistake | WIREDNovember 15, 2002…
British court records summarised the allegation by stating that the software enabled McKinnon to access and alter data “at any time” while masquerading as part of the Windows operating system, making the unauthorised access less immediately obvious to administrators who were not actively looking for it.[UK Parliament]publications.parliament.ukUK Parliament Microsoft WordUK ParliamentMicrosoft Word - McKinnon Appellant v Government of the United States of America Respondents and another.doc…
Importantly, this did not make RemotelyAnywhere itself malicious. The software’s intended purpose was lawful remote administration. The alleged abuse arose from installing it without permission on computers that had already been compromised.
How Persistent Access Changed the Investigation
US prosecutors alleged that RemotelyAnywhere became a central component of maintaining continued access to several networks.
One indictment involving Naval Weapons Station Earle alleged that McKinnon installed RemotelyAnywhere on a port services computer and other connected systems, then used the previously installed software on multiple later occasions to reconnect over the internet. Prosecutors further alleged that, after obtaining password information, he later re-entered the network through the same installed software rather than recreating the original compromise.[Department of Justice]justice.govDepartment of JusticeBritish National Charged with Hacking Into N.J. Naval Weapons Station Computers, Disabling Network After Sept. 11 (N…
The broader Virginia indictment similarly alleges that after obtaining administrator privileges on military, NASA and other systems, McKinnon installed RemotelyAnywhere alongside other tools, copied password files and used compromised systems to discover additional vulnerable computers. In that account, the remote-administration software became part of a wider pattern of persistence rather than an isolated action.[Department of Justice]justice.govedva mckinnon indictmentDepartment of JusticeIN THE UNITED STATES DISTRICT COURT FOR THEMarch 26, 2026…
Within the prosecution’s narrative, this transformed individual compromised computers into convenient return points, reducing the need to repeat the original authentication process every time access was required.
The Download Records That Helped Trace McKinnon
Ironically, the use of legitimate commercial software also generated evidence that investigators could later exploit.
Contemporary reporting by WIRED described how investigators examined download logs maintained by the software distributor. According to the report, McKinnon downloaded a trial version of RemotelyAnywhere from the vendor’s server using an internet connection associated with his UK internet service provider. The download process also allegedly included an email address supplied to obtain an evaluation code. Those records reportedly became significant investigative leads linking the software installation to a specific individual in London.[WIRED]wired.comdot mil hackers download mistakeDot-Mil Hacker's Download Mistake | WIREDNovember 15, 2002…
Unlike underground hacking tools distributed anonymously, commercial software frequently involved ordinary business processes such as:
- web server download logs;
- evaluation licence requests;
- customer registration information;
- recorded IP addresses associated with downloads.
In this case, investigators believed those ordinary commercial records helped connect the installations found on compromised government systems to McKinnon’s internet activity. Although they formed only part of a much larger international investigation, they illustrate how using legitimate software can leave unexpectedly useful forensic evidence.[WIRED]wired.comdot mil hackers download mistakeDot-Mil Hacker's Download Mistake | WIREDNovember 15, 2002…

What the Case Demonstrated About Remote Administration
The McKinnon case has often been remembered because of its connection with military systems and his stated interest in UFO-related material. From a computer security perspective, however, one of its more enduring lessons concerns persistence rather than initial intrusion.
The allegations show how legitimate administration software can become an effective unauthorised access mechanism once administrator privileges have already been obtained. The software itself was not the vulnerability; weak authentication and inadequate system security created the opportunity. After that point, a commercially supported remote-management product allegedly provided reliable, repeatable access while blending into the kinds of tools that administrators themselves commonly used.[justice.gov]justice.govedva mckinnon indictmentDepartment of JusticeIN THE UNITED STATES DISTRICT COURT FOR THEMarch 26, 2026…
Amazon book picks
Further Reading
Books and field guides related to Remotelyanywhere Per. Use these as the next step if you want deeper reading beyond the article.
Ghost in the Wires
In this "intriguing, insightful and extremely educational" novel, the world's most famous hacker teaches you easy cloaking and counter-me...
Hacking: The Art of Exploitation
Hacking is the art of creative problem solving, whether that means finding an unconventional solution to a difficult problem or exploitin...
Network Security Assessment
Covers offensive technologies by grouping and analyzing them at a higher level--from both an offensive and defensive standpoint--helping...
Practical Malware Analysis
Malware analysis is big business, and attacks can cost a company dearly. When malware breaches your defenses, you need to act quickly to...
eBay marketplace picks
Marketplace Samples
Live-tested eBay searches with available results related to this page.
Selected fromhacker t shirt oneBay.co.uk.
Endnotes
1.
Source: justice.gov
Title: edva mckinnon indictment
Link:https://www.justice.gov/archive/usao/nj/Press/files/pdffiles/Older/edva_mckinnon_indictment.pdf
Source snippet
Department of JusticeIN THE UNITED STATES DISTRICT COURT FOR THEMarch 26, 2026...
Published: March 26, 2026
2.
Source: publications.parliament.uk
Title: UK Parliament Microsoft Word
Link:https://publications.parliament.uk/pa/ld200708/ldjudgmt/jd080730/mckinn.pdf
Source snippet
UK ParliamentMicrosoft Word - McKinnon _Appellant_ v Government of the United States of America _Respondents_ and another.doc...
3.
Source: justice.gov
Link:https://www.justice.gov/archive/criminal/cybercrime/press-releases/2002/mckinnonIndict.htm
Source snippet
Department of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20...
4.
Source: wired.com
Title: dot mil hackers download mistake
Link:https://www.wired.com/2002/11/dot-mil-hackers-download-mistake/
Source snippet
Dot-Mil Hacker's Download Mistake | WIREDNovember 15, 2002...
Published: November 15, 2002
5.
Source: justice.gov
Link:https://www.justice.gov/archive/criminal/cybercrime/press-releases/2002/mckinnonIndict2.htm
Source snippet
Department of JusticeBritish National Charged with Hacking Into N.J. Naval Weapons Station Computers, Disabling Network After Sept. 11 (N...
6.
Source: justice.gov
Link:https://www.justice.gov/opa/pr/justice-department-announces-coordinated-nationwide-actions-combat-north-korean-remote
Source snippet
ogy Workers’ Illicit Revenue Generation Schemes | United States Department of JusticeJune 30, 2025 — Press Release JUSTICE DEPARTMENT ANN...
Published: June 30, 2025
7.
Source: youtube.com
Title: The Untold Story of Gary Mc Kinnon: Biggest Military Hack Ever!
Link:https://www.youtube.com/watch?v=-_tzaIKGnYw
Source snippet
UFO - Hacker Gary Mckinnon Interview 5-5-2006 BBC...
8.
Source: youtube.com
Link:https://www.youtube.com/watch?v=B00Fv9VMDq0
Source snippet
Gary McKinnon hacker Hacking for UFOs and fighting for his life. Who is Gary McKinnon? | NordVPN NordVPN...
9.
Source: GOV.UK
Title: About this guid
Link:https://www.gov.uk/government/publications/immigration-enforcement-digital-device-extraction-policy/immigration-enforcement-criminal-and-financial-investigations-digital-devices-seizure-and-retention-and-data-extraction-policy-accessible
Source snippet
Enforcement criminal and financial investigations: digital devices - seizure and retention, and data extraction policy (accessible) - GOV...
10.
Source: GOV.UK
Title: www.gov.uk Recovery and Acquisition of Video Evidence v3.0
Link:https://www.gov.uk/government/publications/recovery-and-acquisition-of-video-evidence/recovery-and-aquisition-of-video-evidence-v30
Source snippet
and Acquisition of Video Evidence v3.0 - GOV.UKJune 15, 2022 — 3 RETRIEVAL AND PRESERVATION OF VIDEO EVIDENCE 3.1 INTRODUCTION This proce...
Published: June 15, 2022
Additional References
11.
Source: csri.info
Title: CSR I | “Gary Mc Kinnon was unlucky
Link:https://www.csri.info/gary-mckinnon-was-unlucky-hes-not-even-a-very-good-hacker/
Source snippet
He’s not even a very good hacker”October 22, 2012 — The junior hacker “He was asking for passwords to US systems and ways to access them...
Published: October 22, 2012
12.
Source: youtube.com
Title: Hacking for UFOs and fighting for his life. Who is Gary Mc Kinnon?
Link:https://www.youtube.com/watch?v=OImdnvQx7sQ
Source snippet
The Untold Story of Gary McKinnon: Biggest Military Hack Ever...
13.
Source: youtube.com
Title: UFO Hacker Shares New Secrets | Gary Mc Kinnon
Link:https://www.youtube.com/watch?v=_SOTGFj7BwI
Source snippet
Hacking for UFOs and fighting for his life. Who is Gary McKinnon?...
14.
Source: youtube.com
Title: UFO Hacker Gary Mc Kinnon talks about NASA Hack
Link:https://www.youtube.com/watch?v=ZKfKIUXhqSM
Source snippet
UFO Hacker Shares New Secrets | Gary McKinnon...
15.
Source: ufohackers.org
Link:https://www.ufohackers.org/hackers/gary-mckinnon/mckinnon-overview
16.
Source: linuxsecurity.com
Title: Gary Mc Kinnon Indicted For Hacking U.S. Military Systems
Link:https://linuxsecurity.com/news/hackscracks/dot-mil-hackers-download-mistake
17.
Source: govexec.com
Title: British man indicted for hacking into military networks
Link:https://www.govexec.com/technology/2002/11/british-man-indicted-for-hacking-into-military-networks/12896/
18.
Source: cio.com
Title: it strategy u k approves extradition order for hacker
Link:https://www.cio.com/article/258826/it-strategy-u-k-approves-extradition-order-for-hacker.html
19.
Source: infoworld.com
Title: U K grants extradition order for hacker | Info World
Link:https://www.infoworld.com/article/2184117/uk-grants-extradition-order-for-hacker.html
20.
Source: csoonline.com
Title: U.K. Hacker Fights U.S. Extradition | CSO Online
Link:https://www.csoonline.com/article/520766/data-protection-u-k-hacker-fights-u-s-extradition.html