Within Claim Checklist
What Makes a Leaked UFO File Trustworthy?
Original files, forensic copies, hashes and handling records determine whether alleged UFO material can be examined without guessing about alteration.
On this page
- How digital evidence should be acquired
- Why hashes and handling records matter
- What independent examiners need to reproduce
Page outline Jump by section
Introduction
When evaluating a UFO hacking claim, the credibility of any alleged file depends less on its apparent content than on whether its history can be demonstrated. A dramatic document, spreadsheet or image is not persuasive simply because someone says it came from a government system. Investigators need a documented chain of custody: a record showing where the material originated, how it was acquired, who handled it, whether it was copied correctly and whether it remained unchanged throughout examination. Digital forensics standards consistently treat these steps as essential because they allow independent experts to verify findings rather than relying on personal testimony.[NIST Computer Security Resource Center]csrc.nist.govComputer Security Resource Centerdigital forensicsNIST Computer Security Resource Centerdigital forensics - Glossary | CSRC…
Within the context of UFO-related hacking claims such as those made by Gary McKinnon, this distinction is particularly important. Public discussion often centres on the alleged contents of files, but the first question should be whether the files themselves exist in a form that can be independently authenticated. Without an unbroken evidential record, debates about extraordinary interpretations become largely speculative.
How digital evidence should be acquired
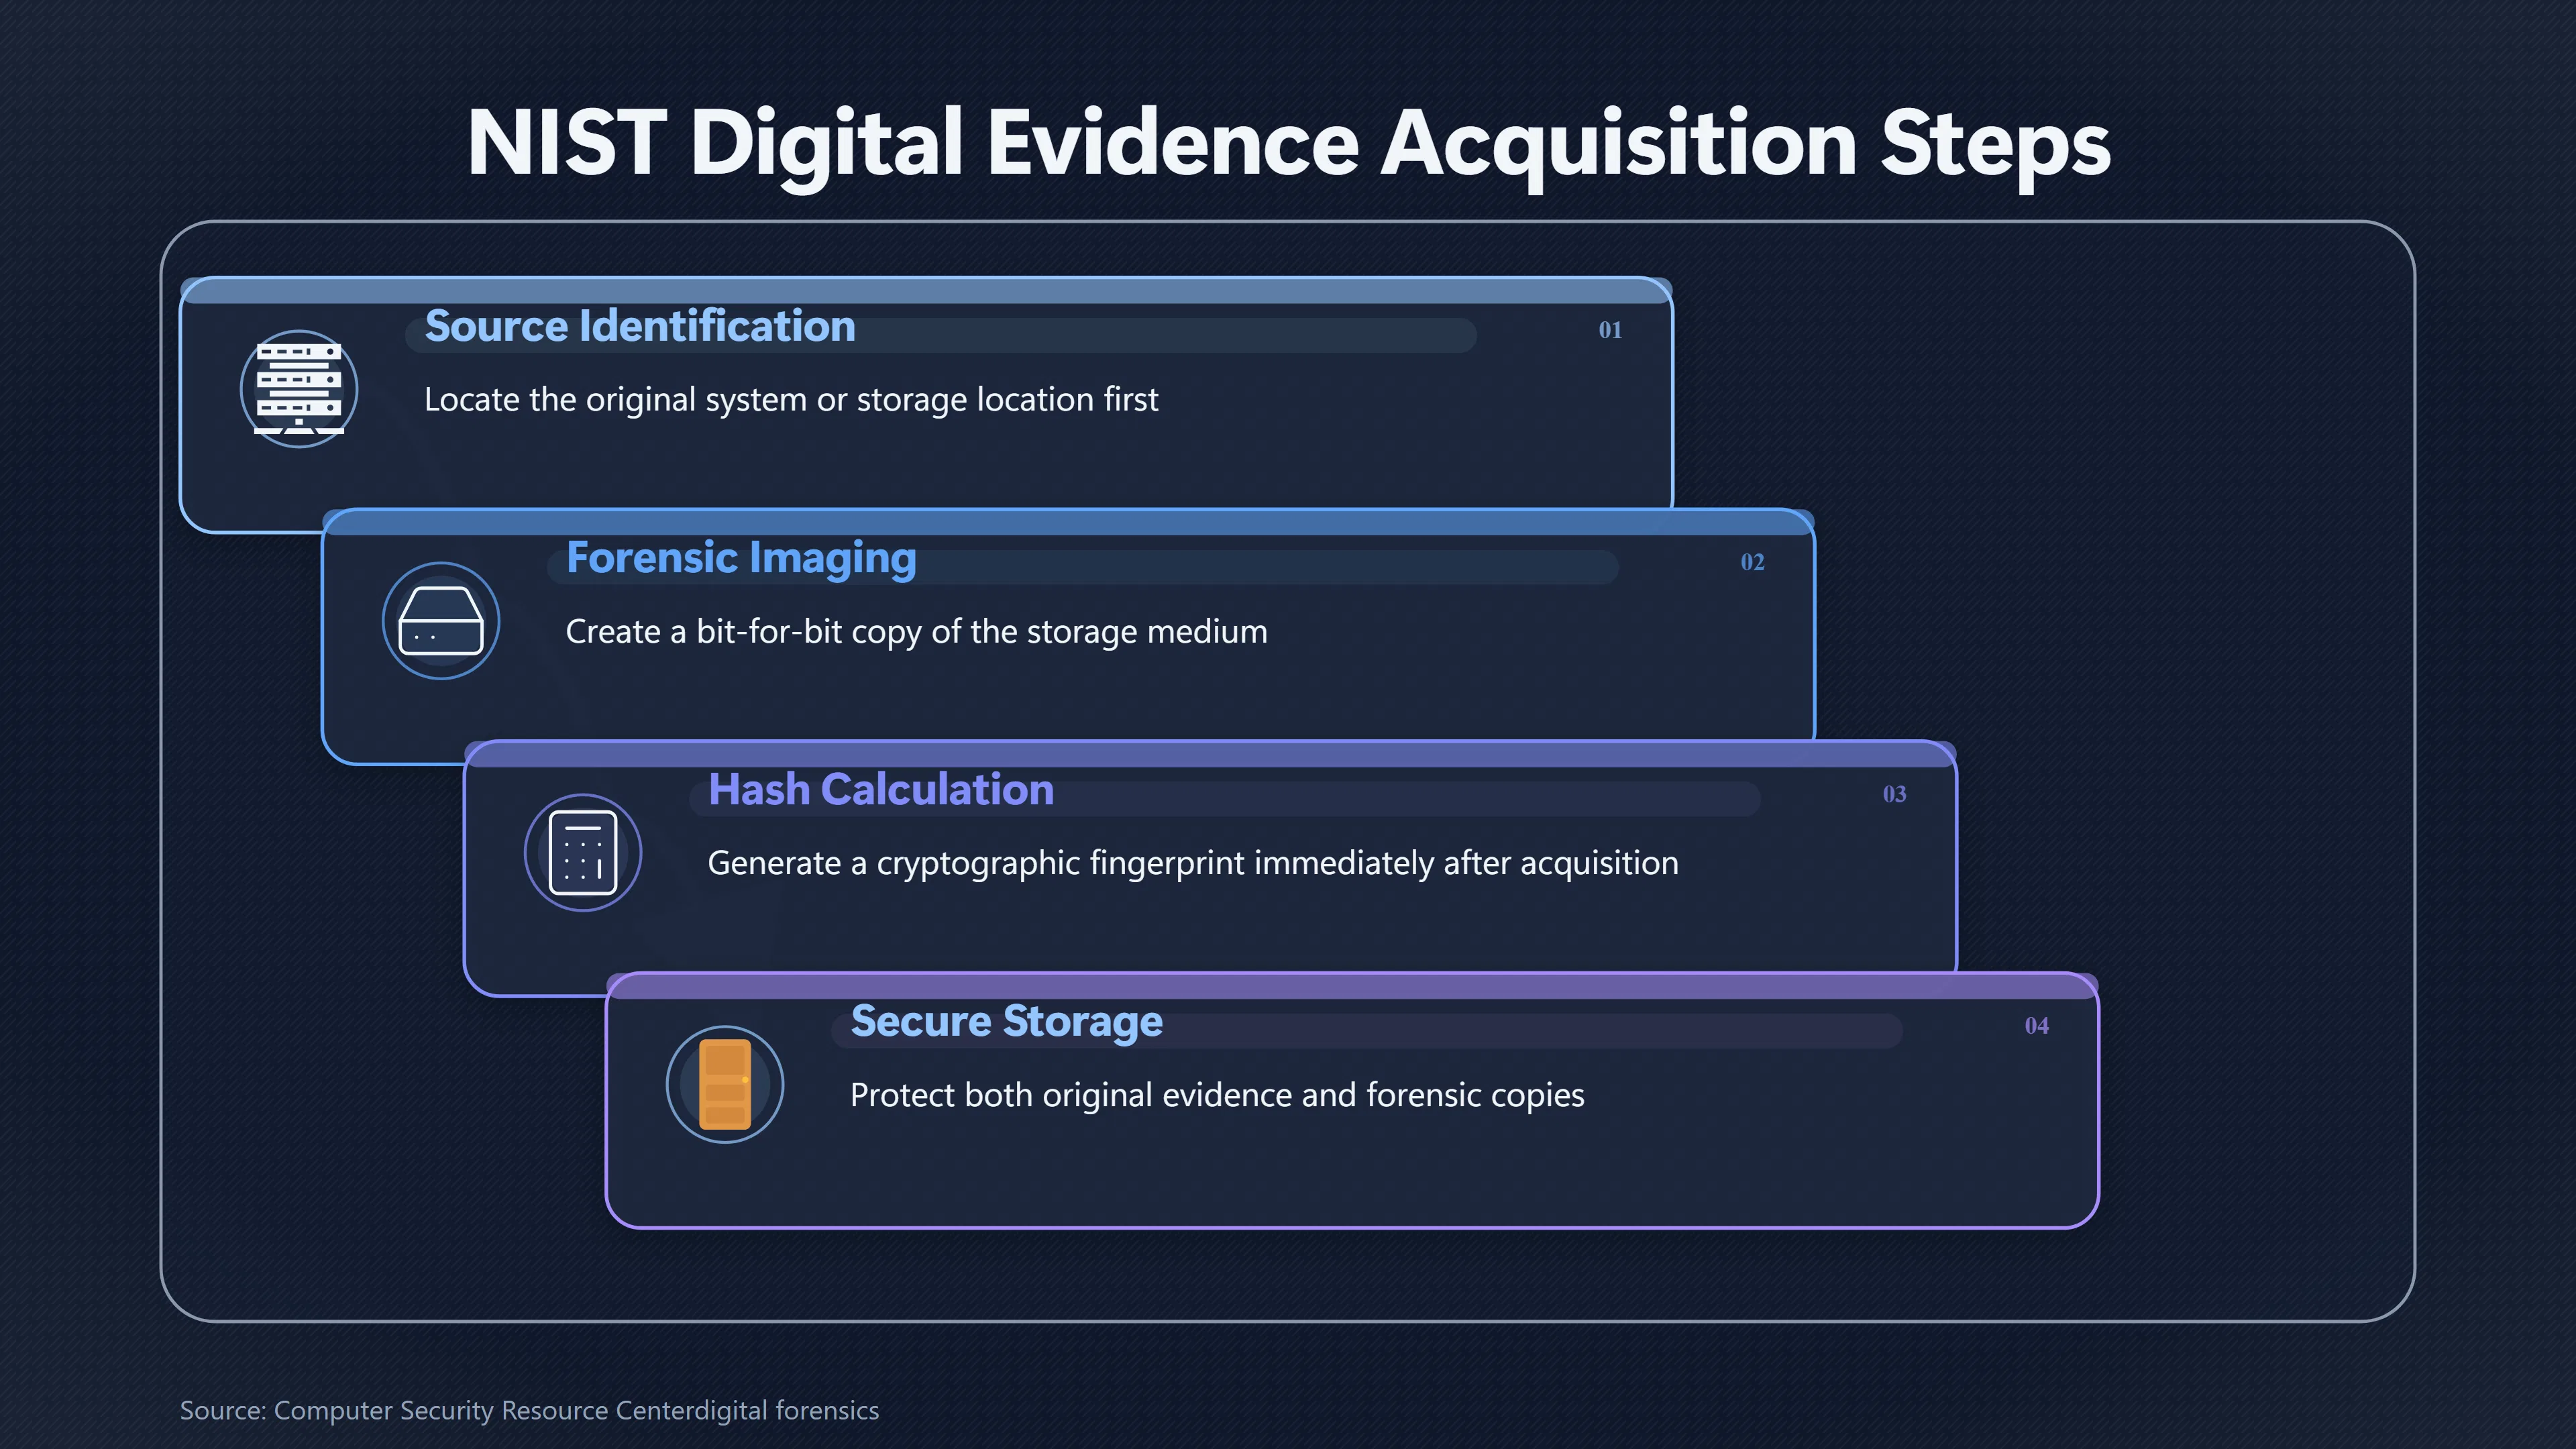
The strongest digital evidence begins with preserving the original source rather than working directly on it. Standard forensic practice is to create a bit-for-bit forensic image of the storage medium or server data whenever possible, leaving the original untouched. Analysis is then performed on the forensic copy, ensuring that investigators cannot accidentally alter the evidence.[NIST Computer Security Resource Center]csrc.nist.govNIST Computer Security Resource CenterSP 800-86, Guide to Integrating Forensic Techniques into Incident Response | CSRC…
For an alleged UFO-related document, a credible acquisition process would ideally include:
- identification of the original system or storage location;
- the date and time of acquisition;
- the person who performed the acquisition;
- the software and hardware tools used;
- documentation showing that the acquisition process itself did not modify the source;
- secure storage of both the original evidence and its forensic image.
If evidence originates from a compromised computer rather than an official forensic seizure, the available documentation may be more limited. Even then, preserving original copies before any editing, renaming or conversion greatly improves later analysis.
Why hashes and handling records matter
A digital file can be copied perfectly thousands of times, but only if investigators can demonstrate that every copy matches the original. This is why cryptographic hash values are fundamental to digital forensics.
A hash function produces a fixed-length digital fingerprint from a file. Algorithms such as SHA-256 generate values that change completely if even a single bit of the file changes. Investigators therefore calculate a hash immediately after acquisition and recalculate it whenever the evidence is transferred or analysed.
In practical terms:
- matching hashes strongly indicate that two files are identical;
- differing hashes show that some change has occurred;
- hashes cannot explain why a change occurred, only that one did.
Digital forensics guidance treats mathematical validation through hashes as one of the mechanisms that makes examination repeatable and scientifically defensible.[NIST Computer Security Resource Center]csrc.nist.govComputer Security Resource Centerdigital forensicsNIST Computer Security Resource Centerdigital forensics - Glossary | CSRC…
Handling records are equally important. Every transfer of evidence should record:
Record elementPurposeDate and timeEstablishes chronologyPerson releasing evidenceIdentifies responsibilityPerson receiving evidenceMaintains accountabilityReason for transferExplains accessHash verificationConfirms integrity after transfer
Without these records, investigators cannot distinguish between deliberate tampering, accidental modification and simple administrative uncertainty.
What independent examiners need to reproduce
Extraordinary claims become more credible when independent specialists can repeat the examination and obtain the same results.
That generally requires access not merely to screenshots or summaries but to enough technical information to reproduce the investigation, including:
- the original file or forensic image where legally possible;
- cryptographic hash values;
- metadata showing creation, modification and access times;
- directory structure and file paths;
- acquisition notes;
- versions of forensic software used during examination.
Repeatability is a defining principle of digital forensics. Scientific confidence increases when another examiner, using the same evidence and validated methods, reaches the same conclusions.[nist.gov]csrc.nist.govComputer Security Resource Centerdigital forensicsNIST Computer Security Resource Centerdigital forensics - Glossary | CSRC…
By contrast, a verbal description of a file cannot be independently reproduced. Neither can a cropped image with no metadata or a transcript lacking the original document.
What weakens a claimed chain of custody
Several common situations reduce confidence in alleged leaked UFO material even if there is no evidence of deliberate fabrication.
Only screenshots survive. Screenshots preserve visual appearance but usually discard important metadata, internal structure and file history.
Files have been repeatedly converted. Images saved through multiple formats or documents copied between applications may lose metadata or acquire new timestamps unrelated to the original creation.
Unknown editing history. If nobody can identify who possessed the file over time, changes cannot be confidently attributed or excluded.
Missing originals. Copies without access to an original reference cannot be conclusively authenticated.
Late disclosure. Files emerging many years after their alleged discovery without contemporaneous records face greater scrutiny because opportunities for accidental or intentional alteration increase over time.
None of these issues automatically prove deception, but each reduces the evidential weight that investigators can reasonably assign.

Applying these principles to UFO hacking claims
These forensic standards explain why many well-known UFO hacking stories remain difficult to evaluate decades later.
In Gary McKinnon’s case, the unauthorised computer access itself is documented through legal proceedings and government records. However, the specific UFO-related files he described have not entered the public domain with original forensic images, preserved metadata, documented acquisition procedures or independently verified cryptographic hashes. As a result, outside investigators cannot perform the kind of repeatable examination expected in digital forensic practice.[NIST Computer Security Resource Center]csrc.nist.govNIST Computer Security Resource CenterSP 800-86, Guide to Integrating Forensic Techniques into Incident Response | CSRC…
This distinction matters because several different explanations remain compatible with the available evidence. A remembered filename, spreadsheet heading or image may accurately reflect something that existed on a system, may represent an ordinary document interpreted unusually, or may be imperfectly recalled years later. Without preserved digital evidence accompanied by a demonstrable chain of custody, forensic methods cannot reliably distinguish among those possibilities.
What would make a leaked UFO file substantially more trustworthy?
A genuinely persuasive leak would not rely primarily on extraordinary content. Instead, it would arrive with verifiable provenance that allows independent examination.
The strongest package would include:
- the original digital file rather than only screenshots;
- cryptographic hash values generated immediately after acquisition;
- documented custody from acquisition onward;
- preserved metadata;
- forensic copies instead of edited working versions;
- sufficient technical information for independent experts to reproduce the examination;
- consistency between the file’s metadata, system logs and the claimed circumstances of discovery.
These measures cannot prove that an extraordinary claim about UFOs is true. They do, however, establish that investigators are examining authentic, unchanged digital evidence rather than an undocumented copy whose history cannot be reconstructed. That distinction is fundamental to evaluating any alleged UFO hacking claim.
Amazon book picks
Further Reading
Books and field guides related to What Makes a Leaked UFO File Trustworthy?. Use these as the next step if you want deeper reading beyond the article.
Handbook of Digital Forensics and Investigation
Handbook of Digital Forensics and Investigation builds on the success of the Handbook of Computer Crime Investigation, bringing together...
Digital Evidence and Computer Crime
Digital Evidence and Computer Crime, Second Edition, is a hands-on resource that aims to educate students and professionals in the law en...
File System Forensic Analysis
The Definitive Guide to File System Analysis: Key Concepts and Hands-on Techniques Most digital evidence is stored within the computer's...
Practical Forensic Imaging
Forensic image acquisition is an important part of postmortem incident response and evidence collection. Digital forensic investigators a...
eBay marketplace picks
Marketplace Samples
Live-tested eBay searches with available results related to this page.
Selected fromUFO memorabilia oneBay.co.uk.
Endnotes
1.
Source: csrc.nist.gov
Title: Computer Security Resource Centerdigital forensics
Link:https://csrc.nist.gov/glossary/term/digital_forensics
Source snippet
NIST Computer Security Resource Centerdigital forensics - Glossary | CSRC...
2.
Source: csrc.nist.gov
Link:https://csrc.nist.gov/pubs/sp/800/86/final
Source snippet
NIST Computer Security Resource CenterSP 800-86, Guide to Integrating Forensic Techniques into Incident Response | CSRC...
3.
Source: nist.gov
Title: Digital evidence | NIST
Link:https://www.nist.gov/digital-evidence
Source snippet
Digital evidence | NIST...
4.
Source: nist.gov
Title: Digital Investigation Techniques: A NIST Scientific Foundation Review | NIST
Link:https://www.nist.gov/publications/digital-investigation-techniques-nist-scientific-foundation-review
Source snippet
Digital Investigation Techniques: A NIST Scientific Foundation Review | NIST...
5.
Source: nist.gov
Link:https://www.nist.gov/news-events/news/2018/01/framework-harmonizing-forensic-science-practices-and-digitalmultimedia
Source snippet
A Framework for Harmonizing Forensic Science Practices and Digital/Multimedia Evidence | NIST...
6.
Source: toolcatalog.nist.gov
Title: This enables practitioners to find too
Link:https://toolcatalog.nist.gov/
Source snippet
Forensics Tools & Techniques Catalog - HomeJune 24, 2026 — COMPUTER FORENSICS TOOLS & TECHNIQUES CATALOG The primary goal of the Tool Cat...
Published: June 24, 2026
7.
Source: nist.gov
Title: framework harmonizing forensic
Link:https://www.nist.gov/adlp/spo/organization-scientific-area-committees-forensic-science/framework-harmonizing-forensic
8.
Source: nist.gov
Title: guide integrating forensic techniques incident response
Link:https://www.nist.gov/publications/guide-integrating-forensic-techniques-incident-response
9.
Source: nist.gov
Title: guide integrating forensic techniques incident response 0
Link:https://www.nist.gov/publications/guide-integrating-forensic-techniques-incident-response-0
10.
Source: csrc.nist.gov
Title: govchain of custody
Link:https://csrc.nist.gov/glossary/term/chain_of_custody
11.
Source: csrc.nist.rip
Title: ripdigital forensics
Link:https://csrc.nist.rip/glossary/term/digital_forensics
12.
Source: GOV.UK
Title: www.gov.uk Latest on Gary [Mc Kinnon case]({{ ‘mc-kinnon-case/’ | relative_url }})
Link:https://www.gov.uk/government/news/latest-on-gary-mckinnon-case
Additional References
13.
Source: legalclarity.org
Link:https://legalclarity.org/digital-evidence-chain-of-custody-requirements-and-standards/
Source snippet
Digital Evidence Chain of Custody: Requirements and Standards - LegalClarityMay 19, 2026 — DOCUMENTATION REQUIREMENTS Thorough documentat...
Published: May 19, 2026
14.
Source: youtube.com
Title: Understanding the Need of Chain of Custody in Digital Forensics
Link:https://www.youtube.com/watch?v=z_x7gCtntIc
Source snippet
What is chain of custody and why is it important for digital evidence? explains the legal and technical standards required to maintain a...
15.
Source: decryptiondigest.com
Title: forensic disk imaging chain of custody
Link:https://www.decryptiondigest.com/blog/forensic-disk-imaging-chain-of-custody
Source snippet
Forensic Disk Imaging and Chain of Custody Guide | (2026)May 22, 2026 — May 22, 2026 Updated June 18, 2026 12 min read FORENSIC DISK IMAG...
Published: May 22, 2026
16.
Source: legalclarity.org
Title: Forensic Disk Imaging: Bit-for-Bit Copies and Evidence
Link:https://legalclarity.org/forensic-disk-imaging-bit-for-bit-copies-and-evidence/
Source snippet
Every transfer of the physical evidence — from the moment of seizure through imaging, analysis...
17.
Source: youtube.com
Title: Hacking for UFOs and fighting for his life. Who is Gary Mc Kinnon? | Nord VPN
Link:https://www.youtube.com/watch?v=OImdnvQx7sQ
Source snippet
Digital Forensics Chain-of-Custody Explained | Evidence Handling & Cyber Law Guide...
18.
Source: youtube.com
Link:https://www.youtube.com/watch?v=3qTQUVYaGGk
Source snippet
Understanding the Need of Chain of Custody in Digital Forensics...
19.
Source: youtube.com
Title: What is chain of custody and why is it important for digital evidence?
Link:https://www.youtube.com/watch?v=9sJkM0bUF3c
Source snippet
Understanding Chain of Custody in Digital Forensics...
20.
Source: youtube.com
Title: Understanding Chain of Custody in Digital Forensics
Link:https://www.youtube.com/watch?v=vimQuaC3RYM
Source snippet
Hacking for UFOs and fighting for his life. Who is Gary McKinnon? | NordVPN...
21.
Source: ojp.gov
Link:https://ojp.gov/library/publications/dex-digital-evidence-provenance-supporting-reproducibility-and-comparison
22.
Source: ojp.gov
Link:https://ojp.gov/library/publications/forensic-examination-digital-evidence-guide-law-enforcement