Within Claim Checklist
Can the Claimed File Be Traced to the Breach?
A verified intrusion only supports a UFO claim when the alleged file can be tied to a specific host, path, account and access time.
On this page
- What breach records can establish
- How to map a file to a system
- Where the evidential link commonly breaks
Page outline Jump by section
Introduction
A confirmed computer intrusion does not, by itself, verify a claimed UFO-related discovery. In cases such as Gary McKinnon’s, the evidential question is narrower and more practical: can the alleged file or image be traced to a specific compromised computer, account, directory and moment in time? Only if that chain can be reconstructed does the breach provide meaningful support for the existence of the claimed material. Otherwise, the confirmed intrusion and the claimed UFO evidence remain separate propositions. Official records can establish that unauthorised access occurred, yet still leave unanswered whether a particular spreadsheet, image or database was ever present on the compromised system.[UK Parliament]publications.parliament.ukUK Parliament House of LordsUK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008…
What breach records can actually establish
Digital investigations are strongest when multiple independent records describe the same event. For a claimed UFO file, investigators would seek evidence answering four linked questions:
- Which host was accessed? The server name, IP address or asset inventory identifies the compromised machine.
- Which account was used? Authentication records show which credentials opened the session.
- When did access occur? Server logs, network timestamps and forensic timelines establish the relevant window.
- What files were accessed? File-system metadata, audit logs, application records or recovered local artefacts may show specific filenames or directories.
A confirmed breach therefore demonstrates access to a defined environment rather than proving every later description of its contents. Modern digital forensics treats these independent records as the foundation for reconstructing user activity because memory alone is considered much weaker evidence than contemporaneous system logs.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 2002)…
How a claimed file is mapped to a compromised system
To connect an alleged document to a verified intrusion, investigators attempt to build a continuous chain of evidence.
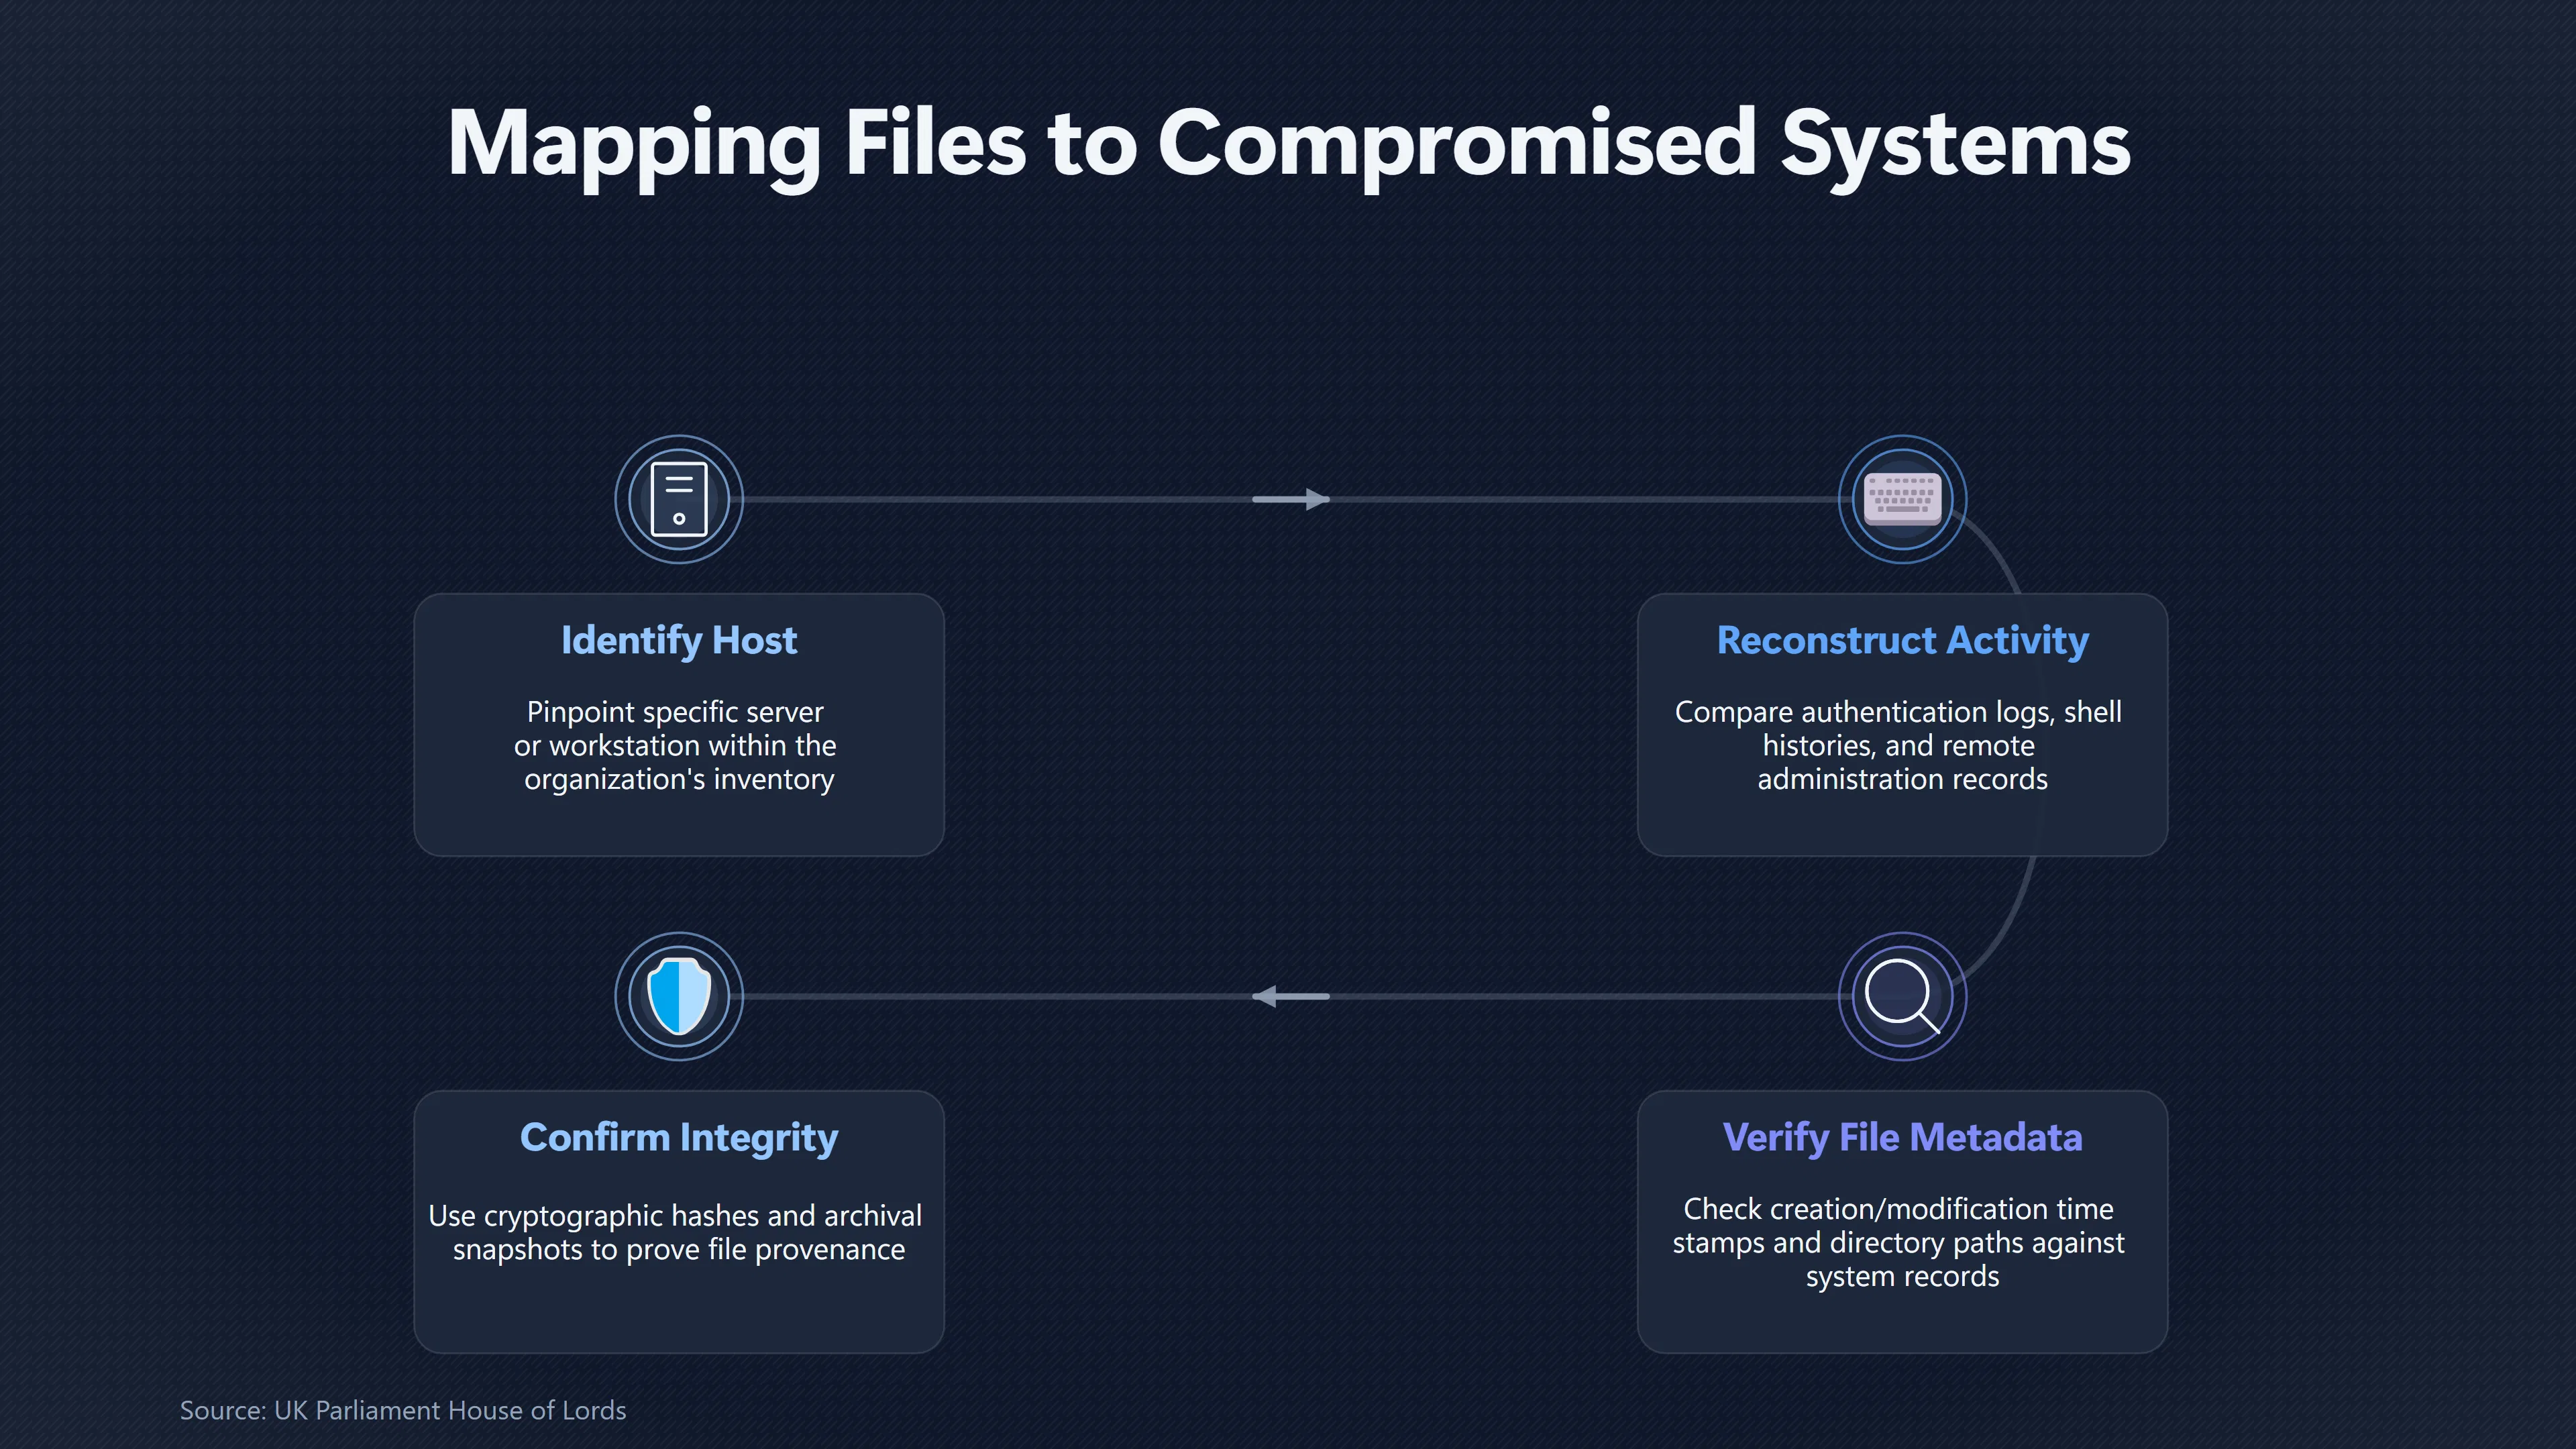
Identify the exact machine
General statements such as “a NASA computer” are rarely sufficient because agencies operate hundreds or thousands of systems with different purposes and access controls. A persuasive claim identifies:
- the organisation;
- the specific server or workstation;
- the directory or application involved;
- the approximate date and time of access.
Without those details, investigators cannot compare the claim against preserved logs or administrative records.
Reconstruct the user’s activity
Once a machine is identified, investigators compare several independent artefacts:
- server authentication logs;
- remote administration logs;
- file access timestamps;
- shell or command histories;
- temporary files;
- browser caches;
- forensic images of seized computers;
- incident-response documentation created during the breach.
Agreement across multiple artefacts substantially strengthens confidence that a claimed file was genuinely opened rather than reconstructed from memory after the event.
Verify the file itself
If the alleged file still exists, investigators would expect evidence such as:
- an original filename;
- directory path;
- creation and modification timestamps;
- metadata linking it to the host;
- cryptographic hashes demonstrating integrity;
- backup copies or archival snapshots.
These details make it possible to determine whether the file belonged on that system or appeared later from another source.

Applying this standard to the McKinnon case
Gary McKinnon’s unauthorised access is well documented in court records and United States indictments. Authorities alleged that he gained access to dozens of military and NASA computers between 2001 and 2002, copied password files, installed remote administration software on some systems and deleted logs and operating system files during certain intrusions.[parliament.uk]publications.parliament.ukUK Parliament House of LordsUK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008…
His best-known UFO claims concern:
- an Excel spreadsheet reportedly titled “Non-Terrestrial Officers”;
- another spreadsheet referring to ship-to-ship transfers;
- a satellite image allegedly depicting a cigar-shaped object.
The crucial evidential issue is that none of these claimed files has been independently linked through publicly available forensic evidence to a specific compromised host. The indictments describe the alleged computer intrusions and damage but do not identify or authenticate those UFO-related files. Likewise, the House of Lords judgment summarises the hacking allegations without confirming that such documents existed on the affected systems.[UK Parliament]publications.parliament.ukUK Parliament House of LordsUK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008…
This distinction is often overlooked. Confirmation that McKinnon accessed NASA or military computers is not equivalent to confirmation that the alleged spreadsheets or image were present on those computers.
Where the evidential chain commonly breaks
In historical hacking cases, the connection between a claimed discovery and a verified breach frequently fails at one of several points.
Missing contemporaneous copies
No publicly authenticated copy of the alleged spreadsheet or image has been produced. Without an original file, investigators cannot examine metadata, compare hashes or verify provenance.
Incomplete host attribution
Public accounts generally do not identify a specific server, directory structure or storage location for the alleged files. That prevents comparison with surviving administrative records.
Deleted or unavailable logs
Some official allegations state that system logs were deleted during parts of the intrusion. Even when deletion itself becomes evidence of unauthorised activity, missing logs reduce investigators’ ability to reconstruct exactly which files were viewed during a session.[Department of Justice]justice.govDepartment of JusticeBritish National Charged with Hacking Into N.J. Naval Weapons Station Computers, Disabling Network After Sept. 11 (N…
Reliance on retrospective memory
Most descriptions of the “Non-Terrestrial Officers” spreadsheet and associated image derive from McKinnon’s later recollections rather than contemporaneous forensic documentation. Human memory can remain sincere while still becoming less reliable over long periods, particularly regarding filenames, interfaces and contextual details.
Why breach confirmation alone is insufficient
From an evidential perspective, several different scenarios remain compatible with the confirmed hacking allegations:
- the described files genuinely existed on the compromised systems;
- genuine administrative files were later misinterpreted;
- details from multiple sessions became combined in memory;
- remembered filenames differed from their original wording;
- no such files existed despite the confirmed unauthorised access.
A verified breach eliminates uncertainty about whether an intrusion occurred. It does not, by itself, distinguish between those possibilities. Only independently corroborated digital evidence connecting the claimed file to a documented host, account, path and access time can do that.[UK Parliament]publications.parliament.ukUK Parliament House of LordsUK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008…
The practical test for future UFO hacking claims
When evaluating any future claim that a hacker discovered evidence of UFO programmes or hidden aerospace projects, the most informative question is not whether the intrusion happened but whether the alleged file can be traced through an unbroken evidential chain.
The strongest case would include independently preserved server logs, identifiable host information, recoverable file metadata, contemporaneous forensic copies and documentation showing that the claimed file resided on the compromised system during the verified period of access. Without that linkage, a confirmed breach supports only the fact of unauthorised access—not the authenticity or interpretation of the alleged UFO-related material.
Amazon book picks
Further Reading
Books and field guides related to Can the Claimed File Be Traced to the Breach?. Use these as the next step if you want deeper reading beyond the article.
Digital Evidence and Computer Crime
Digital Evidence and Computer Crime, Second Edition, is a hands-on resource that aims to educate students and professionals in the law en...
File System Forensic Analysis
The Definitive Guide to File System Analysis: Key Concepts and Hands-on Techniques Most digital evidence is stored within the computer's...
Forensic Discovery
This is an analysis of the major security weaknesses and loopholes of the Internet and of some solutions to those problems. The book info...
Incident Response & Computer Forensics
The definitive guide to incident response--updated for the first time in a decade! Thoroughly revised to cover the latest and most effect...
eBay marketplace picks
Marketplace Samples
Live-tested eBay searches with available results related to this page.
Selected fromcomputer security t shirt oneBay.co.uk.
Endnotes
1.
Source: publications.parliament.uk
Title: UK Parliament House of Lords
Link:https://publications.parliament.uk/pa/ld200708/ldjudgmt/jd080730/mckinn-1.htm
Source snippet
UK ParliamentHouse of Lords - Mckinnon V Government of The United States of America and AnotherJuly 30, 2008...
Published: July 30, 2008
2.
Source: justice.gov
Link:https://www.justice.gov/archive/criminal/cybercrime/press-releases/2002/mckinnonIndict.htm
Source snippet
Department of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 2002)...
Published: November 12, 2002
3.
Source: justice.gov
Link:https://www.justice.gov/archive/criminal/cybercrime/press-releases/2002/mckinnonIndict2.htm
Source snippet
Department of JusticeBritish National Charged with Hacking Into N.J. Naval Weapons Station Computers, Disabling Network After Sept. 11 (N...
4.
Source: uscode.house.gov
Link:https://uscode.house.gov/view.xhtml?edition=prelim&num=0&req=granuleid%3AUSC-prelim-title50-section3143
Source snippet
23, 2026 — 50 USC 3143: Operational files of the National Reconnaissance Office Text contains those laws in effect on June 23, 2026 From...
Published: June 23, 2026
5.
Source: uscode.house.gov
Link:https://uscode.house.gov/view.xhtml?edition=2023&num=0&req=granuleid%3AUSC-2023-title50-section3144
Source snippet
3, 2024 — 50 USC 3144: Operational files of the National Security Agency Back to Original Document << Previous TITLE 50 / CHAPTER 44 / SU...
6.
Source: justice.gov
Title: Office of Information Policy | Judicial Watch, Inc
Link:https://www.justice.gov/oip/judicial-watch-inc-v-us-secret-service-726-f3d-208-dc-cir-aug-30-2013-garland-c-j
Source snippet
v. U.S. Secret Service, 726 F.3d 208 (D.C. Cir. Aug. 30, 2013) (Garland, C. J.) | United States Department of JusticeAugust 30, 2013 — JU...
Published: August 30, 2013
7.
Source: publications.parliament.uk
Title: uk House of Lords
Link:https://publications.parliament.uk/pa/ld200809/ldjudgmt/jd090304/rgrj-1.htm
8.
Source: GOV.UK
Title: latest on [gary mckinnon case]({{ ‘mc-kinnon-case/’ | relative_url }})
Link:https://www.gov.uk/government/news/latest-on-gary-mckinnon-case
Source snippet
on Gary McKinnon case - GOV.UKNovember 4, 2010 — LATEST ON GARY MCKINNON CASE Find out the latest position on the Glasgow-born systems ad...
Published: November 4, 2010
Additional References
9.
Source: nsa.gov
Link:https://www.nsa.gov/serve-from-netstorage/news-features/declassified-documents/index.html
Source snippet
Declassification & TransparencyDECLASSIFICATION & TRANSPARENCY As NSA/CSS reviews records under the Freedom of Information Act or Mandato...
10.
Source: computerweekly.com
Link:https://www.computerweekly.com/news/2240086153/Gary-McKinnon-broke-into-73000-US-government-computers-Lords-told
Source snippet
Gary McKinnon broke into 73,000 US government computers, Lords told | Computer WeeklyJune 16, 2008 — GARY MCKINNON BROKE INTO 73,000 US G...
Published: June 16, 2008
11.
Source: theguardian.com
Link:https://www.theguardian.com/technology/2008/jun/16/hacking.internationalcrime
Source snippet
June 16, 2008 — This article is more than 18 years old BRITISH HACKER SHOULD NOT BE EXTRADITED TO US, LORDS TOLD This article is more tha...
Published: June 16, 2008
12.
Source: scribd.com
Link:https://www.scribd.com/document/839289048/digital-forensic
Source snippet
FROM IN OR ABOUT SEPTEMBER 2001, THROUGH ON OR ABOUT MARCH 19, 2002, WITHIN THE EASTERN DISTRICT OF VIRGINIA, AND ELSEWHERE, THE DEFENDAN...
Published: March 19, 2002
13.
Source: youtube.com
Link:https://www.youtube.com/watch?v=b-3RhyfYk58
Source snippet
Hacking for UFOs and fighting for his life. Who is Gary McKinnon? | NordVPN is directly relevant because it details the historical breach...
14.
Source: youtube.com
Title: Hacking for UFOs and fighting for his life. Who is Gary Mc Kinnon? | Nord VPN
Link:https://www.youtube.com/watch?v=OImdnvQx7sQ
Source snippet
Chapter 08: Your Systems Were Breached. Now What? The Incident Response Playbook...
15.
Source: youtube.com
Title: Chapter 08: Your Systems Were Breached. Now What? The Incident Response Playbook
Link:https://www.youtube.com/watch?v=OZNyZT2ErRQ
Source snippet
Ancient Aliens: Hacking NASA Secrets (Season 12, Episode 9) | History...
16.
Source: youtube.com
Link:https://www.youtube.com/watch?v=8XuqFwgFYUk
Source snippet
Ancient Aliens: TOP 10 ALIEN ENCOUNTERS OF 2023 | PART 2 | History...
17.
Source: youtube.com
Title: Ancient Aliens: Hacking NASA Secrets (Season 12, Episode 9) | History
Link:https://www.youtube.com/watch?v=20rWFDfh68Y
Source snippet
Introduction to Log Management...