Within Rome Laboratory
How Investigators Watched the Rome Hackers in Real Time
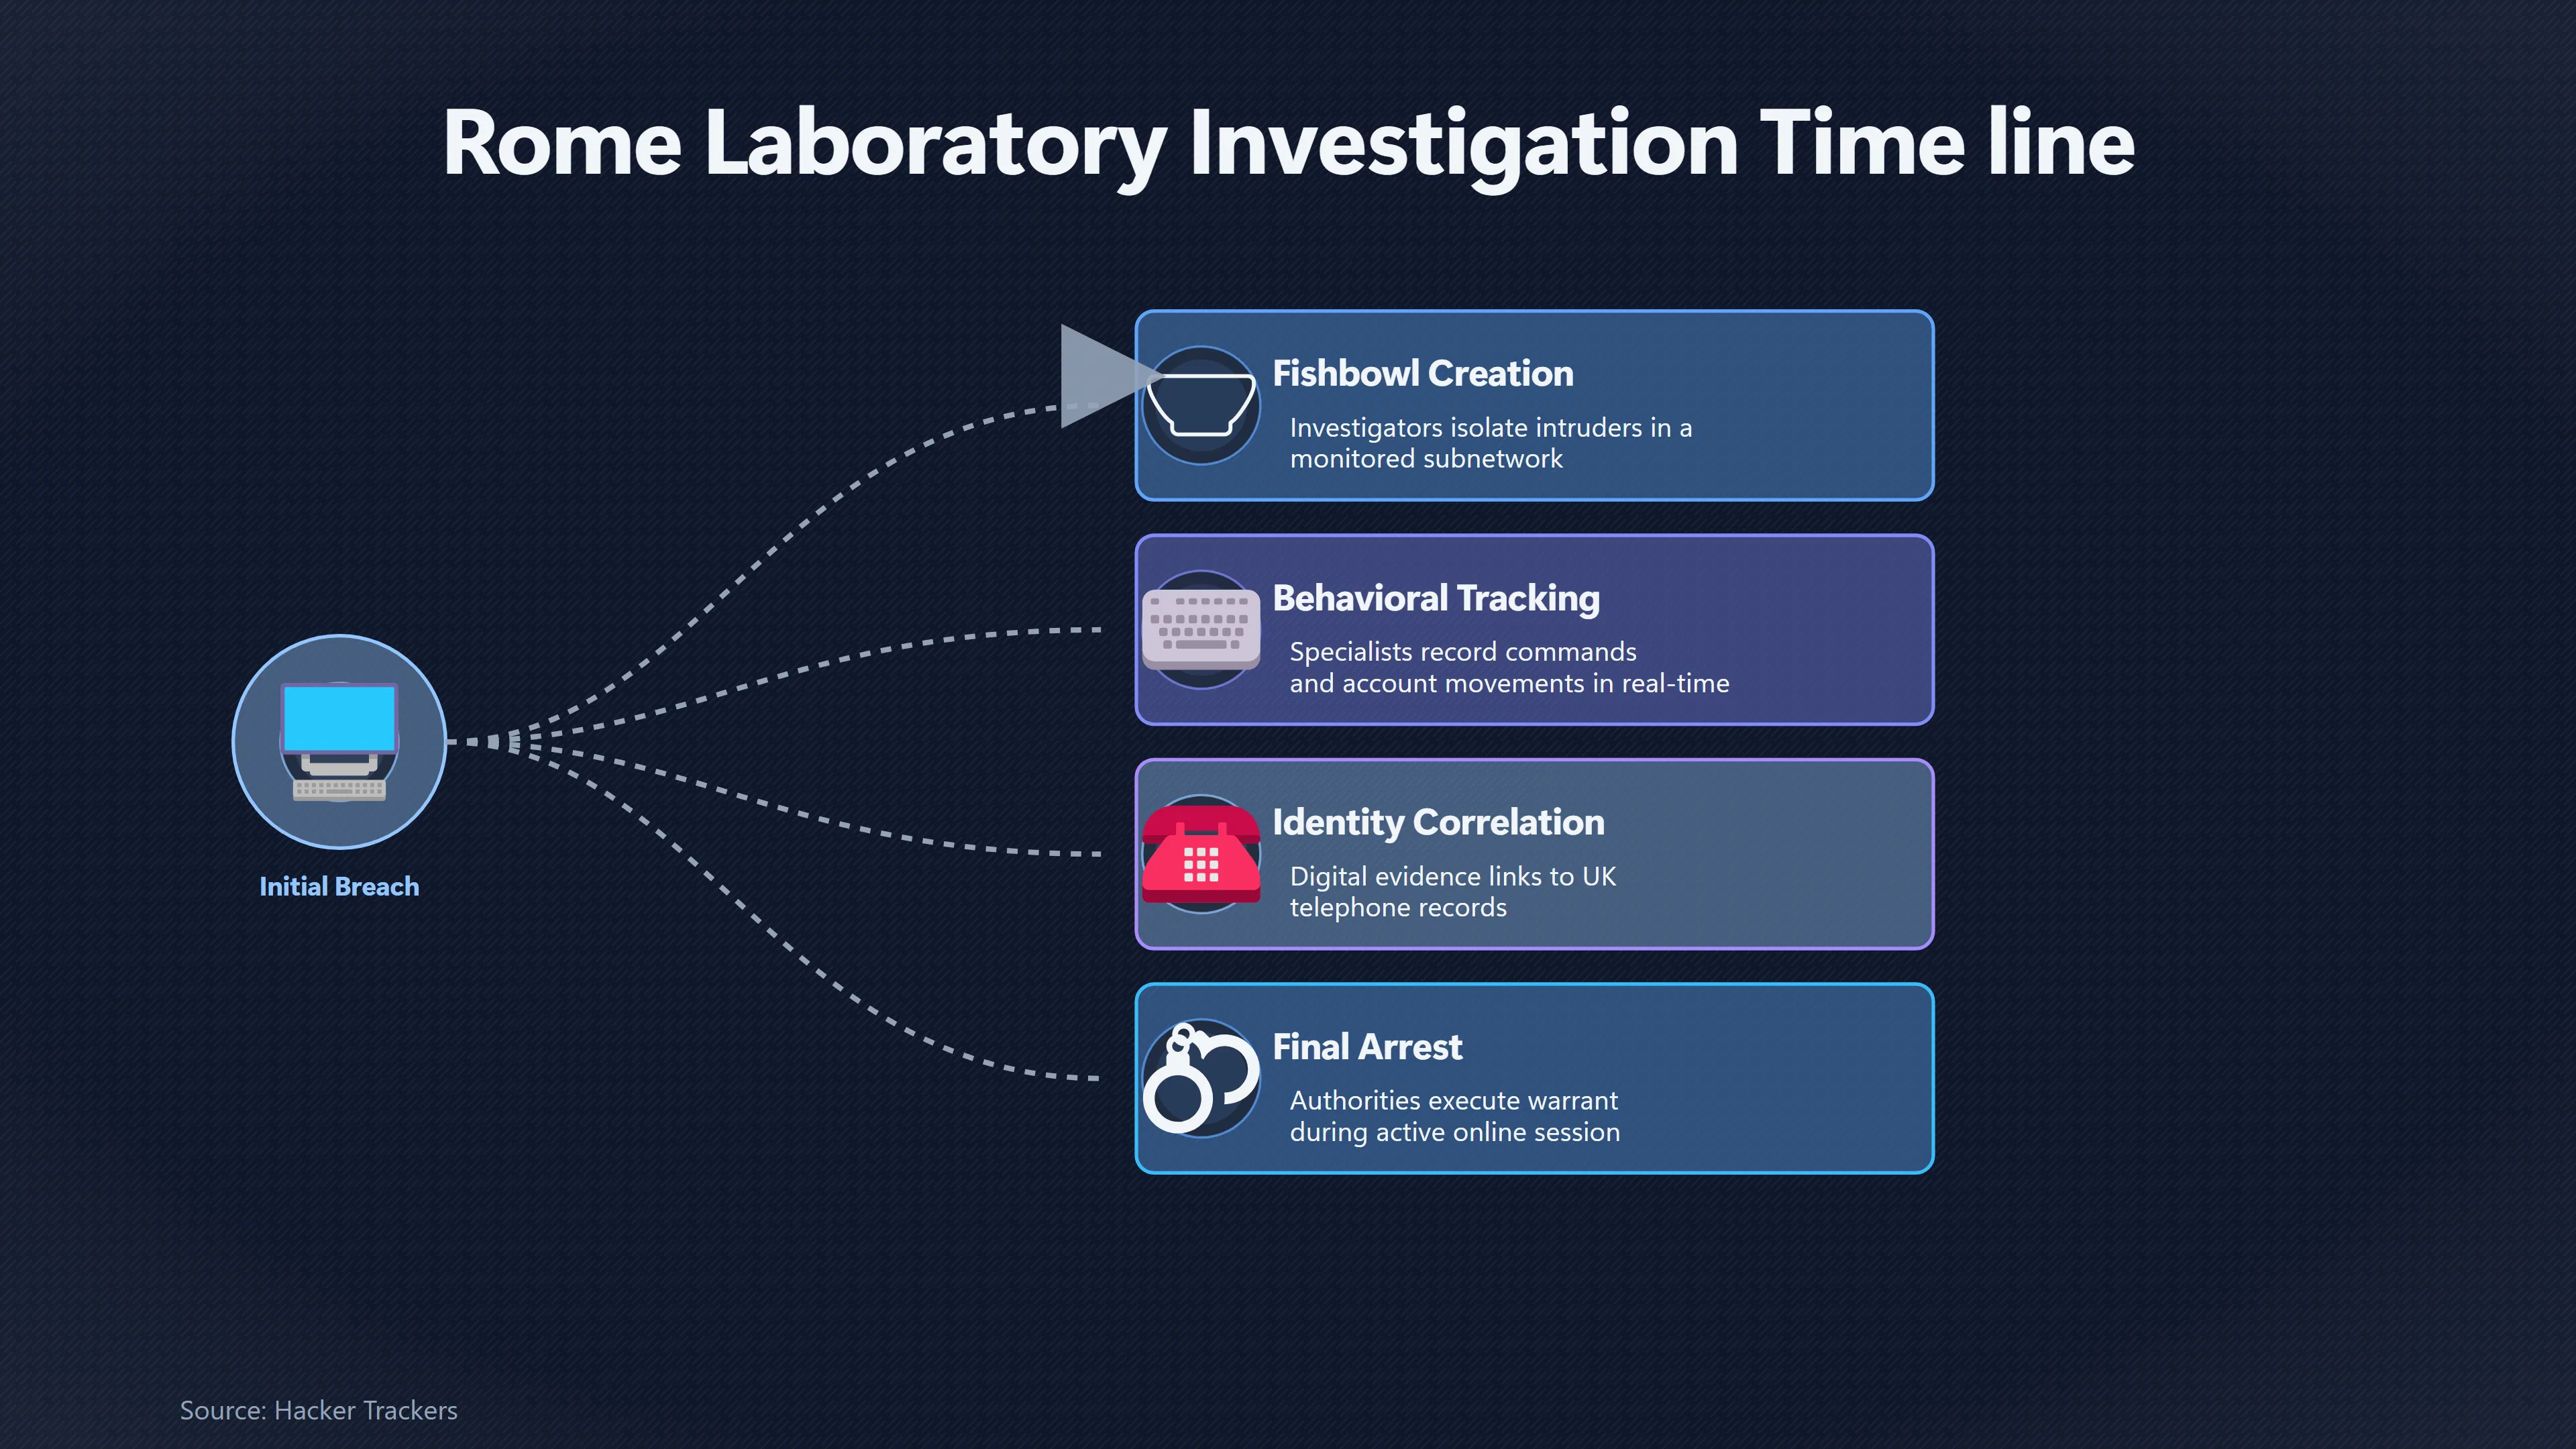
Investigators restricted the attackers to a monitored area, recording keystrokes while combining technical surveillance with telephone and informant evidence.
On this page
- Why defenders left limited access open
- How keystroke monitoring contained the threat
- How police and telecom evidence identified Richard Pryce
Page outline Jump by section
Introduction
One of the most unusual aspects of the 1994 Rome Laboratory hacking incident was that investigators did not immediately eject the intruders once the compromise had been discovered. Instead, Air Force specialists deliberately isolated the attackers inside what officials later described as an “electronic fishbowl”—a controlled portion of the network where their activity could be observed, recorded and correlated with traditional police investigation. This decision transformed the case from a straightforward incident response into one of the earliest documented examples of active cyber surveillance supporting a criminal investigation. Rather than simply restoring systems, investigators prioritised learning who the attackers were, how they operated and where they were connecting from, eventually identifying the teenager using the handle Datastream Cowboy as Richard Pryce in the United Kingdom.[National Security Archive]nsarchive.gwu.eduNational Security Archive United States General Accounting OfficeNational Security ArchiveUnited States General Accounting OfficeApril 12, 2026…
Why investigators left limited access open
By the time Rome Laboratory detected password-sniffing software on its systems, the attackers had already compromised numerous machines and stolen user credentials. Completely disconnecting every affected system would have halted the immediate activity but would also have eliminated the opportunity to trace the people responsible.
Instead, investigators from the Air Force Office of Special Investigations (AFOSI), working alongside the Air Force Information Warfare Center and other agencies, regained control of the network while creating an isolated environment where the attackers could continue operating without unrestricted access to the wider infrastructure. The General Accounting Office later described this controlled environment as an electronic fishbowl, noting that the intruders’ access was deliberately limited to a single isolated subnetwork where their actions could be monitored.[National Security Archive]nsarchive.gwu.eduNational Security Archive United States General Accounting OfficeNational Security ArchiveUnited States General Accounting OfficeApril 12, 2026…
This approach reflected an important strategic trade-off:
- immediate removal of the attackers would protect systems but sacrifice intelligence;
- controlled observation increased short-term operational risk while greatly improving the chances of identifying those responsible;
- isolation reduced the likelihood that the hackers could continue expanding into sensitive systems.
The strategy foreshadowed techniques now common in modern cyber defence, such as deception environments, containment networks and monitored “honeynets”, although the Rome investigation predated most formal terminology.
How keystroke monitoring contained the threat
The fishbowl was valuable because investigators could watch the attackers’ behaviour in real time rather than reconstructing events afterwards from system logs.
Reports from AFOSI participants describe continuous surveillance in which specialists remained in the operations room for weeks while silent alarms indicated when the hackers returned. Their monitoring allowed investigators to observe:
- commands entered by the intruders;
- movement between compromised accounts;
- attempts to pivot into connected organisations;
- the relationship between the two hacker aliases, Datastream Cowboy and Kuji.[soldierx.com]soldierx.comDatastream Cowboy | SOLDIERX.COMSOLDIERX.COM NOBODY CAN STOP INFORMATION INSEMINATION DATASTREAM COWBOY IRL Name: Richard Pryce Biography…
Investigators concluded that Kuji appeared technically more sophisticated and often acted as a mentor, while Datastream carried out much of the practical intrusion activity. Continuous observation also revealed how captured passwords were reused to compromise additional organisations through Rome Laboratory’s trusted connections.[all.net]all.netHacker TrackersHacker Trackers
Importantly, monitoring was not passive. By restricting the attackers to controlled systems, investigators reduced the danger of additional compromise while still allowing enough activity to gather evidence. This balance between operational security and investigative value became one of the defining features of the case.
How police and telecom evidence identified Richard Pryce
Technical monitoring alone could not reveal the real identity of Datastream Cowboy because the attacks travelled through a complicated chain of international systems spanning Europe, South America, Mexico, Hawaii and Internet providers in the United States.
The breakthrough came from combining digital evidence with conventional policing.
An AFOSI informant who participated in online hacker communities produced earlier email exchanges in which Datastream Cowboy had:
- claimed to be a 16-year-old from the United Kingdom;
- boasted about targeting “.mil” systems because they were insecure;
- provided the telephone number for his own bulletin board system.
That telephone number gave investigators a tangible lead that pure network tracing had failed to provide. AFOSI shared the information with New Scotland Yard, which identified the household associated with the line. British Telecom then implemented pen-register monitoring that recorded outgoing dialled numbers. Investigators noticed a striking pattern: whenever Rome Laboratory experienced another intrusion, someone at the same residence was simultaneously engaging in illegal “phone phreaking” to obtain free international telephone connections through British Telecom.[Intelligence Resource Program]irp.fas.orgIntelligence Resource Program Security in Cyberspace APPENDIX BIntelligence Resource ProgramSecurity in Cyberspace APPENDIX B - Case Study Rome Laboratory, Griffiss Air Force Base, NY Intrusion…
This correlation linked technical evidence with telecommunications records and established that the attacks consistently originated from the same household despite their complex international routing.
From surveillance to arrest
The investigation did not end once Richard Pryce became the principal suspect. Authorities continued monitoring long enough to strengthen the evidential chain before acting.
British and American investigators coordinated closely, with Scotland Yard preparing to arrest Pryce while AFOSI continued observing activity from Rome Laboratory. Contemporary accounts describe investigators waiting until Datastream Cowboy was actively online before executing the warrant, ensuring both the suspect and the equipment were caught during live activity. Pryce was arrested in May 1994 and later prosecuted in the United Kingdom under the Computer Misuse Act.[kujimedia.com]kujimedia.comKuji Media Corporation Ltd. » Blog Archive » THE SCHOOLBOY SPY. Sunday TimesKuji Media Corporation Ltd. » Blog Archive » THE SCHOOLBOY SPY. Sunday TimesJune 26, 2008…
Although the identity of the second hacker, Kuji, remained unresolved in the official investigation, the evidence gathered against Pryce demonstrated the value of combining network monitoring with traditional investigative techniques.
The lasting significance of the fishbowl strategy
The electronic fishbowl became one of the earliest widely cited examples of integrating cyber defence with criminal investigation instead of treating them as separate activities.
Several lessons emerged from the Rome Laboratory case:
- Containment can be more valuable than immediate eviction. Investigators accepted carefully managed short-term risk to obtain evidence that would identify an attacker rather than merely interrupt one intrusion.
- Human intelligence remained essential. The decisive breakthrough came not from sophisticated tracing technology alone but from an online informant, email evidence and telephone records.
- Cross-border cooperation proved critical. AFOSI, the Air Force Information Warfare Center, New Scotland Yard and British Telecom each contributed different pieces of the investigation.
- Behavioural evidence complemented technical evidence. Watching how the hackers navigated the network revealed relationships, objectives and operational habits that log files alone could not fully explain.[gwu.edu]nsarchive.gwu.eduNational Security Archive United States General Accounting OfficeNational Security ArchiveUnited States General Accounting OfficeApril 12, 2026…
Within the broader story of the Rome Laboratory breach—and the later public interest surrounding hackers such as Gary McKinnon—the electronic fishbowl stands out because it demonstrated that effective cyber investigations depend not only on technical expertise but also on patience, controlled containment and the careful integration of digital and conventional policing techniques.
Amazon book picks
Further Reading
Books and field guides related to How Investigators Watched the Rome Hackers in Real Time. Use these as the next step if you want deeper reading beyond the article.
The Practice of Network Security Monitoring
Network security is not simply about building impenetrable walls—determined attackers will eventually overcome traditional defenses. The...
Ghost in the Wires
In this "intriguing, insightful and extremely educational" novel, the world's most famous hacker teaches you easy cloaking and counter-me...
Network Intrusion Detection
This training aid and resource guide includes some theory and lots of practical advice from a world-class authority on the subject of net...
eBay marketplace picks
Marketplace Samples
Live-tested eBay searches with available results related to this page.
Selected fromretro computer art oneBay.co.uk.
Endnotes
1.
Source: all.net
Title: Hacker Trackers
Link:https://all.net/books/iw/iwarstuff/www.af.mil/news/airman/0496/hacker.htm
2.
Source: kujimedia.com
Title: Kuji Media Corporation Ltd. » Blog Archive » THE SCHOOLBOY SPY. Sunday Times
Link:https://www.kujimedia.com/the-schoolboy-spy-sunday-times/
Source snippet
Kuji Media Corporation Ltd. » Blog Archive » THE SCHOOLBOY SPY. Sunday TimesJune 26, 2008...
Published: June 26, 2008
3.
Source: phrack.org
Link:https://phrack.org/issues/49/16
Source snippet
The comings and goings of Datastream Cowbo...
4.
Source: kujimedia.com
Title: Kuji Media Corporation Ltd
Link:https://www.kujimedia.com/tag/datastream-cowboy/
Source snippet
» Datastream CowboyJune 26, 2008 — I then began a systematic attack on each of the ones I could find with online equivalents. I had many...
Published: June 26, 2008
5.
Source: kujimedia.com
Title: Kuji Media Corporation Ltd
Link:https://www.kujimedia.com/tag/datastream-cowboy/page/2/
Source snippet
» Datastream CowboyJune 26, 2008 — If a foreign intelligence service was involved, it is impossible to know which one, as many countries...
Published: June 26, 2008
6.
Source: kujimedia.com
Title: Kuji Media Corporation Ltd
Link:https://www.kujimedia.com/tag/richard-pryce/page/2/
Source snippet
» Richard PryceJune 26, 2008 — Naive, too. Before long, the informant had established that Datastream Cowboy lived in the United Kingdom...
Published: June 26, 2008
7.
Source: nsarchive.gwu.edu
Title: National Security Archive United States General Accounting Office
Link:https://nsarchive.gwu.edu/sites/default/files/documents/2700086/Document-10b.pdf
Source snippet
National Security ArchiveUnited States General Accounting OfficeApril 12, 2026...
Published: April 12, 2026
8.
Source: irp.fas.org
Title: Intelligence Resource Program Security in Cyberspace APPENDIX B
Link:https://irp.fas.org/congress/1996_hr/s960605b.htm
Source snippet
Intelligence Resource ProgramSecurity in Cyberspace APPENDIX B - Case Study Rome Laboratory, Griffiss Air Force Base, NY Intrusion...
9.
Source: soldierx.com
Link:https://www.soldierx.com/hdb/Datastream-Cowboy
Source snippet
Datastream Cowboy | SOLDIERX.COMSOLDIERX.COM NOBODY CAN STOP INFORMATION INSEMINATION DATASTREAM COWBOY IRL Name: Richard Pryce Biography...
Additional References
10.
Source: slidetodoc.com
Link:https://slidetodoc.com/introducing-digital-forensics-peter-sommer-london-school-of/
Source snippet
Introducing Digital Forensics Peter Sommer London School ofImage: GAO Report Image: GAO Report Image: Rome Labs Sources: • I was hired by...
11.
Source: slidetodoc.com
Link:https://slidetodoc.com/introducing-digital-forensics-peter-sommer-london-school-of-2/
Source snippet
Introducing Digital Forensics Peter Sommer London School ofRome Labs Sources: • I was hired by UK defense lawyers (in the English legal s...
12.
Source: leveson.robertsharp.co.uk
Link:https://leveson.robertsharp.co.uk/E/chapter3/
Source snippet
INTRODUCTION 1.1 The information arising from Operation Reproof caused the Office of the Information Commissioner (ICO) to focus attentio...
13.
Source: independent.co.uk
Title: Fine for boy who hacked into Pentagon | The Independent | The Independent
Link:https://www.independent.co.uk/news/fine-for-boy-who-hacked-into-pentagon-1274204.html
Source snippet
March 22, 1997 — FINE FOR BOY WHO HACKED INTO PENTAGON Saturday 22 March 1997 00:02 GMT * * Bookmark A British teenager who got a D grade...
Published: March 22, 1997
14.
Source: trulyadventure.us
Link:https://www.trulyadventure.us/the-hacker
Source snippet
Jim Christy, 42, then director of Computer Crime Investigations (CCI) for the Air Force Office of Special...
15.
Source: computing.co.uk
Title: DAN SABBAGH HAS THE INSIDE INFORMATION Next Mo
Link:https://www.computing.co.uk/news/1835011/silence-falls-exchange-moves-electronic-dealing
Source snippet
Silence falls as Exchange moves to electronic dealingSILENCE FALLS AS EXCHANGE MOVES TO ELECTRONIC DEALING AFTER WEEKS OF WEEKEND TESTING...
16.
Source: korben.info
Title: Deux ados cherchant des OVNIS ont failli lancer la WW3
Link:https://korben.info/kuji-datastream-cowboy-pentagone-hack-1996-histoire-complete.html
Source snippet
Ils laissent des traces partout, copient des gigaoctets de données sans discrimination, et communi...
17.
Source: casemine.com
Title: Vogon International Ltd
Link:https://www.casemine.com/judgement/uk/5a8ff7ba60d03e7f57eb1966
Source snippet
v The Serious Fraud Office | England and Wales High Court (Technology & Construction Court) | Judgment | Law | CaseMineJuly 15, 2003 — Ci...
Published: July 15, 2003
18.
Source: youtube.com
Title: A Tale of Two UFO Hackers: Matthew Bevan & Gary Mc Kinnon | True Crime
Link:https://www.youtube.com/watch?v=rksYZZgSPcY
Source snippet
Kaise Ek 16 Saal Ke Hacker Ne US Defense Ko Hila Diya The Darknet Hub · 5.2K views...
19.
Source: read.uolpress.co.uk
Link:https://read.uolpress.co.uk/read/electronic-evidence-and-electronic-signatures/section/f179427f-bc7c-411f-923f-4d61b6d0c775
Source snippet
2[1998] 2 WLUK 562, (1998) 2 Cr App R 171, [1998] CLY 984. 3(1998) 2 Cr App R 171 at 178E. 10.18...