Within Access vs Proof
What Would Make a Leaked UFO File Verifiable
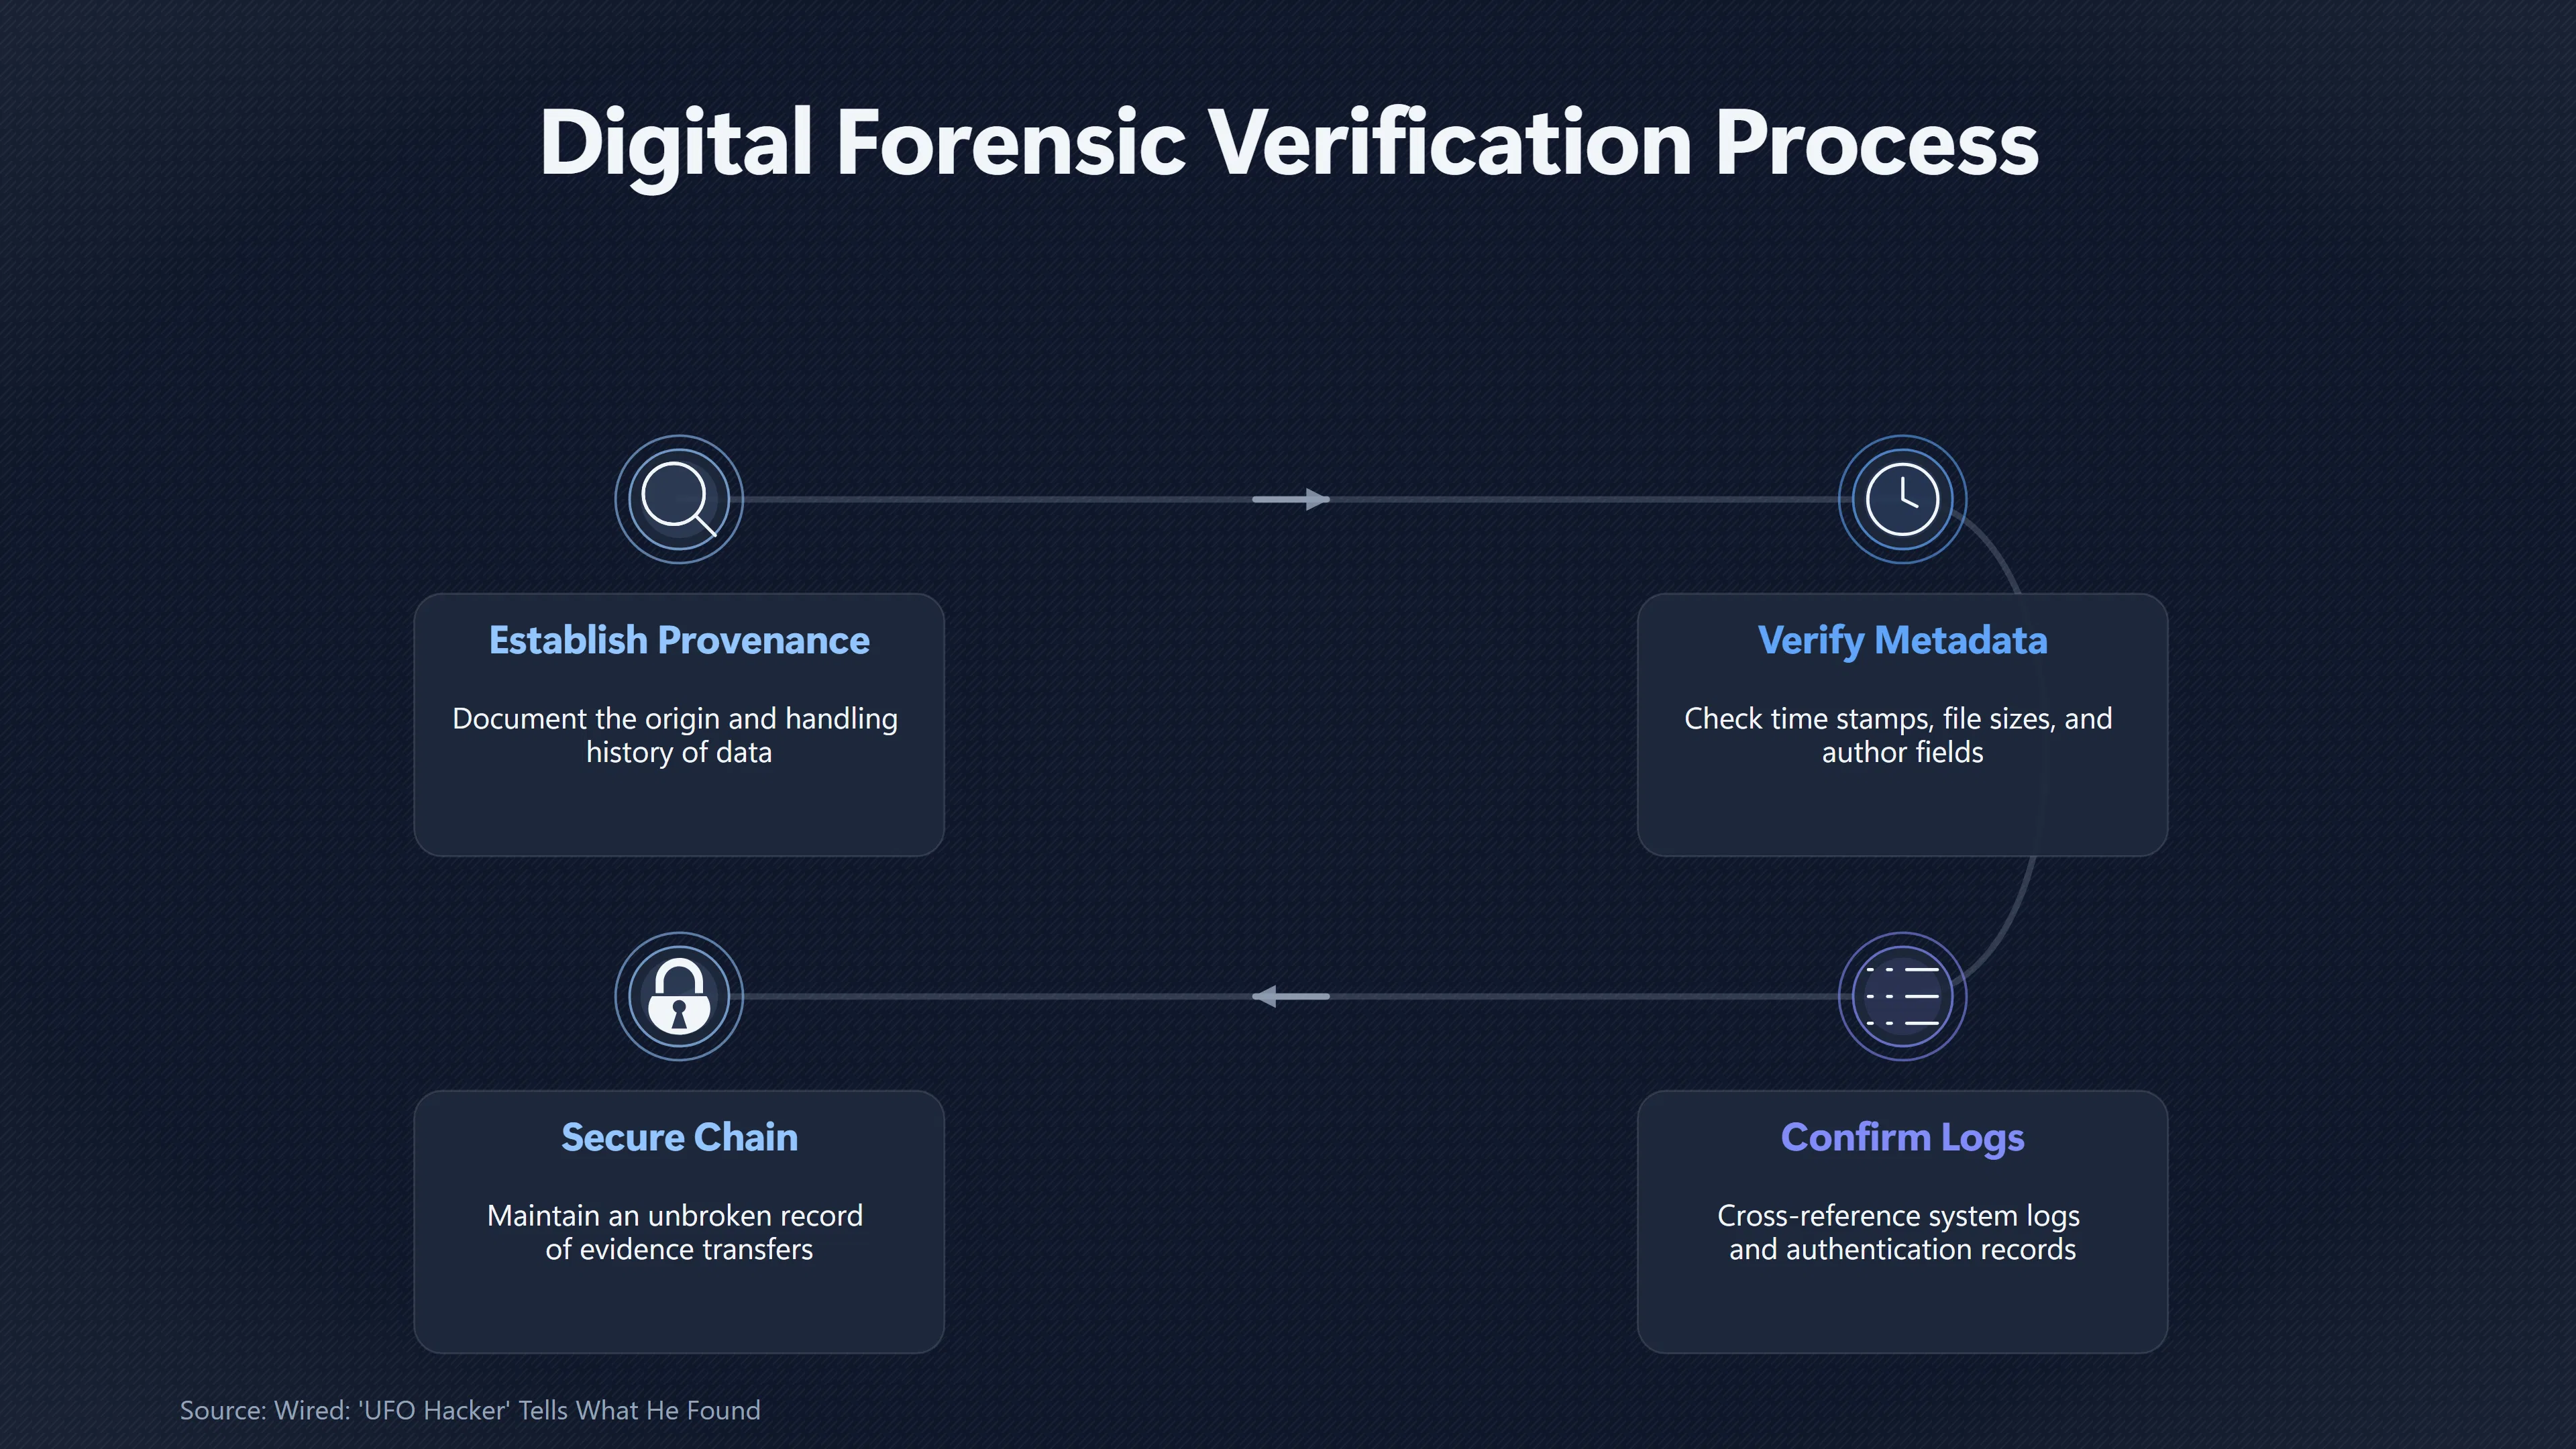
A claimed UFO file becomes testable only when its source, metadata, authorship, logs and chain of custody can be independently checked.
On this page
- Source systems, filenames and metadata
- Authorship, access logs and chain of custody
- How to rule out drafts, jokes and misunderstood records
Page outline Jump by section
Introduction
Claims that a hacker found secret UFO files on a government computer are not automatically evidence that those files were genuine. The central question is not whether a computer was accessed, but whether any alleged document, spreadsheet or image can be independently authenticated. In the context of Gary McKinnon’s claims, this distinction is especially important. McKinnon consistently described seeing unusual files, including an alleged spreadsheet headed “Non-Terrestrial Officers” and an image of an unidentified object, but no complete copies of those files have been produced for independent examination. As a result, the claims remain largely testimonial rather than documentary.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20…
For any alleged UFO file originating from an unauthorised breach, credibility depends on the same digital forensic principles used in criminal investigations, corporate incident response and intelligence inquiries. Without verifiable provenance, preserved metadata and a documented chain of custody, even an apparently remarkable file cannot reliably establish that a government possessed or concealed extraordinary information.
What Would Make a Leaked UFO File Verifiable
A leaked file becomes substantially more credible only when multiple independent pieces of evidence point to the same conclusion. Digital investigators generally look for provenance—the documented history of where data originated and how it was handled—rather than relying on the file’s contents alone. NIST defines provenance and chain of custody as records that document a file’s origin, ownership, handling and transfers throughout its lifecycle.[NIST Computer Security Resource Center]csrc.nist.govComputer Security Resource Centerdata provenanceNIST Computer Security Resource Centerdata provenance - Glossary | CSRC…
In practice, an alleged UFO document would become far more persuasive if investigators could independently verify:
- the original computer or server where it resided;
- the complete original file rather than a screenshot or recollection;
- intact filesystem metadata;
- consistent timestamps;
- corroborating system logs;
- confirmation from multiple independent sources.
Without these elements, extraordinary interpretations remain difficult to distinguish from misunderstanding, incomplete observation or fabrication.
Source Systems, Filenames and Metadata
The first question is where the file came from.
A genuine government record normally exists within a wider technical environment. Investigators would expect to identify the server, directory structure, operating system, storage medium and account that contained the document. They would also compare surrounding files to determine whether the alleged document fits naturally within the system or appears to have been inserted later.
Useful metadata would include:
- original filename and extension;
- creation, modification and access timestamps;
- file size;
- author fields where applicable;
- document revision history;
- cryptographic hashes showing that the file has not changed.
Digital forensics places considerable weight on metadata because it often reveals relationships that are difficult to fabricate consistently across an entire system. Modern forensic practice also emphasises cross-verifying filesystem artefacts rather than relying upon a single recovered file in isolation.[NIST]nist.govprovenience based cross verification digital forensic artifacts applied ntfsProvenience-based cross-verification of digital forensic artifacts applied to NTFS | NISTFebruary 19, 2024…
In McKinnon’s case, no original spreadsheet, image file or preserved metadata has entered the public domain. His descriptions therefore cannot be tested against the normal forensic indicators that would establish authenticity.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20…
Authorship, Access Logs and Chain of Custody
Even an authentic file found on a government computer would not automatically prove its contents.
The next stage is determining who created it, who edited it and whether anyone else accessed it. Enterprise systems frequently retain information such as user accounts, audit logs, revision histories and backup records that help reconstruct a document’s lifecycle.
Important questions include:
- Which authenticated user created the file?
- Which department owned the directory?
- Was the document routinely edited by multiple users?
- Did backup systems preserve earlier versions?
- Do network or authentication logs confirm the file’s existence at the claimed time?
Equally important is maintaining an unbroken chain of custody after discovery. Every transfer of the evidence should be documented so later investigators can demonstrate that the file was not altered during analysis. These principles are standard throughout digital forensic practice because undocumented handling weakens confidence in the evidence regardless of its contents.[NIST Computer Security Resource Center]csrc.nist.govComputer Security Resource Centerchain of custodyNIST Computer Security Resource Centerchain of custody - Glossary | CSRC…
If a hacker merely reports seeing a file but cannot preserve it, investigators lose the opportunity to perform these independent checks.
How to Rule Out Drafts, Jokes and Misunderstood Records
Context often matters more than a striking filename.
Government and military networks routinely contain draft documents, test databases, training exercises, fictional scenarios and placeholder records. Technical abbreviations may also have entirely ordinary meanings unfamiliar to outsiders.
To distinguish an extraordinary document from an ordinary administrative file, investigators would ask:
- Does the terminology match known organisational conventions?
- Is the document referenced elsewhere?
- Do related records support its claims?
- Does it appear in official inventories or backups?
- Is the naming consistent with genuine departmental practice?
An isolated spreadsheet title or partial screenshot is therefore insufficient. A seemingly dramatic filename may reflect a simulation, an internal joke, an unfinished draft or terminology whose meaning becomes clear only when viewed alongside surrounding documentation.
Independent corroboration is essential because genuine classified programmes generally leave multiple administrative traces rather than a single unexplained document.

Applying These Standards to the McKinnon Claims
McKinnon stated that he briefly viewed what he believed was an unedited NASA image showing a cigar-shaped object and an Excel spreadsheet referring to “Non-Terrestrial Officers.” He has also explained that his slow internet connection prevented him from downloading the image before the session ended. These accounts have remained broadly consistent over time, but they are supported primarily by his own testimony rather than preserved digital evidence.[Reddit]reddit.comWired: 'UFO Hacker' Tells What He FoundWired: 'UFO Hacker' Tells What He Found - June 21, 2006…
Because the alleged files were never publicly produced in their original form:
- no metadata has been independently examined;
- no filenames or directory structures have been verified;
- no cryptographic hashes exist for comparison;
- no authenticated chain of custody has been established;
- no access logs have been released confirming the specific files described.
This does not demonstrate that McKinnon’s recollections were false. Equally, it means they cannot presently be verified using the standards normally applied to digital evidence.
Why Authentication Matters More Than the Breach
A successful intrusion establishes that unauthorised access occurred, not that every claimed discovery accurately reflects what existed on the target system. The evidential burden shifts from proving access to proving provenance.
For alleged UFO files, convincing evidence would require a reproducible digital record that independent experts could inspect, authenticate and compare against system logs and organisational records. Until such material exists, claims based solely on recollection or unpreserved observations remain significantly weaker than claims supported by original files with verifiable provenance, intact metadata and an unbroken chain of custody.
Amazon book picks
Further Reading
Books and field guides related to What Would Make a Leaked UFO File Verifiable. Use these as the next step if you want deeper reading beyond the article.
Digital Evidence and Computer Crime: Forensic Science, Comput...
Digital Evidence and Computer Crime, Third Edition, provides the knowledge necessary to uncover and use digital evidence effectively in a...
File System Forensic Analysis
The Definitive Guide to File System Analysis: Key Concepts and Hands-on Techniques Most digital evidence is stored within the computer's...

The Craft of Research
Rating: 4.3/5 from 6 Google Books ratings
Since 1995, students, researchers, and professionals have turned to The Craft of Research for clear and helpful guidance on how to conduc...
Calling Bullshit: The Art of Skepticism in a Data-Driven World
Bullshit isn’t what it used to be. Now, two science professors give us the tools to dismantle misinformation and think clearly in a world...
eBay marketplace picks
Marketplace Samples
Live-tested eBay searches with available results related to this page.
Selected fromdigital forensics kit oneBay.co.uk.
Endnotes
1.
Source: justice.gov
Link:https://www.justice.gov/archive/criminal/cybercrime/press-releases/2002/mckinnonIndict.htm
Source snippet
Department of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20...
2.
Source: reddit.com
Title: Wired: ‘UFO Hacker’ Tells What He Found
Link:https://www.reddit.com/r/UFOs/comments/t01nyf
Source snippet
Wired: 'UFO Hacker' Tells What He Found - June 21, 2006...
Published: June 21, 2006
3.
Source: csrc.nist.gov
Title: Computer Security Resource Centerdata provenance
Link:https://csrc.nist.gov/glossary/term/data_provenance
Source snippet
NIST Computer Security Resource Centerdata provenance - Glossary | CSRC...
4.
Source: csrc.nist.gov
Title: Computer Security Resource Centerchain of custody
Link:https://csrc.nist.gov/glossary/term/chain_of_custody
Source snippet
NIST Computer Security Resource Centerchain of custody - Glossary | CSRC...
5.
Source: csrc.nist.gov
Title: Computer Security Resource Centerprovenance
Link:https://csrc.nist.gov/glossary/term/Provenance
Source snippet
NIST Computer Security Resource Centerprovenance - Glossary | CSRC...
6.
Source: nist.gov
Title: provenience based cross verification digital forensic artifacts applied ntfs
Link:https://www.nist.gov/publications/provenience-based-cross-verification-digital-forensic-artifacts-applied-ntfs
Source snippet
Provenience-based cross-verification of digital forensic artifacts applied to NTFS | NISTFebruary 19, 2024...
Published: February 19, 2024
7.
Source: nist.gov
Title: Digital Investigation Techniques: A NIST Scientific Foundation Review | NIST
Link:https://www.nist.gov/publications/digital-investigation-techniques-nist-scientific-foundation-review
Source snippet
Digital Investigation Techniques: A NIST Scientific Foundation Review | NIST...
8.
Source: reddit.com
Title: Gary Mc Kinnon
Link:https://www.reddit.com/r/ufo/comments/dmjjq5
Source snippet
Gary McKinnon - Scottish hacker claims to have seen UFO files...
9.
Source: justice.gov
Link:https://www.justice.gov/usao-md/pr/justice-department-statements-regarding-indictment-former-national-security-advisor-john
10.
Source: pages.nist.gov
Title: sp800 63
Link:https://pages.nist.gov/800-63-4/sp800-63.html
11.
Source: pages.nist.gov
Title: sp800 63c
Link:https://pages.nist.gov/800-63-4/sp800-63c.html
12.
Source: pages.nist.gov
Title: sp800 63b
Link:https://pages.nist.gov/800-63-4/sp800-63b.html
13.
Source: justice.gov
Link:https://www.justice.gov/archives/opa/pr/national-security-agency-employee-indicted-willful-transmission-and-retention-national
14.
Source: justice.gov
Link:https://www.justice.gov/usao-md/pr/national-security-agency-employee-facing-federal-indictment-willful-transmission-and
15.
Source: justice.gov
Link:https://www.justice.gov/archives/opa/pr/fbi-employee-indicted-illegally-removing-national-security-documents-taking-material-her-home
16.
Source: oig.justice.gov
Title: fbi intelligence analyst indicted and arrested retention national defense
Link:https://oig.justice.gov/news/press-release/fbi-intelligence-analyst-indicted-and-arrested-retention-national-defense
17.
Source: csrc.nist.gov
Link:https://csrc.nist.gov/pubs/sp/800/86/final
18.
Source: justice.gov
Link:https://www.justice.gov/archive/criminal/cybercrime/press-releases/2002/mckinnonIndict2.htm
19.
Source: nvlpubs.nist.gov
Title: SP.800 171r3
Link:https://nvlpubs.nist.gov/nistpubs/SpecialPublications/800-171r3/NIST.SP.800-171r3.html
20.
Source: justice.gov
Title: Manual | 9-5.000
Link:https://www.justice.gov/jm/jm-9-5000-issues-related-trials-and-other-court-proceedings
21.
Source: csrc.nist.rip
Title: ripdigital forensics
Link:https://csrc.nist.rip/glossary/term/digital_forensics
22.
Source: GOV.UK
Title: www.gov.uk UF O files
Link:https://www.gov.uk/government/publications/ufo-files
23.
Source: uapmurders.com
Link:https://uapmurders.com/uaps/Details/Gary_McKinnon/
Additional References
24.
Source: youtube.com
Title: Unmasking Deepfakes & Proving Authenticity: The Tech Behind Video Forensics
Link:https://www.youtube.com/watch?v=13cEYoo5Hgg
Source snippet
This selection pairs direct coverage of Gary McKinnon's computer intrusion case—where unverified claims of UFO files were made—with exper...
25.
Source: ufosearch.org
Title: The full Department of War PURSUE archive — d
Link:https://ufosearch.org/
Source snippet
UFO Search — PURSUE UAP ArchiveMay 8, 2026 — P PRESIDENTIAL UNSEALING & REPORTING SYSTEM FOR UAP ENCOUNTERS▍ RELEASE 01 · CLEARED 2026-05...
Published: May 8, 2026
26.
Source: legalclarity.org
Title: Each entry records the date and tim
Link:https://legalclarity.org/authentication-of-digital-evidence-admissibility-standards/
Source snippet
Authentication of Digital Evidence: Admissibility Standards - LegalClarityMay 15, 2026 — CHAIN OF CUSTODY FOR DIGITAL FILES A chain of cu...
Published: May 15, 2026
27.
Source: youtube.com
Title: Digital Provenance Explained | Track, Verify & Trust Data
Link:https://www.youtube.com/watch?v=ZGM67CdbhPU
Source snippet
Unmasking Deepfakes & Proving Authenticity: The Tech Behind Video Forensics...
28.
Source: youtube.com
Title: Understanding Chain of Custody in Digital Forensics
Link:https://www.youtube.com/watch?v=vimQuaC3RYM
Source snippet
Digital Provenance Explained | Track, Verify & Trust Data...
29.
Source: monkeyandelf.com
Link:https://www.monkeyandelf.com/antigravity-unearthly-officers-and-ufos-the-history-of-the-loudest-pentagon-hacking/
30.
Source: ufohackers.org
Link:https://www.ufohackers.org/hackers
31.
Source: youtube.com
Title: Gary Mc Kinnon wins extradition battle
Link:https://www.youtube.com/watch?v=y4lecD44F5E
Source snippet
Understanding Chain of Custody in Digital Forensics...
32.
Source: youtube.com
Title: Hacking for UFOs and fighting for his life. Who is Gary Mc Kinnon?
Link:https://www.youtube.com/watch?v=OImdnvQx7sQ
Source snippet
Gary McKinnon wins extradition battle...
33.
Source: ufohackers.org
Link:https://www.ufohackers.org/hackers/gary-mckinnon/mckinnon-overview