Within Missing Proof
What the Missing Access Logs Could Have Proved
Host records and timestamps could link the claimed files to a specific machine and session, separating documented access from later recollection.
On this page
- How logs identify hosts and sessions
- What timestamps can corroborate
- Why intrusion evidence does not verify file content
Page outline Jump by section
Introduction
The strongest evidence that could have clarified Gary McKinnon’s most controversial claims is not necessarily the files themselves, but the access logs surrounding the sessions in which he said he viewed them. Public records establish that McKinnon gained unauthorised access to numerous United States military and NASA systems between 2001 and 2002. What they do not publicly establish is that he accessed the specific computers, directories or files later associated with his claims about UFO imagery or a spreadsheet referring to “Non-Terrestrial Officers”.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20…
This distinction matters because access logs can reliably answer questions about where a user connected, when they were connected and what resources they requested. They generally cannot, on their own, prove the meaning or contents of files viewed during a session. In McKinnon’s case, the absence of publicly available logs linking his remembered discoveries to identifiable systems leaves a significant evidential gap between a documented intrusion and later recollections about what was seen.
How logs identify hosts and sessions
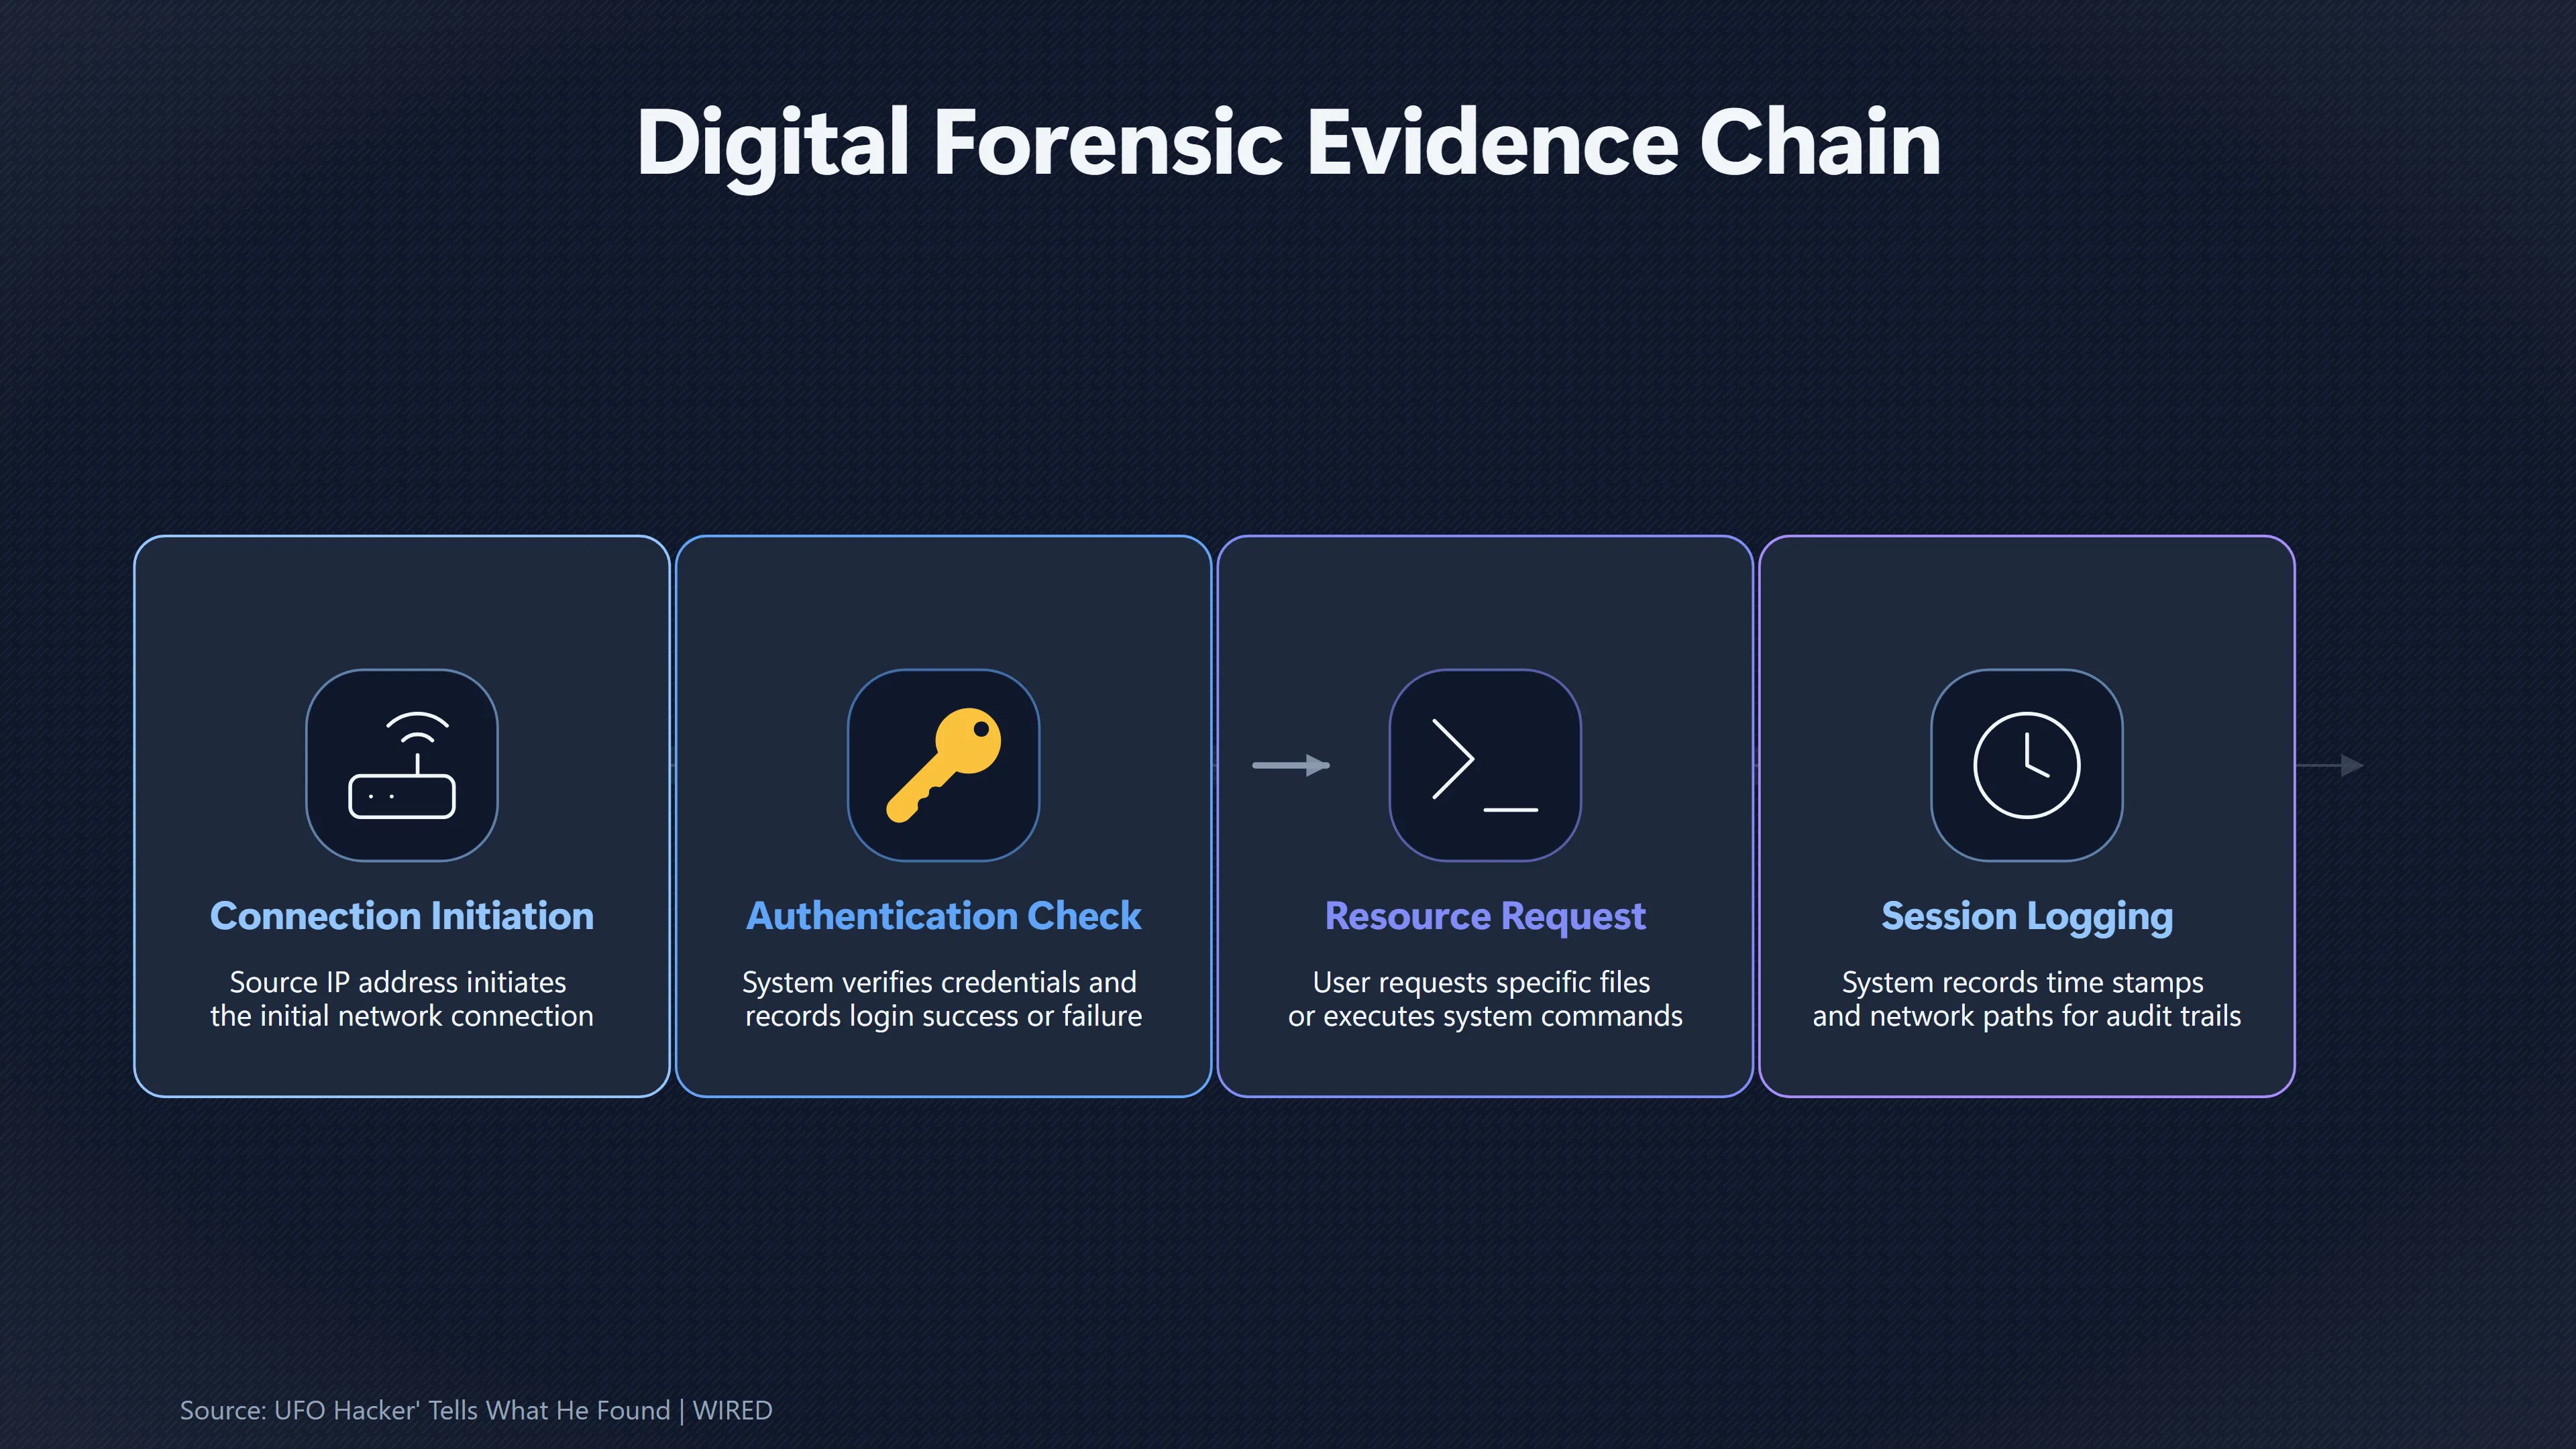
Enterprise computer systems routinely generate multiple kinds of logs during an authenticated or unauthorised session. Although the precise formats differ between operating systems and applications, investigators generally look for records that establish:
- the source IP address initiating the connection
- the destination computer or server
- the account or credentials used
- login and logout times
- authentication successes or failures
- commands executed or files requested
- remote administration tools launched
- network paths followed between systems.
Because the McKinnon investigation involved numerous military and NASA computers across different organisations, such records could have identified the exact machine on which a disputed file allegedly appeared rather than simply demonstrating that he had entered a government network. The Department of Justice’s indictments describe unauthorised access to dozens of military and NASA systems and allege that McKinnon obtained administrator privileges and moved between compromised computers, but they do not publicly identify any access logs showing him opening the particular image or spreadsheet later discussed in interviews.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20…
Had investigators retained and released logs identifying a specific NASA workstation, server or file repository corresponding to McKinnon’s account, independent researchers could have examined that system’s role and the types of material it normally contained.
What timestamps can corroborate
Timestamps are particularly valuable because they allow separate records to be compared.
For example, if logs showed that McKinnon connected to a NASA image server at a particular time, investigators could compare that timestamp with:
- firewall records
- operating system audit logs[nvlpubs.nist.gov]nvlpubs.nist.govReview and analyze system audit records [Assignment: organization-defined frControlled Unclassified Information in Nonfederal Systems and OrganizationsREFERENCES Source Control: AU-05 Supporting Publications: None…
- file access times
- administrator activity
- backup schedules
- network monitoring records
- McKinnon’s own computer records, if available.
When several independent systems record the same sequence of events, confidence increases that the reconstructed timeline is accurate. This is a standard principle in digital forensics, where investigators seek repeatable evidence supported by multiple sources rather than relying on a single record. Guidance from the U.S. National Institute of Standards and Technology (NIST) emphasises preserving evidence in a way that documents origin, integrity and handling so events can later be reconstructed and verified.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20…
In McKinnon’s case, publicly available legal records establish the period during which the intrusions occurred, but no released timeline ties his reported viewing of an unusual satellite image or spreadsheet to a documented file access event on a named host.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20…
Why intrusion evidence does not verify file content
A common misunderstanding is that proving someone entered a computer automatically proves everything they later claimed to have seen there.
Digital evidence does not work that way.
Access logs can demonstrate that a person reached a particular computer or directory, but they normally cannot answer questions such as:
- whether a displayed image represented operational data, a simulation or test material
- whether a spreadsheet reflected genuine personnel records, fictional content or a training exercise
- whether a filename accurately described its contents
- whether a file was opened completely or only partially before a connection ended.
McKinnon himself has consistently said that his slow dial-up connection prevented him from downloading the high-resolution image and that the remote session ended before he could preserve it. That explanation is consistent with why no original image has been produced, but it also means later analysis cannot compare his memory with the original digital artefact.[WIRED]wired.comUFO Hacker' Tells What He Found | WIREDWIRED'UFO Hacker' Tells What He Found | WIRED…
Consequently, even perfect authentication logs would establish only that he reached a particular resource at a particular time. They would not independently verify his interpretation of what appeared on screen.
The additional complication of missing or deleted logs
Another limitation is that access logs are not permanent by default.
Large organisations typically rotate logs because of storage limits, retention policies and operational requirements. Some logs are overwritten automatically after weeks or months. Others may survive only if copied into an incident investigation.
The McKinnon indictments also allege that, during some intrusions, system log files were deleted after remote administration software was installed. Whether every affected organisation retained separate forensic copies has not been publicly documented, and no released investigative material includes the detailed session logs that would allow outside researchers to reconstruct the disputed viewing sessions.[Department of Justice]justice.govDepartment of JusticeBritish National Charged with Hacking Into N.J. Naval Weapons Station Computers, Disabling Network After Sept. 11 (N…
Even if some original logs survived within investigative files, they have not entered the public record in a form that permits independent examination.
What the missing logs could have proved—and what they never could
If detailed access logs for the relevant sessions were publicly available, they could potentially answer several important questions:
- Which host was accessed? Identifying the precise computer or server would narrow the search to a specific project or organisational unit.
- When did the session occur? Precise timestamps could be matched with other network and forensic records.
- Which directories were opened? File paths might distinguish operational repositories from testing, graphics or training environments.
- How long did the session last? Session duration could help evaluate McKinnon’s account of interrupted downloads over a slow connection.
- Which files were requested? File names or access records could establish whether the claimed documents existed on that system.
Equally important are the questions that logs alone could not answer. They could not prove that an image depicted an extraterrestrial craft, that a spreadsheet accurately described secret personnel, or that McKinnon’s interpretation was correct. Those conclusions would still require the original files, metadata, surrounding directories and corroborating documentation.
For that reason, the missing access logs occupy a crucial middle ground in the evidence. They could have strengthened or weakened McKinnon’s account by linking it to specific systems and documented sessions, but they would not by themselves transform remembered observations into verified proof of the extraordinary claims that followed.
Amazon book picks
Further Reading
Books and field guides related to What the Missing Access Logs Could Have Proved. Use these as the next step if you want deeper reading beyond the article.
The Demon-Haunted World
Rating: 4.5/5 from 43 Google Books ratings
NEW YORK TIMES BESTSELLER • From the renowned astronomer and author of Cosmos comes a “powerful [and] stirring defense of informed ration...
The Practice of Network Security Monitoring
Network security is not simply about building impenetrable walls—determined attackers will eventually overcome traditional defenses. The...
Network Forensics
“This is a must-have work for anybody in information security, digital forensics, or involved with incident handling. As we move away fro...
Digital Evidence and Computer Crime
Digital Evidence and Computer Crime, Second Edition, is a hands-on resource that aims to educate students and professionals in the law en...
eBay marketplace picks
Marketplace Samples
Live-tested eBay searches with available results related to this page.
Selected fromserver room wall art oneBay.co.uk.
Endnotes
1.
Source: justice.gov
Link:https://www.justice.gov/archive/criminal/cybercrime/press-releases/2002/mckinnonIndict.htm
Source snippet
Department of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20...
2.
Source: wired.com
Title: ‘UFO Hacker’ Tells What He Found | WIRED
Link:https://www.wired.com/2006/06/ufo-hacker-tells-what-he-found/
Source snippet
WIRED'UFO Hacker' Tells What He Found | WIRED...
3.
Source: justice.gov
Link:https://www.justice.gov/archive/criminal/cybercrime/press-releases/2002/mckinnonIndict2.htm
Source snippet
Department of JusticeBritish National Charged with Hacking Into N.J. Naval Weapons Station Computers, Disabling Network After Sept. 11 (N...
4.
Source: nasa.gov
Title: Headquarters FOIA Library
Link:https://www.nasa.gov/foia/nasa-e-libraries/headquarters-foia-library/
Source snippet
January 22, 2026 — FOIA * FOIA Home * FOIA Contacts * FOIA Guidance * Access NASA Records * NASA FOIA Reports * FOIA E-Libraries * Su...
Published: January 22, 2026
5.
Source: justice.gov
Title: National Security Division | NSD Electronic Reading Room
Link:https://www.justice.gov/nsd/nsd-electronic-reading-room
Source snippet
March 10, 2023 — NSD ELECTRONIC READING ROOM * The Hanssen Case * Statement of Facts (PDF) * Indictment (PDF) * Plea Agreement (PDF) * Pa...
Published: March 10, 2023
6.
Source: nist.gov
Title: Lyle, Barbara Guttman, John Butler, Kelly Sauerwein, Christina Reed, Corrine L
Link:https://www.nist.gov/publications/digital-investigation-techniques-nist-scientific-foundation-review
Source snippet
Digital Investigation Techniques: A NIST Scientific Foundation Review | NISTNovember 21, 2022 — DIGITAL INVESTIGATION TECHNIQUES: A NIST...
Published: November 21, 2022
7.
Source: nist.gov
Title: White, Shannan Williams, Tracy Walraven
Link:https://www.nist.gov/publications/digital-evidence-preservation-considerations-evidence-handlers
Source snippet
Digital Evidence Preservation: Considerations for Evidence Handlers | NISTSeptember 8, 2022 — DIGITAL EVIDENCE PRESERVATION: CONSIDERATIO...
Published: September 8, 2022
8.
Source: nist.gov
Title: Laamanen, Craig S. Russell, Lawrence D. Nadel AB
Link:https://www.nist.gov/publications/assessment-closed-circuit-television-digital-video-recording-and-export-technologies
Source snippet
Assessment of Closed Circuit Television Digital Video Recording and Export Technologies | NISTMarch 6, 2017 — ASSESSMENT OF CLOSED CIRCUI...
Published: March 6, 2017
9.
Source: justice.gov
Title: Manual | 9-13.000
Link:https://www.justice.gov/jm/jm-9-13000-obtaining-evidence
Source snippet
Justice Manual | 9-13.000 - Obtaining Evidence | United States Department of JusticeJustice Manual Title 9: Criminal 9-13.000 - OBTAINING...
10.
Source: nvlpubs.nist.gov
Title: Review and analyze system audit records [Assignment: organization-defined fr
Link:https://nvlpubs.nist.gov/nistpubs/SpecialPublications/800-171r3/NIST.SP.800-171r3.html
Source snippet
Controlled Unclassified Information in Nonfederal Systems and OrganizationsREFERENCES Source Control: AU-05 Supporting Publications: None...
11.
Source: GOV.UK
Title: From: Ministry of Justic
Link:https://www.gov.uk/government/publications/access-to-digital-evidence-a2de
Source snippet
to Digital Evidence (A2DE) - GOV.UKDecember 21, 2018 — Guidance ACCESS TO DIGITAL EVIDENCE (A2DE) This Policy Framework explains the proc...
Published: December 21, 2018
Additional References
12.
Source: en.wikisource.org
Title: US v Gary Mc Kinnon Indictment
Link:https://en.wikisource.org/wiki/US_v_Gary_McKinnon_Indictment
Source snippet
v Gary McKinnon Indictment - Wikisource, the free online libraryUS V GARY MCKINNON INDICTMENT Download IN THE UNITED STATES DISTRICT COUR...
13.
Source: youtube.com
Title: Gary Mc Kinnon interviewed by Richard Dolan
Link:https://www.youtube.com/watch?v=IhUC80M8X1s
Source snippet
Hacking for UFOs and fighting for his life. Who is Gary McKinnon?...
14.
Source: youtube.com
Title: The Man Who Hacked the U.S. Government
Link:https://www.youtube.com/watch?v=ND0zQX1rGdg
Source snippet
Ancient Aliens: Hacking NASA Secrets (Season 12, Episode 9)...
15.
Source: youtube.com
Title: Hacking for UFOs and fighting for his life. Who is Gary Mc Kinnon?
Link:https://www.youtube.com/watch?v=OImdnvQx7sQ
Source snippet
The Man Who Hacked the U.S. Government...
16.
Source: youtube.com
Title: Ancient Aliens: Hacking NASA Secrets (Season 12, Episode 9)
Link:https://www.youtube.com/watch?v=20rWFDfh68Y
Source snippet
Gary McKinnon wins extradition battle...
17.
Source: youtube.com
Title: UK blocks hacker extradition to U.S
Link:https://www.youtube.com/watch?v=xudYoyi_JSY
Source snippet
Gary McKinnon: No hacking charges in UK...
18.
Source: youtube.com
Title: Gary Mc Kinnon wins extradition battle
Link:https://www.youtube.com/watch?v=y4lecD44F5E
Source snippet
UK hacker's extradition to US blocked...
19.
Source: youtube.com
Title: UK hacker’s extradition to US blocked
Link:https://www.youtube.com/watch?v=v4Js8DF80HY
Source snippet
UK blocks hacker extradition to U.S...
20.
Source: youtube.com
Title: Gary Mc Kinnon: No hacking charges in UK
Link:https://www.youtube.com/watch?v=xAhzZRa2aws