Within Mc Kinnon Case
Mckinnon Entry Metho
Gary McKinnon's unauthorised access to NASA and US military computers between 2001 and 2002 was notable not because it relied on advanced hacking techniques, but because it exploited surprisingly weak security practices.
Page outline Jump by section
Introduction
Gary McKinnon’s unauthorised access to NASA and US military computers between 2001 and 2002 was notable not because it relied on advanced hacking techniques, but because it exploited surprisingly weak security practices. McKinnon consistently said that many internet-connected Windows systems were protected by blank or trivial administrator passwords, allowing him to gain administrative access using simple scanning tools rather than sophisticated exploits. Prosecutors agreed that he obtained administrator privileges across numerous systems, although they characterised his subsequent actions far more seriously than McKinnon did.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20…
The case has since become a widely cited example of how basic security failures can expose even large government organisations. While later public discussion often focused on McKinnon’s UFO claims, the mechanics of his entry into military networks revealed shortcomings in password management, network trust relationships and remote administration practices that security professionals considered avoidable.[The Guardian]theguardian.comOpen source on theguardian.com.
The blank-password weakness
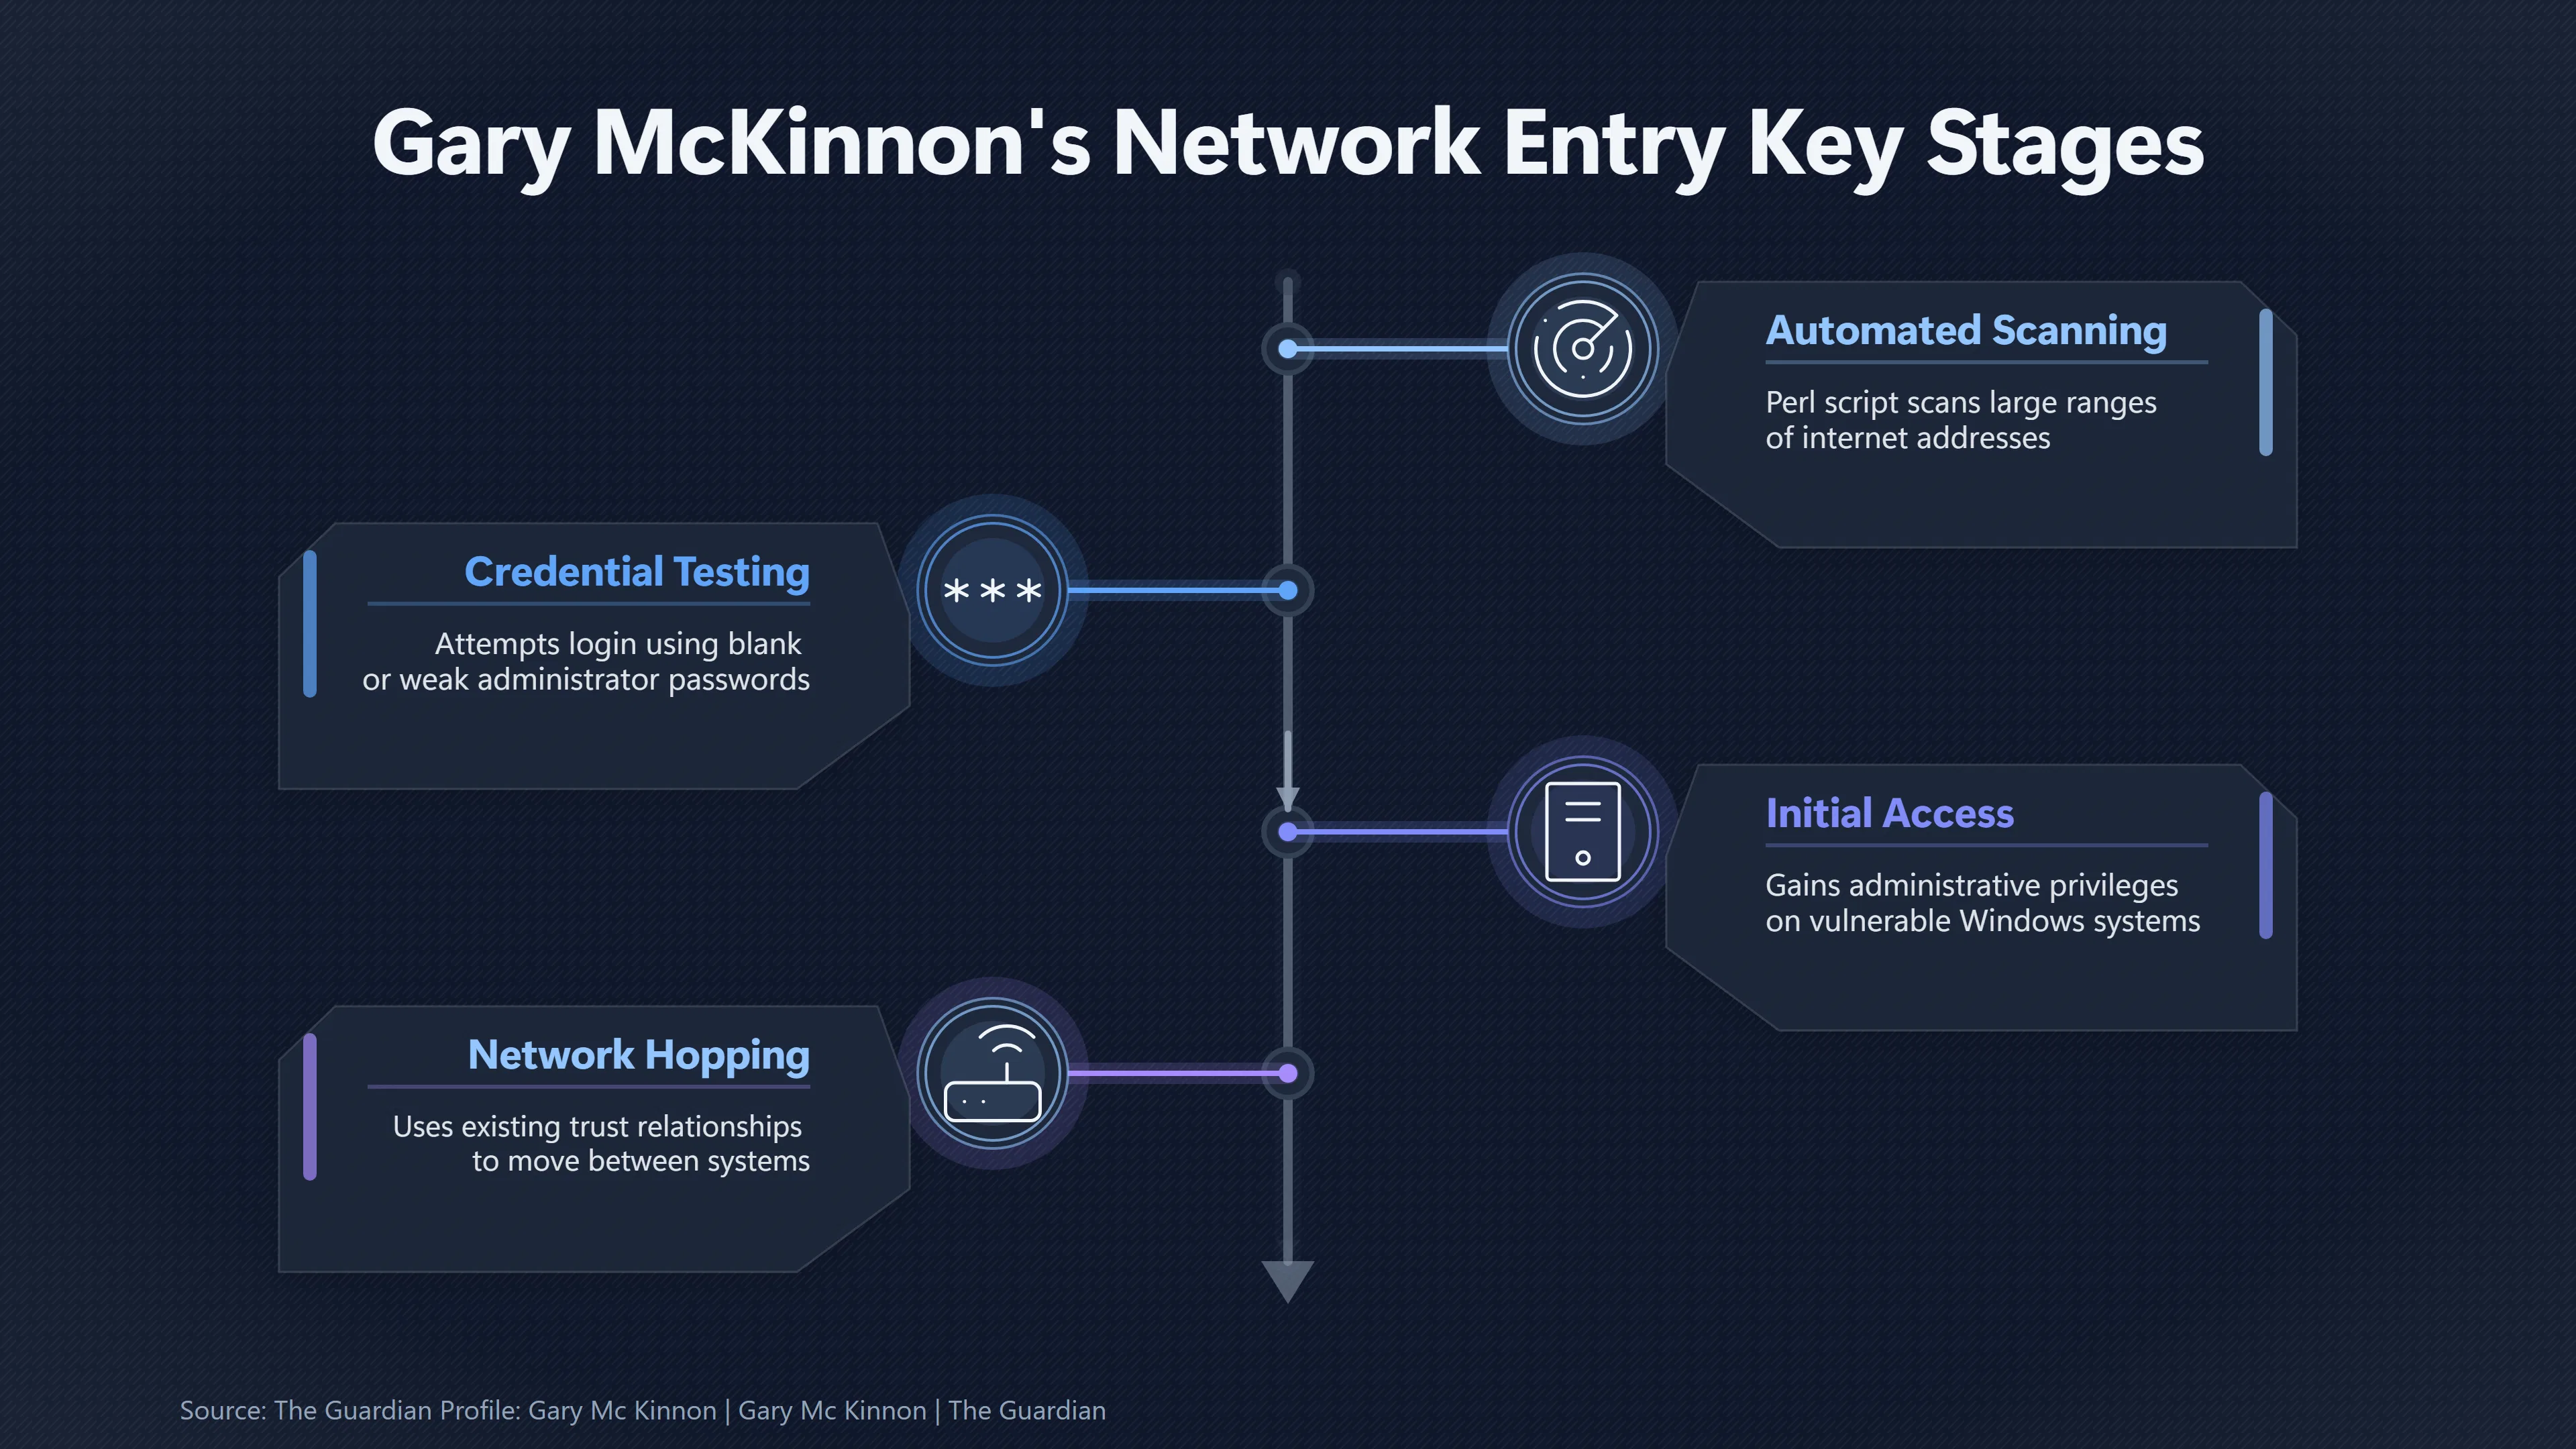
The central feature of McKinnon’s account was remarkably simple: he searched for Windows computers where administrator accounts had no password at all or retained extremely weak default credentials. According to his interviews, he wrote a Perl script that scanned large ranges of internet addresses looking for Windows systems exposing remote administration services. When the script identified a machine, he attempted to log in using administrator accounts with blank passwords.
McKinnon later claimed that this process uncovered large numbers of vulnerable computers across NASA and the US military. In one interview he said he could scan around 65,000 computers in under ten minutes using automated tools, making the discovery of poorly secured systems largely a matter of scale rather than technical brilliance.[The Guardian]theguardian.comThe Guardian Profile: Gary Mc Kinnon | Gary Mc Kinnon | The GuardianThe GuardianProfile: Gary McKinnon | Gary McKinnon | The GuardianJuly 31, 2009…
The US indictment broadly matched this description. Rather than alleging that McKinnon defeated advanced encryption or exploited previously unknown software flaws, prosecutors stated that he scanned military networks, gained administrator privileges and then installed remote administration software and other utilities after obtaining access.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20…
Scanning and trusted connections
Finding one vulnerable computer was only the first step. According to McKinnon, he deliberately targeted computers connected to support and logistics departments because they were often less well protected than more sensitive systems.
Once logged into an authorised machine, he examined how that computer communicated with other systems on the same network. Organisations commonly configure computers to trust authenticated users or administrators from related systems so that staff can move between network resources without repeated logins. McKinnon said he used these existing trust relationships to move gradually from less sensitive computers towards systems that appeared more interesting.
He described this progression as “hopping” through trusted connections rather than breaking into each computer individually. Public reporting indicates that he inspected network connections and administrative relationships already available to authorised users rather than repeatedly exploiting new vulnerabilities.[The Guardian]theguardian.comThe Guardian Game over | Gary Mc Kinnon | The GuardianThe Guardian Game over | Gary Mc Kinnon | The Guardian
This distinction is important. His public description does not suggest that he bypassed every security control independently. Instead, once one administrator account had been compromised, existing network design often allowed movement to additional systems that trusted that account or machine.
Why administrator access mattered
Administrator privileges provide extensive control over a Windows computer. An administrator can normally:
- View and copy files.
- Create or delete user accounts.
- Install or remove software.
- Change system settings.
- Access password databases and configuration files.
- Connect remotely to other authorised systems.
US prosecutors alleged that after obtaining administrator privileges McKinnon installed remote administration software, copied password files and other data, deleted user accounts and removed critical operating-system files on some systems. Those allegations formed a major part of the criminal case against him and went well beyond the initial method of entry. McKinnon admitted accessing computers without permission but disputed allegations about the extent of intentional damage.[justice.gov]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20…
Why these systems were vulnerable
The McKinnon case highlighted several basic security weaknesses occurring together rather than one catastrophic technical flaw.
The reported weaknesses included:
- Blank administrator passwords. Some administrator accounts allegedly had no password configured, making remote login straightforward.
- Internet exposure. Vulnerable computers were reachable from the public internet instead of being isolated behind stronger access controls.
- Weak password management. Contemporary reporting also referred to default or easily guessed passwords remaining in use on some systems.
- Broad administrative trust. Once authenticated on one machine, existing trust relationships sometimes allowed movement to additional systems.
- Remote administration tools. Legitimate management software could be used after authentication to control computers remotely.[theguardian.com]theguardian.comOpen source on theguardian.com.
None of these weaknesses was individually unique. What made the case unusual was that multiple weaknesses reportedly existed across numerous defence-related networks.

What the breach revealed about security
Security specialists have often cited the McKinnon case as evidence that poor operational security can be more dangerous than a lack of sophisticated defensive technology. The incident suggested that organisations responsible for sensitive but unclassified government systems had not consistently enforced basic practices such as mandatory passwords, least-privilege administration and network segmentation.
It is also important to distinguish between the affected systems and highly classified military networks. Contemporary reporting indicated that McKinnon primarily accessed unclassified administrative systems connected to the public internet, not isolated classified networks designed to handle top-secret information. That did not make the compromised systems unimportant, since logistics, communications and administrative infrastructure can still be operationally significant.[The Guardian]theguardian.comOpen source on theguardian.com.
The broader lesson was not that military networks were universally insecure, but that even a relatively small number of poorly managed systems could provide an entry point into larger government environments.
A case study in basic cyber hygiene
From a technical perspective, McKinnon’s own description of his methods has remained remarkably consistent over the years: automate the search for internet-connected Windows computers, identify administrator accounts protected by blank or weak passwords, log in legitimately using those credentials, and then explore trusted network relationships from inside.
Whether or not every detail of his recollections is complete, this overall mechanism aligns closely with the core allegations in the US indictment. The enduring significance of the case is therefore less about an ingenious hacking breakthrough than about how elementary security oversights—particularly poor password management and excessive trust between systems—enabled unauthorised access to dozens of government computers.[justice.gov]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20…
Amazon book picks
Further Reading
Books and field guides related to Mckinnon Entry Metho. Use these as the next step if you want deeper reading beyond the article.
The Cuckoo's Egg
This is the true story of how a systems manager at Lawrence Berkeley Lab singlehandedly tracked down and helped capture a computer hacker...
Ghost in the Wires
In this "intriguing, insightful and extremely educational" novel, the world's most famous hacker teaches you easy cloaking and counter-me...
Hacking: The Art of Exploitation
Hacking is the art of creative problem solving, whether that means finding an unconventional solution to a difficult problem or exploitin...
The Tangled Web
Modern web applications are built on a tangle of technologies that have been developed over time and then haphazardly pieced together. Ev...
eBay marketplace picks
Marketplace Samples
Live-tested eBay searches with available results related to this page.
Selected fromcomputer circuit art oneBay.co.uk.
Endnotes
1.
Source: justice.gov
Link:https://www.justice.gov/archive/criminal/cybercrime/press-releases/2002/mckinnonIndict.htm
Source snippet
Department of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20...
2.
Source: theguardian.com
Link:https://www.theguardian.com/uk/2007/apr/03/politics.usa
3.
Source: theguardian.com
Link:https://www.theguardian.com/technology/blog/2008/aug/01/nasahackerexploitsknownmed
4.
Source: theguardian.com
Title: The Guardian Profile: Gary Mc Kinnon | Gary Mc Kinnon | The Guardian
Link:https://www.theguardian.com/technology/2009/jul/31/gary-mckinnon-hacking-extradition
Source snippet
The GuardianProfile: Gary McKinnon | Gary McKinnon | The GuardianJuly 31, 2009...
Published: July 31, 2009
5.
Source: theguardian.com
Title: The Guardian Game over | Gary Mc Kinnon | The Guardian
Link:https://www.theguardian.com/theguardian/2005/jul/09/weekend7.weekend2
6.
Source: media.defense.gov
Title: U.S. Department of War U.S. Department of Justice
Link:https://media.defense.gov/2002/Nov/12/2001711901/-1/-1/1/McKinnon_comphacker.pdf
7.
Source: theguardian.com
Link:https://www.theguardian.com/technology/2005/jun/11/hacking.internetcrime
Additional References
8.
Source: gao.gov
Link:https://www.gao.gov/products/gao
Source snippet
August 22, 2019 — DOD INSTALLATIONS: MONITORING USE OF PHYSICAL ACCESS CONTROL SYSTEMS COULD REDUCE RISKS TO PERSONNEL AND ASSETS GAO...
Published: August 22, 2019
9.
Source: seclists.org
Title: Information Security News: UK’s NASA hacker breaks his silence
Link:https://seclists.org/isn/2005/Jul/42
Source snippet
July 11, 2005 — UK'S NASA HACKER BREAKS HIS SILENCE * * * From: InfoSec News <isn c4i org> Date: Tue, 12 Jul 2005 05:12:13 -0500 (CDT)...
Published: July 11, 2005
10.
Source: youtube.com
Title: Gary Mc Kinnon interviewed by Richard Dolan
Link:https://www.youtube.com/watch?v=IhUC80M8X1s
Source snippet
These videos cover Gary McKinnon's computer intrusion into U.S. military and NASA systems, detailing how he exploited default remote acce...
11.
Source: youtube.com
Title: Ancient Aliens: Hacking NASA Secrets (Season 12, Episode 9) | History
Link:https://www.youtube.com/watch?v=20rWFDfh68Y
Source snippet
Gary McKinnon interviewed by Richard Dolan...
12.
Source: youtube.com
Title: THE ONE WHO HACKED NASA [MC KINNON]
Link:https://www.youtube.com/watch?v=-4ciqkHNFPE
Source snippet
Ancient Aliens: Hacking NASA Secrets (Season 12, Episode 9) | History...
13.
Source: youtube.com
Title: The Man Who Hacked the U.S. Government
Link:https://www.youtube.com/watch?v=ND0zQX1rGdg
Source snippet
UK hacker to learn extradition fate...
14.
Source: wired.com
Title: Dot-Mil Hacker’s Download Mistake | WIRED
Link:https://www.wired.com/2002/11/dot-mil-hackers-download-mistake/
15.
Source: wired.com
Title: Brit Accused of Hacking Pentagon | WIRED
Link:https://www.wired.com/2002/11/brit-accused-of-hacking-pentagon/
16.
Source: youtube.com
Title: UK hacker to learn extradition fate
Link:https://www.youtube.com/watch?v=LEvGU1b4ysw
Source snippet
THE ONE WHO HACKED NASA [MC KINNON]...
17.
Source: wired.com
Title: brit fights hacking extradition
Link:https://www.wired.com/2002/11/brit-fights-hacking-extradition/