Within Access Methods
Why Government Defenses Reacted So Slowly
Warnings, incident reports and searches for installed tools moved slowly enough that suspicious activity continued for months before access was fully stopped.
On this page
- When suspicious activity was first noticed
- Why warnings were not shared quickly enough
- What federal reviews said about incident coordination
Page outline Jump by section
Introduction
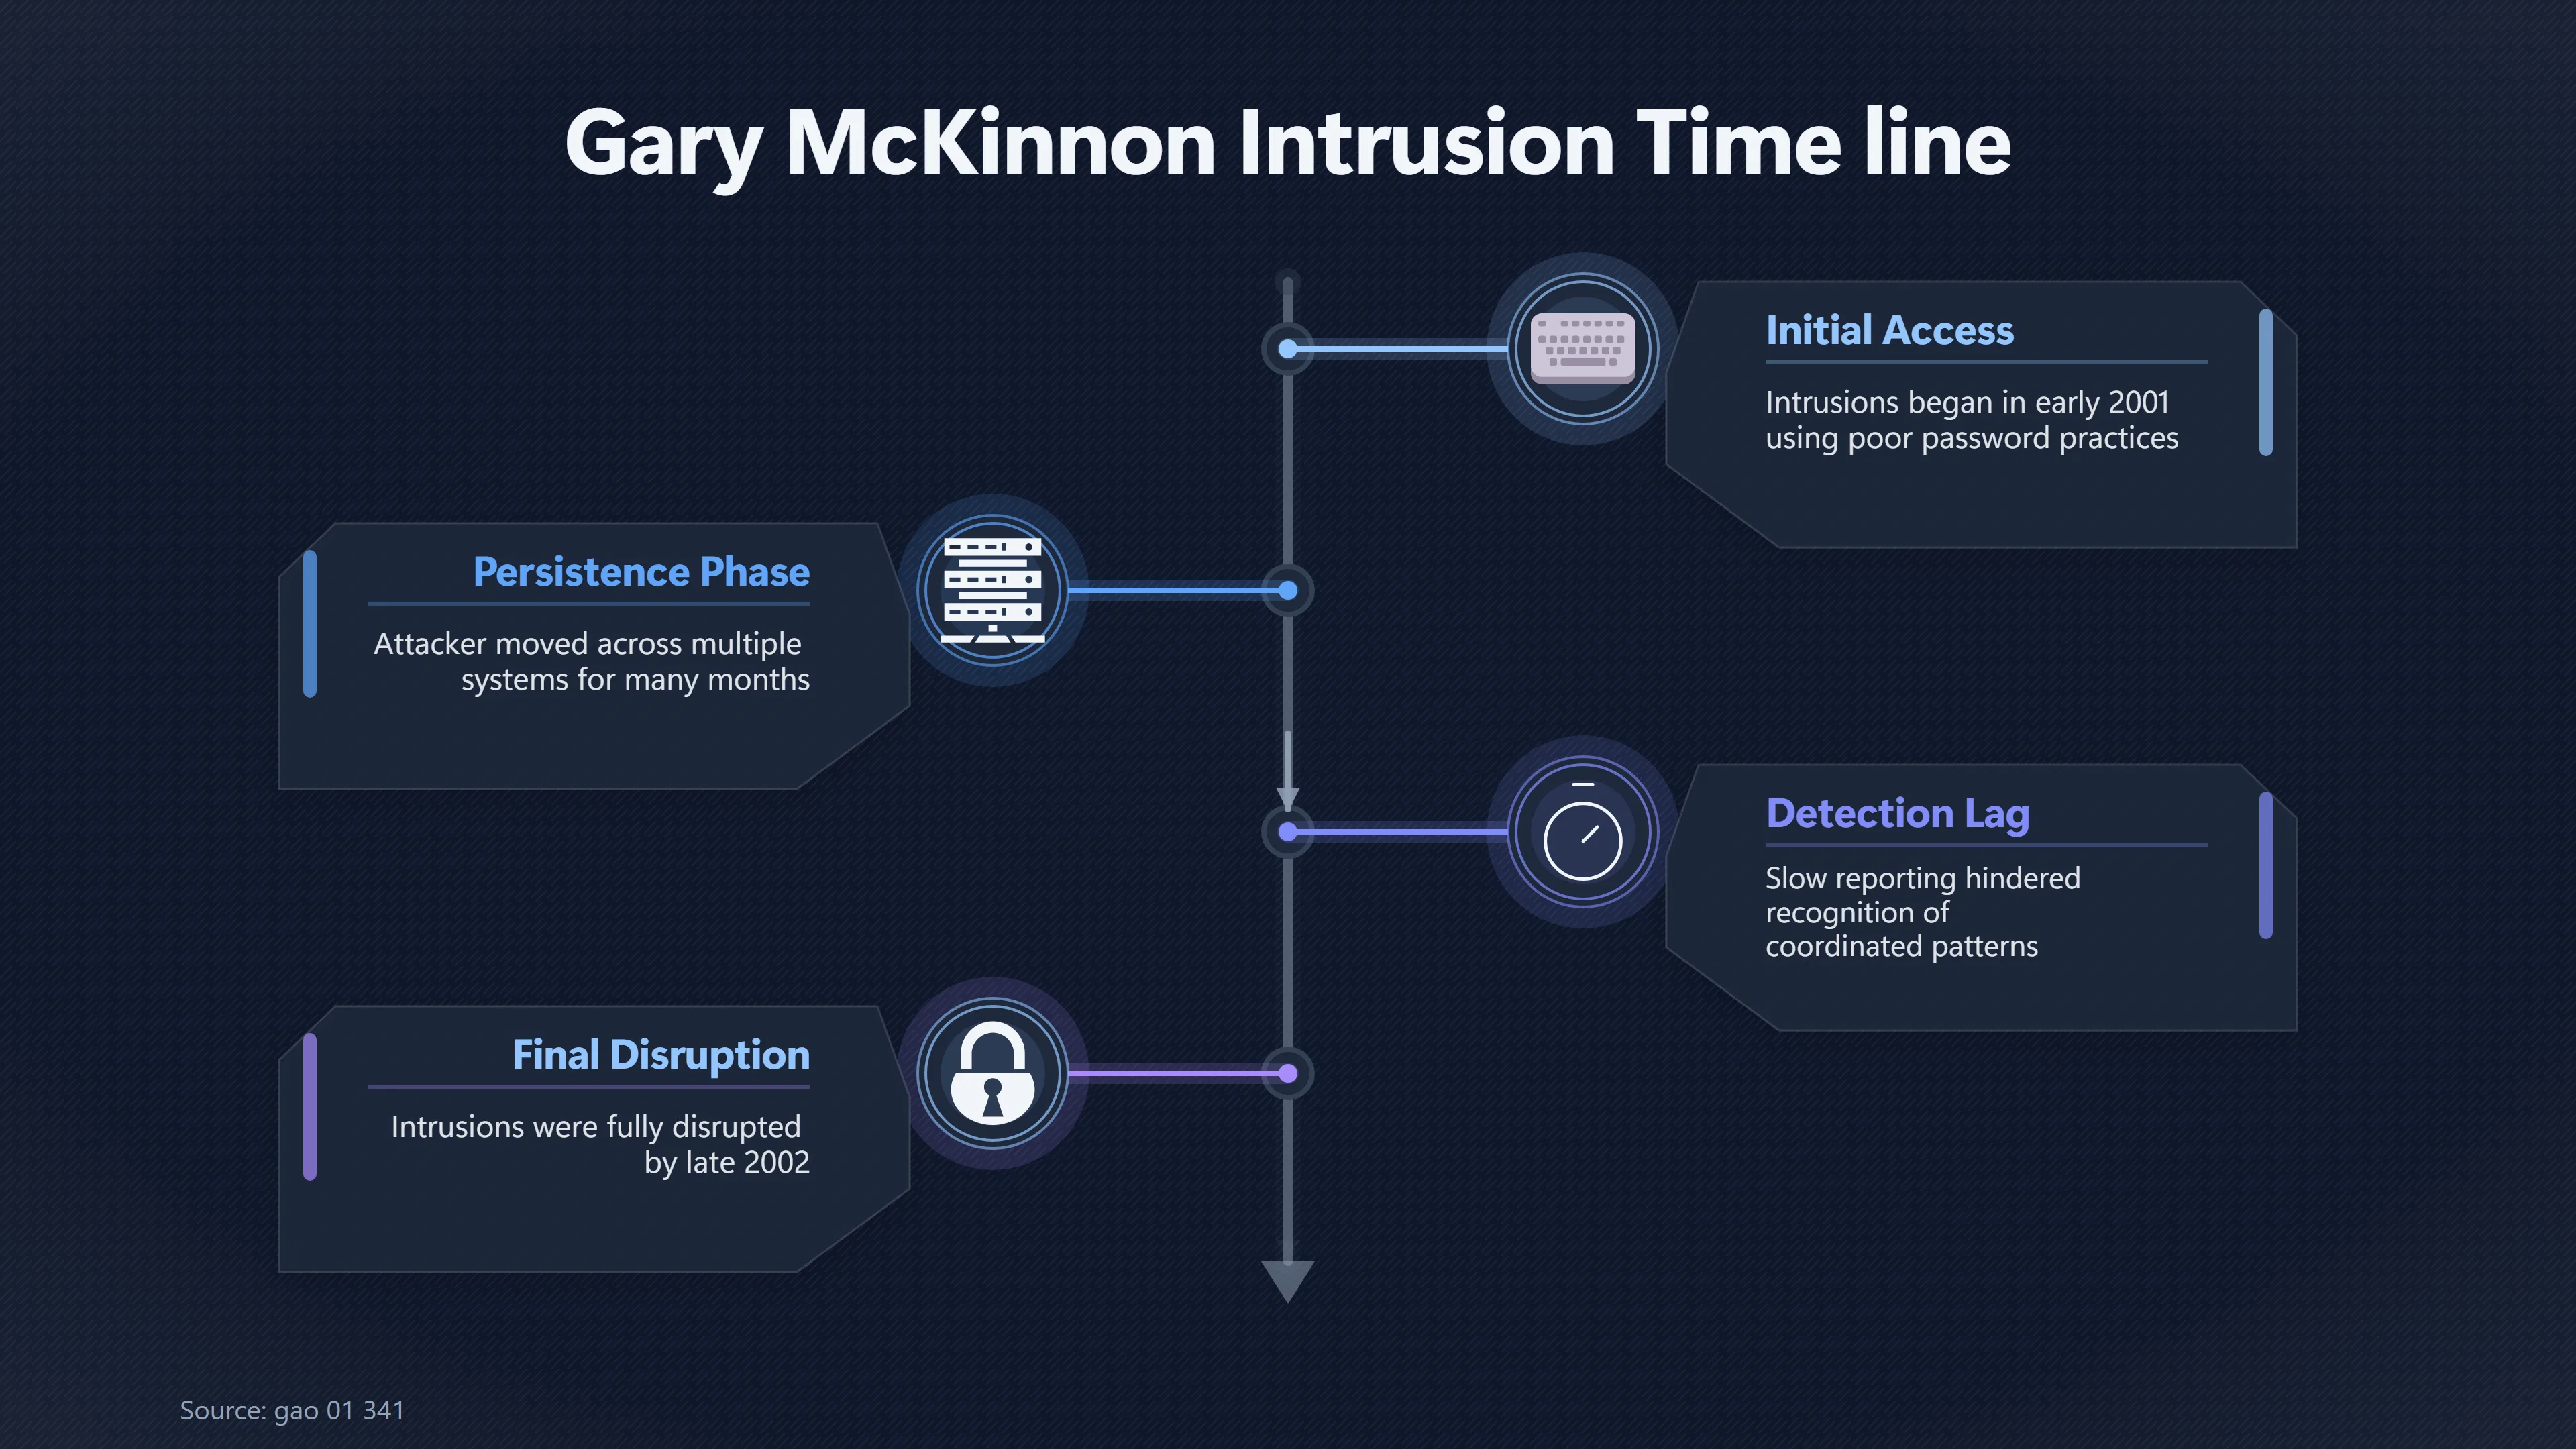
Gary McKinnon’s intrusions persisted for many months not because he used unusually advanced techniques, but because the organisations he targeted were slow to detect suspicious activity, slow to circulate warnings and inconsistent in coordinating their response. The same weaknesses that allowed initial access—poor password practices, exposed administrative services and inconsistent security management—also hindered the government’s ability to recognise that the same attacker was moving across multiple systems. Later official reviews did not treat the case as an isolated failure. Instead, they reflected broader concerns that the US Department of Defense (DoD) lacked integrated monitoring, timely reporting and effective coordination between incident response teams.[GAO]gao.govgaoInformation Security: Challenges to Improving DOD's Incident Response Capabilities | U.S. GAOMarch 29, 2001…
When suspicious activity was first noticed
The public record does not provide a complete day-by-day timeline showing exactly when every affected organisation first detected McKinnon’s activity. However, prosecutors alleged that the intrusions stretched from early 2001 into 2002 before they were fully disrupted, while the subsequent criminal investigation itself lasted around 17 months and involved numerous military and civilian agencies.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20…
Several factors made early detection difficult:
- Many compromised computers were administered locally rather than through a single, central monitoring system.
- Logging and intrusion detection capabilities varied widely between military organisations.
- Administrative access obtained through legitimate accounts could appear less suspicious than attacks exploiting obvious software vulnerabilities.
- Once inside one network, McKinnon allegedly used compromised systems to identify additional targets, meaning each successful intrusion became a platform for discovering others.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20…
Rather than encountering an organisation with a unified operational picture, investigators were dealing with many separate networks that often recognised only fragments of the overall pattern.
Why warnings were not shared quickly enough
Government reviews conducted around the same period show that delayed information sharing was a recognised structural weakness across the Department of Defense.
In March 2001—before McKinnon’s alleged activity had concluded—the US Government Accountability Office (GAO) reported that DoD faced significant challenges integrating information from intrusion detection systems, coordinating incident response between different organisations and ensuring compliance with vulnerability warnings. The review also found weaknesses in department-wide processes for identifying security problems and measuring the effectiveness of incident response.[GAO]gao.govgaoInformation Security: Challenges to Improving DOD's Incident Response Capabilities | U.S. GAOMarch 29, 2001…
These shortcomings mattered because a distributed attacker could appear to each installation as a local problem rather than part of a wider campaign. Without rapid sharing of indicators such as source addresses, attack methods or compromised accounts, different organisations risked investigating the same intruder independently instead of recognising a coordinated pattern.
The GAO also noted that improving incident response required:
- better integration of monitoring data from multiple sensors;
- more consistent reporting of security incidents;
- stronger coordination between component-level response teams;
- regular reviews to identify recurring vulnerabilities across the department.[GAO]gao.govgaoInformation Security: Challenges to Improving DOD's Incident Response Capabilities | U.S. GAOMarch 29, 2001…
Those recommendations closely matched weaknesses exposed during the period of McKinnon’s intrusions.

What federal reviews said about incident coordination
The McKinnon case occurred during a period when federal auditors repeatedly warned that cyber defence coordination lagged behind the growing threat.
A 1996 GAO report had already recommended mandatory reporting of computer security incidents across DoD, routine vulnerability assessments and faster correction of identified weaknesses. The report argued that fragmented reporting prevented senior leaders from understanding the scale of attacks affecting military systems.[GAO]gao.govInformation Security: Computer Attacks at Department of Defense Pose Increasing Risks | U.S. GAO…
By 2001, GAO concluded that progress remained incomplete. Although DoD had established computer emergency response teams and the Joint Task Force–Computer Network Defense to improve coordination, important gaps remained in integrating detection systems, sharing alerts and coordinating responses between military components.[GAO]gao.govgaoInformation Security: Challenges to Improving DOD's Incident Response Capabilities | U.S. GAOMarch 29, 2001…
NASA’s Office of Inspector General also identified broader institutional problems affecting incident response. Testimony to Congress described inconsistent interpretation of IT security guidance across NASA centres and called for improved performance measures covering vulnerability scanning, security monitoring and incident response. It also noted that correlating NASA intrusion data with DoD information helped investigators connect attacks that affected both organisations, illustrating the importance of cross-agency information sharing.[NASA Office of Inspector General]oig.nasa.govOffice of Inspector General Cyber Security: The Status of InformationNASA Office of Inspector GeneralCyber Security: The Status of InformationJune 13, 2025…
How delayed detection prolonged the intrusions
Slow detection had practical consequences beyond simply allowing unauthorised access to continue.
According to the indictment and Department of Justice statements, once administrative access had been obtained McKinnon allegedly installed remote administration software, copied password files, created opportunities for continued access and used compromised machines to locate additional victims. Prosecutors also alleged that some systems suffered deleted user accounts, deleted operating system files and operational disruption before access was finally stopped.[Department of Justice]justice.govDepartment of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20…
Because response was not immediate across every affected organisation, investigators were forced to identify, analyse and remediate compromises on numerous separate networks. Each delay increased the opportunity for lateral movement into additional systems or for compromised credentials to remain useful elsewhere.
Lasting lessons from the case
Although the McKinnon prosecution became widely known because of his claims about searching for UFO-related material, cybersecurity specialists have continued to cite the case primarily as an illustration of organisational rather than technical failure.
The official reviews surrounding the same period consistently emphasised that effective defence required more than stronger passwords. Rapid detection depended on combining technical monitoring with prompt reporting, shared situational awareness and coordinated incident response across agencies. Later GAO assessments have continued to identify accurate incident reporting and effective information sharing as essential elements of DoD cyber defence, suggesting that these governance challenges remained important long after the McKinnon investigation concluded.[GAO]gao.govgao 23 105084DOD Cybersecurity: Enhanced Attention Needed to Ensure Cyber Incidents Are Appropriately Reported and Shared | U.S. GAONovember 14, 2022…
Amazon book picks
Further Reading
Books and field guides related to Why Government Defenses Reacted So Slowly. Use these as the next step if you want deeper reading beyond the article.
The Practice of Network Security Monitoring
Network security is not simply about building impenetrable walls—determined attackers will eventually overcome traditional defenses. The...
Applied Incident Response
Incident response is critical for the active defense of any network, and incident responders need up-to-date, immediately applicable tech...
The Cuckoo's Egg
This is the true story of how a systems manager at Lawrence Berkeley Lab singlehandedly tracked down and helped capture a computer hacker...
Incident Response & Computer Forensics
The definitive guide to incident response--updated for the first time in a decade! Thoroughly revised to cover the latest and most effect...
eBay marketplace picks
Marketplace Samples
Live-tested eBay searches with available results related to this page.
Selected fromhacker t shirt oneBay.co.uk.
Endnotes
1.
Source: gao.gov
Title: gao 01 341
Link:https://www.gao.gov/products/gao
Source snippet
Information Security: Challenges to Improving DOD's Incident Response Capabilities | U.S. GAOMarch 29, 2001...
Published: March 29, 2001
2.
Source: gao.gov
Link:https://www.gao.gov/products/aimd
Source snippet
Information Security: Computer Attacks at Department of Defense Pose Increasing Risks | U.S. GAO...
3.
Source: justice.gov
Link:https://www.justice.gov/archive/criminal/cybercrime/press-releases/2002/mckinnonIndict.htm
Source snippet
Department of JusticeLondon, England Hacker Indicted Under Computer Fraud and Abuse Act For Accessing Military Computers (November 12, 20...
4.
Source: oig.nasa.gov
Title: Office of Inspector General Cyber Security: The Status of Information
Link:https://oig.nasa.gov/docs/testimony062403.pdf
Source snippet
NASA Office of Inspector GeneralCyber Security: The Status of InformationJune 13, 2025...
Published: June 13, 2025
5.
Source: gao.gov
Title: gao 23 105084
Link:https://www.gao.gov/products/gao-23-105084
Source snippet
DOD Cybersecurity: Enhanced Attention Needed to Ensure Cyber Incidents Are Appropriately Reported and Shared | U.S. GAONovember 14, 2022...
Published: November 14, 2022
6.
Source: files.gao.gov
Link:https://files.gao.gov/reports/GAO-26-107922/index.html
Source snippet
gao.govGAO-26-107922, INSPECTORS GENERAL INTEGRITY COMMITTEE: Strengthened Oversight and Policy Needed to Ensure Consistent Investigation...
7.
Source: files.gao.gov
Link:https://files.gao.gov/reports/GAO-26-107861/index.html
Source snippet
gao.govGAO-26-107861, INDUSTRIAL SECURITY: Improved Risk Management and Stakeholder Engagement Needed to Help DOD Address Mission GapsApr...
8.
Source: files.gao.gov
Link:https://files.gao.gov/reports/GAO-26-107100/index.html
9.
Source: gao.gov
Title: gao 25 108138
Link:https://www.gao.gov/products/gao-25-108138
10.
Source: gao.gov
Title: gao 22 104746
Link:https://www.gao.gov/products/gao-22-104746
11.
Source: oig.nasa.gov
Link:https://oig.nasa.gov/office-of-inspector-general-oig/ig-21-019/
12.
Source: oig.nasa.gov
Link:https://oig.nasa.gov/office-of-inspector-general-oig/ig-21-011/
13.
Source: oig.nasa.gov
Link:https://oig.nasa.gov/office-of-inspector-general-oig/ig-12-017/
14.
Source: justice.gov
Link:https://www.justice.gov/archive/criminal/cybercrime/press-releases/2002/mckinnonIndict2.htm
15.
Source: gao.gov
Link:https://www.gao.gov/products/t-imtec
16.
Source: GOV.UK
Title: www.gov.uk Latest on Gary [Mc Kinnon case]({{ ‘mc-kinnon-case/’ | relative_url }})
Link:https://www.gov.uk/government/news/latest-on-gary-mckinnon-case
Additional References
17.
Source: oversight.gov
Title: Cybersecurity Incident Response Maturity Assessment | Oversight.gov
Link:https://www.oversight.gov/reports/audit/cybersecurity-incident-response-maturity-assessment
Source snippet
March 30, 2026 — Brought to you by the Council of the Inspectors General on Integrity and Efficiency CYBERSECURITY INCIDENT RESPONSE MATU...
Published: March 30, 2026
18.
Source: oig.doc.gov
Link:https://www.oig.doc.gov/Pages/Fundamental-Deficiencies-in-OS-Cybersecurity-Incident-Response-Program-Increase-the-Risk-of-Cyberattacks.aspx
19.
Source: doioig.gov
Link:https://www.doioig.gov/reports/evaluation/interior-incident-response-program-calls-improvement
20.
Source: youtube.com
Title: Ancient Aliens: Hacking NASA Secrets (Season 12, Episode 9) | History
Link:https://www.youtube.com/watch?v=20rWFDfh68Y
Source snippet
Gary McKinnon Case (Interview from 2009)...
21.
Source: youtube.com
Title: The Man Who Hacked the U.S. Government
Link:https://www.youtube.com/watch?v=ND0zQX1rGdg
Source snippet
Hacking for UFOs and fighting for his life. Who is Gary McKinnon? | NordVPN...
22.
Source: youtube.com
Title: UK hacker’s extradition to US blocked
Link:https://www.youtube.com/watch?v=v4Js8DF80HY
Source snippet
Ancient Aliens: Hacking NASA Secrets (Season 12, Episode 9) | History...
23.
Source: youtube.com
Title: Hacking for UFOs and fighting for his life. Who is Gary Mc Kinnon? | Nord VPN
Link:https://www.youtube.com/watch?v=OImdnvQx7sQ
Source snippet
UK hacker's extradition to US blocked...
24.
Source: dodig.mil
Title: evaluation of the dods response to anomalous health incidents or havana syndrom
Link:https://www.dodig.mil/reports.html/article/3326777/evaluation-of-the-dods-response-to-anomalous-health-incidents-or-havana-syndrom/
25.
Source: muckrock.com
Title: Gary Mc Kinnon damage assessment/lessons learned • Muck Rock
Link:https://www.muckrock.com/foi/united-states-of-america-10/gary-mckinnon-damage-assessmentlessons-learned-47980/
26.
Source: gao.justia.com
Title: operation desert storm osi 93 4
Link:https://gao.justia.com/department-of-defense/1993/6/operation-desert-storm-osi-93-4/